Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
Your network contains an Active Directory Domain Services (AD DS) domain named contoso.com.
You need to identify which server is the PDC emulator for the domain.
Solution: From Active Directory Domains and Trusts, you right-click Active Directory Domains and Trusts in the console tree, and then select Operations
Master.
Does this meet the goal?
Explanation
The solution described does not meet the goal because to identify the PDC emulator for the domain, one should right-click on the domain in Active Directory Users and Computers rather than Active Directory Domains and Trusts. Selecting 'Operations Masters' from there will correctly display the server holding the PDC role.
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
Your network contains an Active Directory Domain Services (AD DS) domain named contoso.com.
You need to identify which server is the PDC emulator for the domain.
Solution: From a command prompt, you run netdom.exe query fsmo.
Does this meet the goal?
Explanation
The command 'netdom query fsmo' from a command prompt can identify the PDC emulator for the domain among other FSMO roles. This meets the goal as specified.
You have an on premises Active Directory Domain Services (AD DS) domain that syncs with an Azure Active Directory (Azure AD) tenant.
You plan to implement self-service password reset (SSPR) in Azure AD.
You need to ensure that users that reset their passwords by using SSPR can use the new password resources in the AD DS domain.
What should you do?
- A. Deploy the Azure AD Password Protection proxy service to the on premises network.
- B. Run the Microsoft Azure Active Directory Connect wizard and select Password writeback. Correct
- C. Grant the Change password permission for the domain to the Azure AD Connect service account.
- D. Grant the impersonate a client after authentication user right to the Azure AD Connect service account.
Explanation
Password writeback must be enabled to ensure that password changes made via self-service password reset in Azure AD are synchronized back to the on-premises Active Directory Domain Services (AD DS). This ensures users can use their new passwords for resources within the AD DS domain.
Your network contains an Active Directory Domain Services (AD DS) forest named contoso.com.
You create the resources shown in the following table.
| Name | Type | Member of | In organizational unit (OU) |
|--------|-----------------|-----------|-----------------------------|
| User1 | User | None | Contoso.com\OU1 |
| User2 | User | Group1 | Contoso.com\OU1 |
| User3 | User | Group1 | Contoso.com\OU2 |
| Group1 | Group | None | Contoso.com\OU1 |
| Comp1 | Client computer | Group1 | Contoso.com\OU2 |
You create the Group Policy Objects (GPOs) shown in the following table.
| Name | Linked to |
|------|-----------|
| GPO1 | OU1 |
| GPO2 | OU2 |
You configure the Group Policy Preferences shown in the following table.
| GPO | Setting |
|------|---------|
| GPO1 | Computer Configuration: Add a shortcut named Link1 to the desktop<br>User Configuration: Add a shortcut named Link2 to the desktop |
| GPO2 | Computer Configuration: Add a shortcut named Link3 to the desktop<br>User Configuration: Add a shortcut named Link4 to the desktop |
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Explanation
Statement 1 (No): Link4 comes from the User Configuration of GPO2, which is linked to OU2. User settings follow the location of the user object, and User1 is in OU1, so User1 receives GPO1's user setting (Link2), not Link4. Because Comp1 is in OU2, it receives only GPO2's computer setting (Link3). Loopback processing is not configured, so GPO2's user settings do not apply to User1 on Comp1.
Statement 2 (Yes): User2's account is in OU1, so GPO1's User Configuration applies whenever User2 signs in, including on Comp1, and the Link2 shortcut appears.
Statement 3 (No): User3's account is in OU2, so User3 receives GPO2's user setting (Link4), not Link2. Membership in Group1 does not matter: a GPO linked to an OU applies to the user and computer objects in that OU, not to members of a group that happens to be stored there.
You create a new Azure subscription.
You plan to deploy Azure Active Directory Domain Services (Azure AD DS) and Azure virtual machines.
You need to ensure that the virtual machines can join to Azure AD DS.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Explanation
1. Create an Azure virtual network: the managed domain and the VMs that will join it need a virtual network and subnet to be deployed into, and the Azure AD DS instance is placed in that network.
2. Create an Azure AD DS instance: during creation you select the virtual network and subnet, and the service deploys two managed domain controllers there.
3. Modify the settings of the Azure virtual network: after deployment, update the virtual network's DNS servers to the IP addresses of the managed domain controllers, so that VMs in the network can find the domain and join it.
Installing the AD DS role, running the AD DS installation wizard, and installing Azure AD Connect are not needed, because Azure AD DS is a managed service and synchronizes from the tenant automatically.
You have an Azure Active Directory Domain Services (Azure AD DS) domain.
You create a new user named Admin1.
You need Admin1 to deploy custom Group Policy settings to all the computers in the domain. The solution must use the principle of least privilege.
What should you include in the solution? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Explanation
Add Admin1 to the following group: AAD DC Administrators — In an Azure AD DS managed domain, Microsoft owns and operates the domain controllers, so no tenant account can ever join the true Domain Admins or Enterprise Admins roles; AAD DC Administrators is the delegated administrative group Azure AD DS provides, and it grants exactly the rights needed to manage the two built-in GPOs and the AADDC organizational units. Domain Admins and Group Policy Creator Owners are not available for membership changes in a managed domain, so neither can be used to delegate this task.
Instruct Admin1 to apply the custom Group Policy settings by: Modifying AADDC Computers GPO — Azure AD DS pre-creates the AADDC Computers and AADDC Users GPOs linked to the corresponding OUs, and every domain-joined machine is placed in the AADDC Computers OU, so editing that GPO applies the custom settings to all computers in the domain and is the least-privileged option available to a member of AAD DC Administrators. Creating a new GPO and linking it to the domain root is not possible because AAD DC Administrators lacks link and create rights at the domain level, and the Default Domain Policy is managed by the service and cannot be modified by tenant administrators.
Your network contains a single domain Active Directory Domain Services (AD DS) forest named contoso.com. The forest contains a single Active Directory site.
You plan to deploy a read only domain controller (RODC) to a new datacenter on a server named Server1. A user named User1 is a member of the local
Administrators group on Server1.
You need to recommend a deployment plan that meets the following requirements:
✑ Ensures that a user named User1 can perform the RODC installation on Server1
✑ Ensures that you can control the AD DS replication schedule to the Server1
✑ Ensures that Server1 is in a new site named RemoteSite1
Uses the principle of least privilege
Which three actions should you recommend performing in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Explanation
1. Create a site and a subnet. Creating RemoteSite1 with a subnet for the new datacenter places Server1 in its own site. When you create a site, you must add it to a site link. Replication to the site then follows that site link's schedule, so you can control when AD DS replicates to Server1. The existing DEFAULTIPSITELINK can be used for this, so creating a separate site link is not required.
2. Pre-create an RODC account. A Domain Admin pre-stages the RODC computer account in RemoteSite1, chooses the replication settings, and names User1 as the delegated administrator. This lets a user who is not a domain administrator finish the installation.
3. Instruct User1 to run the Active Directory Domain Services installation Wizard on Server1. User1 is a local administrator on Server1 and the delegated administrator of the pre-created account, so User1 can attach the server to the account and complete the RODC installation. Adding User1 to Contoso\Administrators would also work, but it grants far more rights than needed, which breaks the principle of least privilege.
Your network contains an Active Directory Domain Services (AD DS) domain. The network also contains 20 domain controllers, 100 member servers, and 100 client computers.
You have a Group Policy Object (GPO) named GPO1 that contains Group Policy preferences.
You plan to link GPO1 to the domain.
You need to ensure that the preference in GPO1 apply only to domain member servers and NOT to domain controllers or client computers. All the other Group
Policy settings in GPO1 must apply to all the computers. The solution must minimize administrative effort.
Which type of item level targeting should you use?
- A. Domain
- B. Operating System Correct
- C. Security Group
- D. Environment Variable
Explanation
An Operating System targeting item can match on the computer role of the processing computer: Workstation, Member Server, or Domain Controller. Setting Computer role to Member Server makes the preference items in GPO1 apply only to domain member servers, while the other settings in GPO1 still apply to every computer the GPO is linked to. Nothing has to be created or maintained. Security Group targeting would need a group of member servers that you create and keep current, which is more administrative effort. Domain targeting cannot tell the computer types apart, because all computers are in the same domain. Environment Variable targeting would need a variable to be set on each member server first.
You deploy a new Active Directory Domain Services (AD DS) forest named contoso.com. The domain contains three domain controllers named DC1, DC2, and
DC3.
You rename Default-First-Site-Name as Site1.
You plan to ship DC1, DC2, and DC3 to datacenters in different locations.
You need to configure replication between DC1, DC2, and DC3 to meet the following requirements:
✑ Each domain controller must reside in its own Active Directory site.
✑ The replication schedule between each site must be controlled independently.
✑ Interruptions to replication must be minimized.
Which three actions should you perform in sequence in the Active Directory Sites and Services console? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Explanation
First create Site2 and Site3 and move DC2 and DC3 into them, so that each domain controller is in its own site. New sites are added to DEFAULTIPSITELINK, so at that point all three sites share one link and one schedule. Intersite replication schedules are set on site links, so create an additional site link that contains Site1 and Site2, and then remove Site2 from DEFAULTIPSITELINK. Site1 and Site2 then replicate over the new link, Site1 and Site3 over DEFAULTIPSITELINK, and each link has its own schedule. The connection objects are left to the KCC: it creates and maintains them automatically and builds new ones when a domain controller or link fails, which keeps interruptions to a minimum. Connection objects you create manually are not managed or optimized by the KCC, and their intersite schedule comes from the site link anyway.
Your network contains an Active Directory Domain Services (AD DS) forest named contoso.com. The root domain contains the domain controllers shown in the following table.
| Name | FSMO role |
|---|---|
| DC1 | Domain naming master |
| DC2 | RID master |
| DC3 | PDC emulator |
| DC4 | Schema master |
| DC5 | Infrastructure master |
A failure of which domain controller will prevent you from creating application partitions?
- A. DC1 Correct
- B. DC2
- C. DC3
- D. DC4
- E. DC5
Explanation
The domain naming master is the only domain controller that can make changes to the forest-wide Partitions container in the configuration naming context. Creating an application directory partition adds a cross-reference object there, so the domain naming master must be available. DC1 holds the domain naming master role, so a failure of DC1 prevents you from creating application partitions. The schema master (DC4) is only needed for schema changes, and the RID master, PDC emulator and infrastructure master are domain-wide roles that play no part in creating partitions.
Your network contains an on-premises Active Directory Domain Services (AD DS) domain named contoso.com. The domain contains the objects shown in the following table.
| Name | Type |
|---|---|
| User1 | User |
| Group1 | Universal security group |
| Group2 | Domain local security group |
| Computer1 | Computer |
You plan to sync contoso.com with an Azure Active Directory (Azure AD) tenant by using Azure AD Connect.
You need to ensure that all the objects can be used in Conditional Access policies.
What should you do?
- A. Select the Configure Hybrid Azure AD join option. Correct
- B. Change the scope of Group1 and Group2 to Global.
- C. Clear the Configure device writeback option.
- D. Change the scope of Group2 to Universal.
Explanation
Selecting the Configure Hybrid Azure AD join option allows on-premises computer accounts to register with Azure AD, enabling their use in Conditional Access policies. This ensures that all objects can be utilized within Azure AD's Conditional Access framework.
Your network contains a multi-site Active Directory Domain Services (AD DS) forest. Each Active Directory site is connected by using manually configured site links and automatically generated connections.
You need to minimize the convergence time for changes to Active Directory.
What should you do?
- A. For each site link, modify the replication schedule.
- B. For each site links, modify the site link costs.
- C. Create a site link bridge that contains all the site links.
- D. For each site link, modify the options attribute. Correct
Explanation
Modifying the options attribute for each site link to enable change notification allows domain controllers to immediately notify each other of changes, thereby minimizing convergence time.
You deploy a single-domain Active Directory Domain Services (AD DS) forest named contoso.com.
You deploy five servers to the domain. You add the servers to a group named ITFarmHosts.
You plan to configure a Network Load Balancing (NLB) cluster named NLBCluster.contoso.com that will contain the five servers.
You need to ensure that the NLB service on the nodes of the cluster can use a group managed service account (gMSA) to authenticate.
Which three PowerShell cmdlets should you run in sequence? To answer, move the appropriate cmdlets from the list of cmdlets to the answer area and arrange them in the correct order.
Explanation
Add-KdsRootKey creates the Key Distribution Services root key, which the domain controllers need before any group managed service account (gMSA) can be created. New-ADServiceAccount then creates the gMSA, with -PrincipalsAllowedToRetrieveManagedPassword set to the ITFarmHosts group so the five NLB nodes can retrieve its password. Finally, Install-ADServiceAccount is run on each node to install the gMSA locally so the NLB service can use it.
The servers are already in ITFarmHosts, so Add-ADGroupMember is not needed. Set-KdsConfiguration changes KDS algorithm settings and is not required, and Add-ADComputerServiceAccount links a standalone managed service account to one computer, which does not apply to a gMSA used by several servers.
You have an on-premises Active Directory Domain Services (AD DS) domain that syncs with an Azure Active Directory (Azure AD) tenant.
You have several Windows 10 devices that are Azure AD hybrid-joined.
You need to ensure that when users sign in to the devices, they can use Windows Hello for Business.
Which optional feature should you select in Azure AD Connect?
- A. Device writeback Correct
- B. Group writeback
- C. Azure AD app and attribute filtering
- D. Password writeback
- E. Directory extension attribute sync
Explanation
Device writeback is necessary for Windows Hello for Business to function correctly on Azure AD hybrid-joined devices. This feature ensures that the on-premises Active Directory Domain Services (AD DS) domain receives information about device registration states from Azure AD, which is essential for Windows Hello for Business.
Your network contains an Active Directory Domain Services (AD DS) forest named contoso.com. The forest contains a child domain named east.contoso.com.
In the contoso.com domain, you create two users named Admin1 and Admin2.
You need to ensure that the users can perform the following tasks:
✑ Admin1 can create and manage Active Directory sites.
✑ Admin2 can deploy domain controllers to the east.contoso.com domain.
The solution must use the principle of least privilege.
To which group should you add each user? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Hot Area:
Explanation
Admin1: Contoso\Domain Admins — Active Directory sites, subnets, and site links live in the Configuration naming context, which is mastered in the forest root domain (contoso.com), and the root domain's Domain Admins hold the rights over that partition needed to create and manage the site topology. Contoso\Enterprise Admins would also work but violates least privilege, since it grants full control over every domain in the forest; the East groups have no authority over the forest-wide Configuration partition.
Admin2: East\Domain Admins — promoting an additional domain controller into an existing domain requires membership in the Domain Admins group of that specific domain, so Admin2 needs Domain Admins in east.contoso.com and nothing broader. Contoso\Enterprise Admins would permit the promotion as well but hands Admin2 forest-wide control, and East\Administrators (the domain's built-in group) is not the membership domain controller promotion validates when adding a DC to an existing domain.
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
Your network contains an Active Directory Domain Services (AD DS) forest. The forest contains three Active Directory sites named Site1, Site2, and Site3. Each site contains two domain controllers. The sites are connected by using DEFAULTIPSITELINK.
You open a new branch office that contains only client computers.
You need to ensure that the client computers in the new office are primarily authenticated by the domain controllers in Site1.
Solution: You create an organization unit (OU) that contains the client computers in the branch office. You configure the Try Next Closest Site Group Policy Object
(GPO) setting in a GPO that is linked to the new OU.
Does this meet the goal?
Explanation
The solution does not meet the goal. Clients choose a domain controller by using their Active Directory site, and that site is determined by which AD subnet object contains the client's IP address. The new branch office subnet is not defined in AD DS, so the clients belong to no site and are authenticated by any domain controller the DC Locator returns. The Try Next Closest Site Group Policy setting only lets a client fall back to the next closest site (by site link cost) when no domain controller in its own site is available. It cannot make clients prefer Site1, and all three sites share DEFAULTIPSITELINK with the same cost anyway. To meet the goal, create a subnet object for the branch office and associate it with Site1.
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
Your network contains an Active Directory Domain Services (AD DS) forest. The forest contains three Active Directory sites named Site1, Site2, and Site3. Each site contains two domain controllers. The sites are connected by using DEFAULTIPSITELINK.
You open a new branch office that contains only client computers.
You need to ensure that the client computers in the new office are primarily authenticated by the domain controllers in Site1.
Solution: You create a new site named Site4 and associate Site4 to DEFAULTSITELINK.
Does this meet the goal?
Explanation
Creating a new site named Site4 and associating it to DEFAULTIPSITELINK does not ensure that client computers in the new office are primarily authenticated by domain controllers in Site1. A new site link with lower cost between Site4 and Site1 must be created to prioritize authentication from Site1.
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
Your network contains an Active Directory Domain Services (AD DS) forest. The forest contains three Active Directory sites named Site1, Site2, and Site3. Each site contains two domain controllers. The sites are connected by using DEFAULTIPSITELINK.
You open a new branch office that contains only client computers.
You need to ensure that the client computers in the new office are primarily authenticated by the domain controllers in Site1.
Solution: You configure the Try Next Closest Site Group Policy Object (GPO) setting in a GPO that is linked to Site1.
Does this meet the goal?
Explanation
No. The Try Next Closest Site setting only changes how a client picks a domain controller when none is available in its own site: it then tries the next closest site based on site-link cost instead of any DC in the domain. It does not make Site1 the primary authentication site. In addition, a GPO linked to Site1 applies only to computers whose IP subnet belongs to Site1, so the branch-office clients would not even receive the setting.
To meet the goal, associate the branch office's IP subnet with Site1 (or create a new site for the branch office and connect it to Site1 through a site link with a lower cost than the links to Site2 and Site3) so that the DC Locator sends the clients to the Site1 domain controllers.
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
Your network contains an Active Directory Domain Services (AD DS) domain named contoso.com.
You need to identify which server is the PDC emulator for the domain.
Solution: From Active Directory Sites and Services, you right-click Default-First-Site-Name in the console tree, and then select Properties.
Does this meet the goal?
Explanation
The provided solution does not meet the goal because it describes navigating to Active Directory Sites and Services and viewing properties of Default-First-Site-Name, which does not identify the PDC emulator. To correctly identify the PDC emulator, one should use 'Active Directory Users and Computers' and navigate through domain operations masters.
Your network contains a single-domain Active Directory Domain Services (AD DS) forest named contoso.com. The forest contains the servers shown in the following exhibit table.
| Name | Description |
|---|---|
| DC1 | Domain controller |
| Server1 | Member server |
You plan to install a line-of-business (LOB) application on Server1. The application will install a custom Windows service.
A new corporate security policy states that all custom Windows services must run under the context of a group managed service account (gMSA). You deploy a root key.
You need to create, configure, and install the gMSA that will be used by the new application.
Which two actions should you perform? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point
- A. On Server1, run the setspn command.
- B. On DC1, run the New-ADServiceAccount cmdlet. Correct
- C. On Server1, run the Install-ADServiceAccount cmdlet. Correct
- D. On Server1, run the Get-ADServiceAccount cmdlet.
- E. On DC1, run the Set-ADComputer cmdlet.
- F. On DC1, run the Install-ADServiceAccount cmdlet.
Explanation
To create a group managed service account (gMSA), the New-ADServiceAccount cmdlet must be run on DC1. To install and configure this gMSA on Server1 where the LOB application will reside, the Install-ADServiceAccount cmdlet should be executed.
Your network contains three Active Directory Domain Services (AD DS) forests as shown in the following exhibit.
The network contains the users shown in the following table.
The network contains the security groups shown in the following table.
For each of the following statements, select Yes if the statement is true. Otherwise. select No.
NOTE: Each correct selection is worth one point.
Hot Area:
| Name | Domain |
| --- | --- |
| User1 | east.contoso.com |
| User2 | fabrikam.com |
| Name | Type | Domain |
| --- | --- | --- |
| Group1 | Domain local | west.adatum.com |
| Group2 | Universal | contoso.com |
| Group3 | Universal | east.contoso.com |
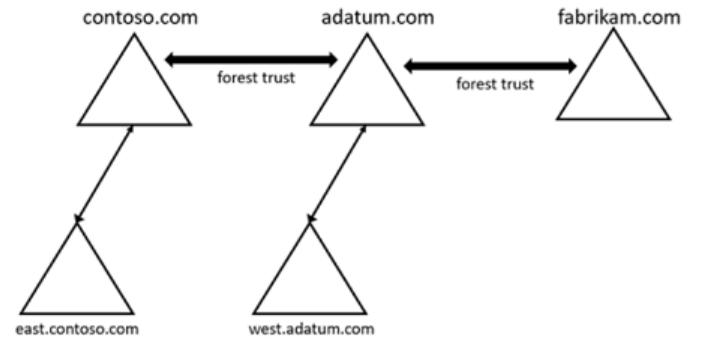
Explanation
Statement 1 (Yes): Group1 is a domain local group in west.adatum.com. A domain local group can contain accounts from any trusted domain. The two-way forest trust between contoso.com and adatum.com covers every domain in both forests, so User1 from east.contoso.com can be added to Group1.
Statement 2 (No): Group3 is a universal group in east.contoso.com. A universal group can contain accounts only from domains in its own forest. User2 belongs to fabrikam.com, a separate forest, so User2 cannot be added to Group3.
Statement 3 (No): fabrikam.com has a forest trust with adatum.com only. A forest trust cannot be extended to a third forest, so the trusts contoso.com-adatum.com and adatum.com-fabrikam.com do not create a trust between contoso.com and fabrikam.com. With no trust path, fabrikam.com cannot resolve Group2 from contoso.com, and Group2 cannot be granted permissions on resources in fabrikam.com.
Your network contains an Active Directory Domain Services (AD DS) forest named contoso.com. The forest root domain contains a server named server1.contoso.com.
A two-way forest trust exists between the contoso.com forest and an AD DS forest named fabrikam.com. The fabrikam.com forest contains 10 child domains.
You need to ensure that only the members of a group named fabrikam\Group1 can authenticate to server1.contoso.com.
What should you do first?
- A. Add fabrikam\Group1 to the local Users group on server1.contoso.com.
- B. Enable SID filtering for the trust.
- C. Enable Selective authentication for the trust. Correct
- D. Change the trust to a one-way external trust.
Explanation
Selective authentication restricts access over an external or forest trust to only those users in a trusted domain who have been explicitly given authentication permissions. This feature is necessary to ensure that only members of fabrikam\Group1 can authenticate to server1.contoso.com.
Your network contains an Active Directory forest. The forest contains two domains named contoso.com and east.contoso.com and the servers shown in the following table.
| Name | Domain | Configuration |
|---|---|---|
| DC1 | contoso.com | Domain controller |
| Server1 | contoso.com | Member server |
| DC2 | east.contoso.com | Domain controller |
| Server2 | east.contoso.com | Member server |
Contoso.com contains a user named User1.
You add User1 to the built-in Backup Operators group in contoso.com.
Which servers can User1 back up?
- A. DC1 only Correct
- B. Server1 only
- C. DC1 and DC2 only
- D. DC1 and Server1 only
- E. DC1, DC2, Server1, and Server2
Explanation
The Backup Operators group in Active Directory is a built-in (Builtin container) domain local group. Its membership is stored in the domain database, so it takes effect only on the domain controllers of that domain. Microsoft documents that this group can perform backup and restore operations on domain controllers. Member servers such as Server1 do not use the domain's Builtin groups. Each member server has its own local Backup Operators group in its SAM database, and User1 has not been added to that group. The group also has no effect in another domain, so DC2 and Server2 in east.contoso.com are excluded. User1 can therefore back up DC1 only.
Your network contains an Azure Active Directory Domain Services (Azure AD DS) domain named contoso.com.
You need to configure a password policy for the local user accounts on the Azure virtual machines joined to contoso.com.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Explanation
Sign in by using a user account that is a member of the: AAD DC Administrators group. In an Azure AD DS (Microsoft Entra Domain Services) managed domain, Microsoft runs the domain controllers, and you do not get Domain Admins or Enterprise Admins rights. Members of the AAD DC Administrators group have Group Policy administration rights in the managed domain and can edit the built-in GPOs or create custom ones. Membership in Administrators or Domain Admins is not available to you for this purpose.
Use a Group Policy Object (GPO) linked to the: AADDC Computers organizational unit (OU). Password policy is an Account Policies setting under Computer Configuration. A domain GPO linked to an OU applies these settings to the local accounts of the computers in that OU. VMs joined to the managed domain are placed in the AADDC Computers container, which has its own built-in GPO where Account Policies can be customized. A GPO linked to AADDC Users would target user objects, where computer password settings have no effect. The Computers container is not where Azure AD DS places domain-joined VMs.
Your network contains an Active Directory Domain Services (AD DS) forest. The forest contains three domains. Each domain contains 10 domain controllers.
You plan to store a DNS zone in a custom Active Directory partition.
You need to create the Active Directory partition for the zone. The partition must replicate to only four of the domain controllers.
What should you use?
- A. Windows Admin Center
- B. DNS Manager
- C. Active Directory Sites and Services
- D. ntdsutil.exe Correct
Explanation
The ntdsutil.exe tool is used to create custom Active Directory partitions. This tool allows for the creation and management of AD DS partitions, including specifying replication settings.
Your network contains a single domain Active Directory Domain Services (AD DS) forest named contoso.com. The forest contains a single Active Directory site.
You plan to deploy a read only domain controller (RODC) to a new datacenter on a server named Server1. A user named User1 is a member of the local Administrators group on Server1.
You need to recommend a deployment plan that meets the following requirements:
• Ensures that a user named User1 can perform the RODC installation on Server1
• Ensures that Server1 is in a new site named RemoteSite1
• Uses the principle of least privilege
Which three actions should you recommend performing in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Explanation
1. Create a site and a subnet: Server1 must end up in a new site named RemoteSite1. Staging an RODC account asks you to pick an existing site (the Select a Site page, or -SiteName in Add-ADDSReadOnlyDomainControllerAccount, which does not create sites), so RemoteSite1 and its subnet must exist first. The forest already has the DEFAULTIPSITELINK site link, so you do not need to create a new one.
2. Pre-create an RODC account: a Domain Admin stages the RODC computer account in RemoteSite1 and names User1 as the delegated administrator, the group or user allowed to attach the server to the account.
3. Instruct User1 to run the Active Directory Domain Services installation Wizard on Server1: User1 completes the second stage (attach to the existing RODC account) with only the delegated rights. Adding User1 to Contoso\Administrators would give far more privilege than needed, which breaks the least-privilege requirement.
Your network contains an Active Directory domain named contoso.com. The domain contains the computers shown in the following table.
| Name | Operating system |
|---|---|
| Computer1 | Windows 11 |
| Server1 | Windows Server 2016 |
| Server2 | Windows Server 2019 |
| Server3 | Windows Server 2022 |
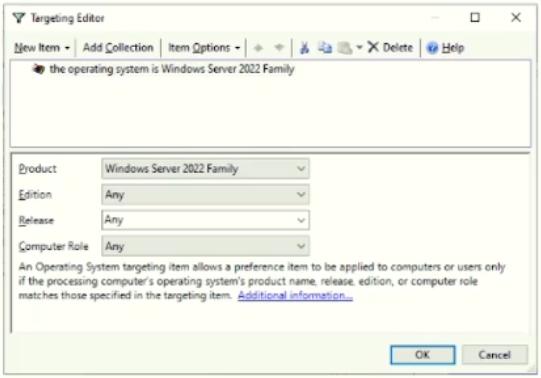
On Server3, you create a Group Policy Object (GPO) named GPO1 and link GPO1 to contoso.com. GPO1 includes a shortcut preference named Shortcut1 that has item-level targeting configured as shown in the following exhibit.
To which computer will Shortcut1 be applied?
- A. Server3 only Correct
- B. Computer1 and Server3 only
- C. Server2 and Server3 only
- D. Server1, Server2, and Server3 only
Explanation
The item-level targeting is configured for the Windows Server 2022 Family. Only Server3, which runs Windows Server 2022, matches this criterion. Therefore, Shortcut1 will be applied to Server3 only.
Your network contains a multi-site Active Directory Domain Services (AD DS) forest. Each Active Directory site is connected by using manually configured site links and automatically generated connections.
You need to minimize the latency for changes to Active Directory.
What should you do?
- A. For each site links, modify the site link costs.
- B. Create a site link bridge that contains all the site links.
- C. For each site link, modify the options attribute. Correct
- D. For each site link, modify the replication schedule.
Explanation
Modifying the options attribute for each site link allows enabling change notification, which reduces replication latency by immediately notifying other domain controllers of changes. This immediate notification minimizes delay in Active Directory change propagation.
Your network contains two Active Directory Domain Services (AD DS) forests named contoso.com and fabrikam.com. Contoso.com contains three child domains named amer.contoso.com, apac.contoso.com, and emea.contoso.com. Fabrikam.com contains a child domain named apac.fabrikam.com. A bidirectional forest trust exists between contoso.com and fabrikam.com.
You need to provide users in the contoso.com forest with access to the resources in the fabrikam.com forest. The solution must meet the following requirements:
• Users in contoso.com must only be added directly to groups in the contoso.com forest.
• Permissions to access the resources in fabrikam.com must only be granted directly to groups in the fabrikam.com forest.
• The number of groups must be minimized.
Which type of groups should you use to organize the users and to assign permissions? To answer, drag the appropriate group types to the correct requirements. Each group may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
Explanation
Organize users: Universal. A universal group can contain user accounts from any domain in the same forest, so one universal group in contoso.com can hold users from contoso.com, amer.contoso.com, apac.contoso.com and emea.contoso.com. Global groups can contain accounts only from their own domain, so you would need four of them. A universal group can be a member of domain local groups in a trusting forest.
Assign permissions: Domain local. A domain local group can contain accounts and groups from trusted forests, and it is used to grant permissions to resources in its own domain. Create domain local groups in fabrikam.com, add the contoso.com universal group to them and grant them the permissions, so users are only added to contoso.com groups and permissions are only granted to fabrikam.com groups.
Your network contains two Active Directory forests and a domain trust as shown in the following exhibit.
The domain trust has the following configurations:
• Name: adatum.com
• Type: External
• Direction: One-way, outgoing
• Outgoing trust authentication level: Domain-wide authentication
The forests contain the users shown in the following table.
| Name | Domain |
| --- | --- |
| User1 | adatum.com |
| User2 | contoso.com |
| User3 | east.contoso.com |
The forests contain the network shares shown in the following table.
| Name | In domain |
| --- | --- |
| Share1 | adatum.com |
| Share2 | contoso.com |
| Share3 | east.contoso.com |
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
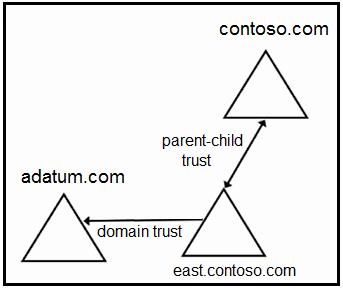
Explanation
Statement 1 (Yes): The trust is configured in east.contoso.com and is named after the other domain, adatum.com. A one-way, outgoing trust means east.contoso.com (the trusting, resource domain) trusts adatum.com (the trusted, account domain). Accounts from adatum.com can therefore be resolved and granted access to resources in east.contoso.com. User1 is in adatum.com and Share3 is in east.contoso.com, so User1 can be assigned permissions for Share3. Because the authentication level is domain-wide, no per-server Allowed to Authenticate permission is needed.
Statement 2 (No): User2 is in contoso.com and Share1 is in adatum.com. adatum.com trusts neither contoso.com nor east.contoso.com, because the trust only goes one way. An external trust is also non-transitive, so it does not reach contoso.com through the parent-child trust. User2 cannot be assigned permissions for Share1.
Statement 3 (No): User3 is in east.contoso.com and Share1 is in adatum.com. Access flows in the opposite direction to the trust: adatum.com accounts can reach east.contoso.com resources, not the other way round. To let east.contoso.com users reach adatum.com resources, adatum.com would need its own outgoing trust to east.contoso.com, or the trust would need to be two-way. User3 cannot be assigned permissions for Share1.
Your network contains an Active Directory Domain Services (AD DS) forest named contoso.com. The forest contains a child named east.contoso.com and the servers shown in the following table.
You need to create a folder for the Central Store to manage Group Policy template files for the entire forest.
What should you name the folder, and on which server should you create the folder? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
| Name | Domain | Description |
| --- | --- | --- |
| DC1 | contoso.com | Has the schema master, infrastructure master, and domain naming master roles |
| DC2 | east.contoso.com | Has the PDC emulator and RID master roles and is a global catalog server |
| Server1 | contoso.com | Has the File Server, DFS Namespaces, and DFS Replication server roles |
Explanation
Name: PolicyDefinitions — The Group Policy tools recognize the Central Store only when the folder is named PolicyDefinitions and is created under the domain's SYSVOL policies folder, for example \\contoso.com\SYSVOL\contoso.com\Policies\PolicyDefinitions. Folders named CentralDefinitions or TemplateDefinitions are ignored.
Server: DC1 and DC2 only — The Central Store is part of SYSVOL, which exists only on domain controllers, so Server1 (a member server) cannot host it. SYSVOL is replicated only to the domain controllers of its own domain, so a Central Store created in contoso.com is not available in east.contoso.com. To manage templates for the whole forest you create the folder in each domain: on DC1 for contoso.com and on DC2 for east.contoso.com.
Your network contains an Active Directory Domain Services (AD DS) domain. The domain contains the domain controllers shown in the following table.
| Name | Description |
| --- | --- |
| DC1 | Has the schema master, infrastructure master, and domain naming master roles |
| DC2 | Has the PDC emulator and RID master roles and is a global catalog server |
| DC3 | None |
You need to configure DC3 to be the authoritative time server for the domain.
Which operations master role should you transfer to DC3, and which console should you use? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Explanation
Role: PDC emulator — In an AD DS forest the domain controller holding the PDC emulator role in the forest root domain is, by default, the authoritative time source for the domain hierarchy; every other DC and domain member synchronizes its clock up the chain to it through the Windows Time service (W32Time). So making DC3 the authoritative time server means transferring the PDC emulator role to DC3. The other roles are unrelated to time: the RID master hands out RID pools, the infrastructure master maintains cross-domain object references, and the domain naming master and schema master are forest-wide roles governing domain additions and schema changes.
Console: Active Directory Users and Computers — The three domain-level operations master roles (PDC emulator, RID master and infrastructure master) are transferred in Active Directory Users and Computers: connect to DC3 with Change Domain Controller, right-click the domain, choose Operations Masters, and use the PDC tab to change the role holder. Active Directory Domains and Trusts only transfers the domain naming master, Active Directory Sites and Services manages sites and replication (no role transfer), and Active Directory Administrative Center does not provide an operations-master transfer interface.
Your on-premises network contains an Active Directory domain named contoso.com. You have an Azure AD tenant.
You plan to sync contoso.com with the Azure AD tenant by using Azure AD Connect cloud sync.
You need to create an account that will be used by Azure AD Connect cloud sync.
Which type of account should you create?
- A. system-assigned managed identity
- B. group managed service account (gMSA) Correct
- C. user
- D. InetOrgPerson
Explanation
Azure AD Connect cloud sync (now Microsoft Entra Cloud Sync) runs its provisioning agent under a group managed service account (gMSA). During agent setup you supply Domain Administrator or Enterprise Administrator credentials so the installer can create the gMSA, which appears as domain\provAgentgMSA$; you can also create a custom gMSA with the required permissions. A gMSA gives automatic password management and can be used across multiple agent servers. A regular user account or an InetOrgPerson object is not the account the agent service runs as, and a system-assigned managed identity is an Azure resource identity, not an on-premises AD account.
Your network contains an Active Directory Domain Services (AD DS) domain. The domain contains the domain controllers shown in the following table.
| Name | Description |
|---|---|
| DC1 | PDC emulator, RID master, and global catalog server |
| DC2 | Infrastructure master and domain naming master |
| DC3 | Schema master |
| RODC1 | Read-only domain controller (RODC) |
You need to ensure that if an attacker compromises the computer account of RODC1, the attacker cannot view the Employee-Number AD DS attribute.
Which partition should you modify?
- A. configuration
- B. global catalog
- C. domain
- D. schema Correct
Explanation
To stop an attribute such as Employee-Number from being available on a compromised RODC, you add it to the RODC filtered attribute set (FAS). Attributes in the FAS are not replicated to any RODC in the forest, and writable domain controllers refuse replication requests for them. The FAS is configured on the attribute's definition (the searchFlags value of its attributeSchema object), which lives in the schema partition, so the change is made in the schema (on the schema master, DC3). Marking the attribute as confidential is a recommended additional safeguard. The domain and configuration partitions hold objects and their values, not the attribute definitions, and the global catalog is not a partition you modify for this.
Your network contains an on-premises Active Directory Domain Services (AD DS) domain named contoso.com that syncs with an Azure AD tenant. The tenant contains a group named Group1 and the users shown in the following table.
| Name | In organizational unit (OU) |
| --- | --- |
| User1 | OU1 |
| User2 | OU2 |
Domain/OU filtering in Azure AD Connect is configured as shown in the Filtering exhibit. (Click the Filtering tab.)
You review the Azure AD Connect configurations as shown in the Configure exhibit. (Click the Configure tab.)
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
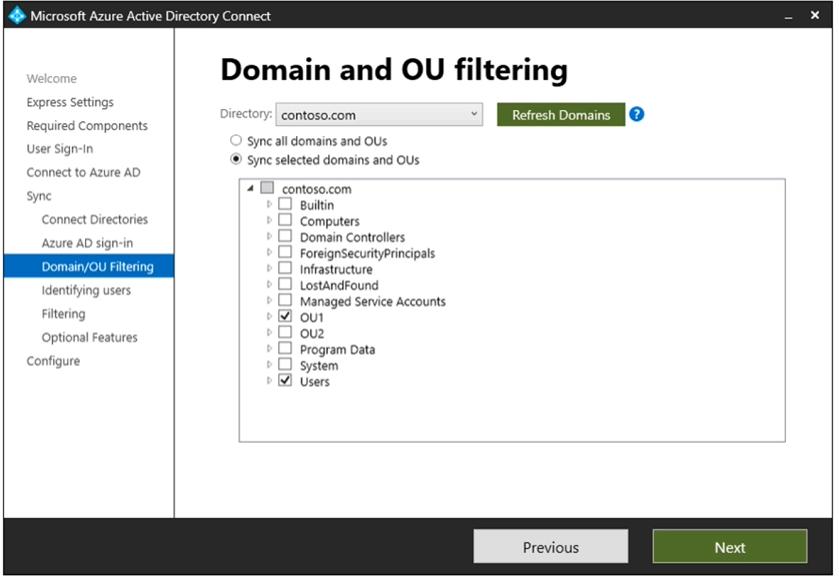
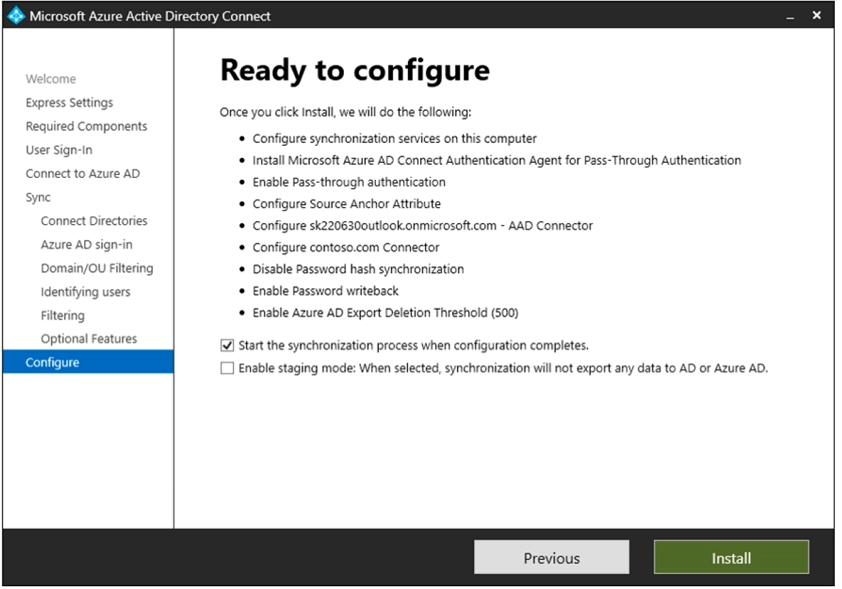
Explanation
Statement 1 (Yes): User1 is in OU1, which is selected in Domain/OU filtering, so User1 is a synchronized user. The Configure exhibit shows Enable Password writeback, which lets a synchronized user reset the password with SSPR and have the new password written back to on-premises AD DS. Pass-through authentication is integrated with self-service password management, including password writeback.
Statement 2 (Yes): The Configure exhibit shows Enable Pass-through authentication and Disable Password hash synchronization. With pass-through authentication, passwords are not stored in Azure AD; the on-premises authentication agent validates the password directly against Active Directory, so an on-premises domain controller authenticates User1 when he signs in to Exchange Online.
Statement 3 (Yes): The question states that the tenant contains Group1 and User2. OU2 is not selected for synchronization, so User2 is not a synchronized account, and Group1 is not shown as a group synchronized from AD DS. Both objects are therefore managed in Azure AD, so you can add User2 to Group1 as a member.
Your on-premises network contains an Active Directory Domain Services (AD DS) domain.
You plan to sync the domain with an Azure AD tenant by using Azure AD Connect cloud sync.
You need to meet the following requirements:
• Install the software required to sync the domain and Azure AD.
• Enable password hash synchronization.
What should you install, and what should you use to enable password hash synchronization? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Explanation
Install: The Azure AD Connect provisioning agent. Azure AD Connect cloud sync (now Microsoft Entra Cloud Sync) uses a lightweight provisioning agent (AADConnectProvisioningAgentSetup.exe) that you download from the portal and install on a domain-joined server. Azure AD Connect is the separate connect sync product, which cloud sync does not use. Active Directory Administrative Center and the AD FS Management console do not synchronize identities to Azure AD.
Use: The Azure portal. All cloud sync configuration is stored and managed in the cloud. You create the configuration in the portal (Azure AD > Azure AD Connect > Cloud sync, now the Microsoft Entra admin center) and turn on password hash synchronization there. The on-premises tools in the list have no cloud sync settings.
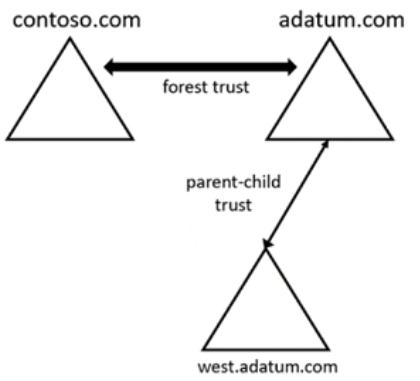
Your network contains two Active Directory Domain Services (AD DS) forests as shown in the following exhibit.
The forests contain the domain controllers shown in the following table.
You perform the following actions on DC1:
• Create a user named User1.
• Extend the schema with a new attribute named Attribute1.
To which domain controllers are User1 and Attribute1 replicated? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
| Name | Domain | Global catalog | Schema master |
| --- | --- | --- | --- |
| DC1 | adatum.com | Yes | Yes |
| DC2 | adatum.com | No | No |
| DC3 | west.adatum.com | Yes | No |
| DC4 | contoso.com | Yes | Yes |
Explanation
User1: DC2 and DC3 only — User1 is created in the adatum.com domain partition on DC1. A domain partition replicates to every domain controller in the same domain, so DC2 (adatum.com) receives a full copy. Global catalog servers in the same forest hold a partial, read-only copy of every object in the forest, so DC3 (a global catalog in west.adatum.com, a child domain of the adatum.com forest) also receives User1. DC4 is in the contoso.com forest; a forest trust allows authentication and resource access but never replicates directory objects between forests, so DC4 does not receive User1.
Attribute1: DC2 and DC3 only — The schema partition is shared by, and replicated to, every domain controller in the forest, whatever its domain or global catalog role. DC2 and DC3 are both in the adatum.com forest, so both receive Attribute1. DC4 belongs to the contoso.com forest, which has its own separate schema (DC4 is its schema master); a forest trust does not replicate schema changes, so DC4 does not receive Attribute1.
Your network contains an Active Directory Domain Services (AD DS) domain. The domain contains the resources shown in the following table.
| Name | Description |
|---|---|
| CLIENT1 | Client computer that runs Windows |
| DC1 | Domain controller |
| Server1 | File server |
| Server2 | File server |
You plan to replicate a volume from Server1 to Server2 by using Storage Replica.
You need to configure Storage Replica.
Where should you install Windows Admin Center?
- A. Server1
- B. CLIENT1 Correct
- C. DC1
- D. Server2
Explanation
For Storage Replica, Microsoft's guidance is to run Windows Admin Center from a separate management computer rather than from one of the servers taking part in replication (Server1 or Server2), so the tool stays available while the replicated servers are configured, restarted, or failed over. Installing Windows Admin Center on a domain controller is not supported, which rules out DC1. CLIENT1, a domain-joined Windows client, is the appropriate place to install Windows Admin Center and manage Storage Replica between Server1 and Server2.
You have an on-premises Active Directory Domain Services (AD DS) domain named contoso.com that syncs with Azure AD by using Azure AD Connect.
You enable password protection for contoso.com.
You need to prevent users from including the word contoso as part of their password.
What should you use?
- A. the Azure Active Directory admin center Correct
- B. Active Directory Users and Computers
- C. Synchronization Service Manager
- D. Windows Admin Center
Explanation
Azure AD Password Protection can enforce password policies that prevent users from including specific words like 'contoso' in their passwords. This feature is configured through the Azure Active Directory admin center, making it the correct choice for this scenario.
Your network contains an Active Directory Domain Services (AD DS) forest. The forest contains three domains. Each domain contains 10 domain controllers.
You plan to store a DNS zone in a custom Active Directory partition.
You need to create the Active Directory partition for the zone. The partition must replicate to only four of the domain controllers.
What should you use?
- A. Windows Admin Center
- B. Set-DnsServer
- C. New-ADObject
- D. ntdsutil.exe Correct
Explanation
ntdsutil.exe is the correct tool for creating a custom Active Directory partition and controlling its replication scope to specific domain controllers, as required by the question.
You have an Active Directory Domain Services (AD DS) domain that contains a group named Group1.
You need to create a group managed service account (gMSA) named Account1. The solution must ensure that Group1 can use Account1.
How should you complete the script? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
[Cmdlet] "Account" -DNSHostName "website.contoso.com" -[Parameter] "Group"
Explanation
Cmdlet: New-ADServiceAccount — This cmdlet creates a managed service account in AD DS; with -DNSHostName it creates a group managed service account. Install-ADServiceAccount only installs an existing gMSA on a host, Add-ADComputerServiceAccount links an existing service account to a computer object, and New-ADObject creates a generic object without the gMSA password management.
Parameter: -PrincipalsAllowedToRetrieveManagedPassword — A gMSA's password is managed by the domain controllers, and only the principals listed in this parameter can retrieve it and therefore run services as the account. Naming Group1 here lets its members use Account1. -PrincipalsAllowedToDelegateToAccount configures Kerberos resource-based constrained delegation to the account and does not allow anyone to use it, -AuthenticationPolicy assigns an authentication policy, and -Instance copies properties from an existing object.
You have an on-premises Active Directory Domain Services (AD DS) domain that syncs with Azure AD.
You deploy an app that adds custom attributes to the domain.
From Azure Cloud Shell, you discover that you cannot query the custom attributes of users.
You need to ensure that the custom attributes are available in Azure AD.
Which task should you perform from Microsoft Azure Active Directory Connect first?
- A. Configure device options
- B. Manage federation
- C. Customize synchronization options
- D. Refresh directory schema Correct
Explanation
Azure AD Connect caches the on-premises AD DS schema when it is installed, so attributes that an app adds to the schema later are not visible to it. The first task is Refresh directory schema, which reads the updated schema so the new custom attributes become available in the sync configuration. After that, you run Customize synchronization options and select the attributes on the Directory extensions page so they are synchronized to Azure AD. Configure device options handles hybrid device join and writeback, and Manage federation handles AD FS; neither makes new schema attributes available.
You have an Active Directory Domain Services (AD DS) domain that contains the domain controllers shown in the following table.
| Name | Operations master role |
|---|---|
| DC1 | Schema master |
| DC2 | Infrastructure master |
| DC3 | Domain naming master |
| DC4 | PDC emulator, RID master |
The domain contains an app named App1 that uses a custom application partition to store configuration data.
You decommission App1.
When you attempt to remove the custom application partition, the process fails.
Which domain controller is unavailable?
- A. DC1
- B. DC2
- C. DC3 Correct
- D. DC4
Explanation
The Domain Naming Master FSMO role is required to add or remove application partitions in a forest. Since the process of removing the custom application partition fails, it indicates that DC3, which holds this role, is unavailable.
Your network contains an Active Directory Domain Services (AD DS) domain.
You plan to use Active Directory Administrative Center to create a new user named User1.
Which two attributes are required to create User1? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
- A. Password
- B. Profile path
- C. User SamAccountName logon Correct
- D. Full name Correct
- E. First name
- F. User UPN logon
Explanation
When creating a new user in Active Directory Administrative Center, the 'Full name' and 'User SamAccountName logon' are mandatory fields. These attributes are essential for uniquely identifying and logging on the user within the domain.
Your on-premises network contains an Active Directory Domain Services (AD DS) domain. The domain contains the servers shown in the following table.
The domain controllers do NOT have internet connectivity.
You plan to implement Azure AD Password Protection for the domain.
You need to deploy Azure AD Password Protection agents. The solution must meet the following requirements:
• All Azure AD Password Protection policies must be enforced.
• Agent updates must be applied automatically.
• Administrative effort must be minimized.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
| Name | Description |
| --- | --- |
| DC1 | Domain naming master, PDC emulator, and RID master |
| DC2 | Schema master and infrastructure master |
| RODC1 | Read-only domain controller (RODC) |
| Server1 | Azure AD Connect server |
| Server2 | Azure AD Application Proxy connector |
Explanation
Install the Azure AD Password Protection agent on: DC1 and DC2 only. Passwords are checked by whichever writable domain controller processes the change or reset, so every writable DC needs the DC agent for the policy to be enforced everywhere. RODCs do not process or store password changes; they forward them to a writable DC. Microsoft states that the DC agent does not have to be installed on RODCs, so leaving RODC1 out also keeps effort down.
Install the Azure AD Password Protection Proxy on: Server1. The proxy downloads the policy and banned-password lists from Azure AD, so it needs internet access. The domain controllers have none, and the proxy is not supported on an RODC (on a writable DC it is meant for testing only). The proxy upgrades itself automatically through the Azure AD Connect Agent Updater service. Azure AD Application Proxy installs a different, incompatible version of that updater, and Microsoft says never to install both on the same machine because the updater can then no longer get updates. That rules out Server2. Server1, a member server with internet access, meets every requirement.
Your on-premises network contains a single-domain Active Directory Domain Services (AD DS) forest. You have an Azure AD tenant named contoso.com. The AD DS forest syncs with the Azure AD tenant by using Azure AD Connect.
You need to ensure that users in the forest that have a custom attribute of NoSync are excluded from synchronization.
How should you configure the Azure AD Connect cloudFiltered attribute, and which tool should you use? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Explanation
Attribute: True — cloudFiltered is the reserved attribute the Azure AD Connect sync engine checks on each metaverse/connector-space object, and setting it to True marks that object as filtered so it is never exported to Azure AD; you would therefore write a rule that evaluates the custom NoSync attribute and sets cloudFiltered = True for matching users. Null is the value that means "not filtered" (the object syncs normally), and Microsoft's guidance is to use True or NULL only — never False — because an explicit False can conflict with other rules that try to filter the same object.
Tool: Synchronization Rules Editor — cloudFiltered is not an Active Directory attribute you can stamp on the user object; it only exists inside the Azure AD Connect sync engine, so it must be populated by a custom inbound synchronization rule with a scoping filter and an attribute-flow expression, which is authored in the Synchronization Rules Editor that ships with Azure AD Connect. ADSI Edit only edits real AD DS attributes and cannot create sync rules, and the Azure AD Connect wizard supports only domain-, OU-, and group-based filtering, not attribute-based filtering on a custom attribute.
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
Your network contains an Active Directory Domain Services (AD DS) forest. The forest contains three Active Directory sites named Site1, Site2, and Site3. Each site contains two domain controllers. The sites are connected by using DEFAULTIPSITELINK.
You open a new branch office that contains only client computers.
You need to ensure that the client computers in the new office are primarily authenticated by the domain controllers in Site1.
Solution: You create a new site named Site4 and associate Site4 to DEFAULTIPSITELINK.
Does this meet the goal?
Explanation
No. All three sites, and now Site4, are on DEFAULTIPSITELINK with the same cost, so nothing makes Site1 closer to Site4 than Site2 or Site3. A site that has no domain controllers is covered through automatic site coverage by the domain controllers in the site(s) with the lowest site link cost to it; with equal costs, the domain controllers in Site2 and Site3 can register for Site4 just as Site1's can, so clients are not primarily authenticated by Site1. Site4 also needs a subnet object for the branch office IP range, otherwise the clients are not mapped to any site. To meet the goal, associate the branch office subnet with Site1, or link Site4 to Site1 with a site link whose cost is lower than its links to the other sites.
Your network contains an Active Directory Domain Services (AD DS) domain named contoso.com.
The domain contains the users shown in the following table.
The domain has the Group Policy Objects (GPOs) shown in the following table.
The GPOs are configured as shown in the following table.
For each of the following statements, select Yes if the statement is true, Otherwise, select No.
NOTE: Each correct selection is worth one point.
| Name | Located in |
| --- | --- |
| User1 | Contoso.com |
| User2 | Contoso.com/Users |
| User3 | Contoso.com/OU1 |
| Name | Linked to |
| --- | --- |
| Default Domain Policy | Contoso.com |
| Default Domain Controllers Policy | Domain Controllers |
| GPO1 | OU1 |
| GPO | Minimum password length |
| --- | --- |
| Default Domain Policy | 8 |
| Default Domain Controllers Policy | 12 |
| GPO1 | 10 |
Explanation
Statement 1 (Yes): Password policy for domain user accounts comes only from a GPO linked at the domain level. The Default Domain Policy, linked to contoso.com, sets a minimum password length of 8, so User1 must use at least eight characters.
Statement 2 (No): The 12-character minimum is set in the Default Domain Controllers Policy, which is linked to the Domain Controllers OU. Account Policies in a GPO linked below the domain level affect only local accounts on the computers in that OU, not domain accounts. User2 is in the Users container and is still subject to the domain-level minimum of 8 characters.
Statement 3 (No): GPO1 is linked to OU1 and sets a minimum of 10 characters, but because it is linked to an OU it applies only to local accounts on computers in OU1. It does not change the password requirements of the domain account User3, which remain the Default Domain Policy minimum of 8 characters. A different minimum for specific domain users requires a fine-grained password policy (PSO) applied to users or global groups, not an OU-linked GPO.
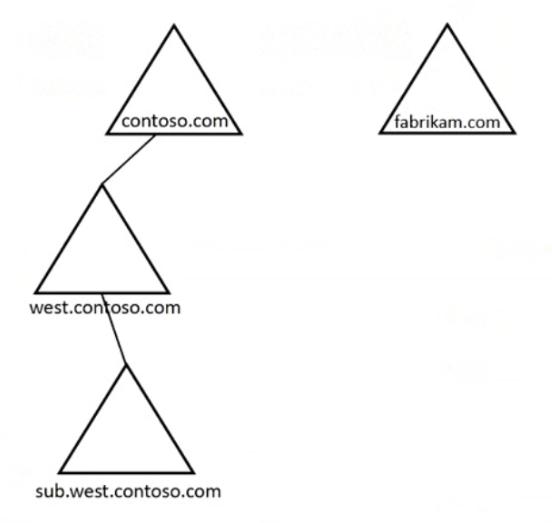
Your network contains the domains shown in the following exhibit.
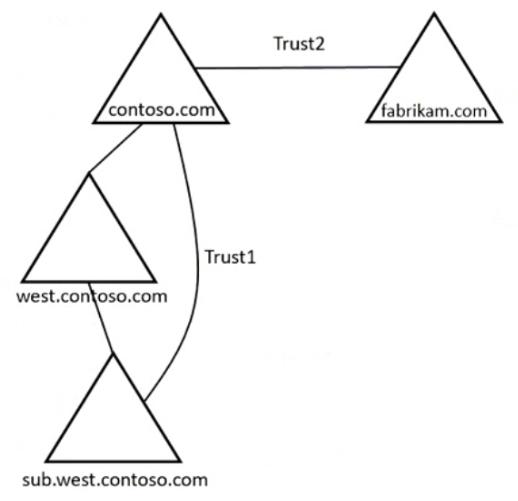
You need to establish trust relationships as shown in the following exhibit.
Which type of trust can you use for Trust1 and Trust2? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Explanation
Trust1: Shortcut trust only — Trust1 links two domains that already belong to the same Active Directory forest, and inside a single forest every domain is already connected by automatic two-way transitive parent-child and tree-root trusts, so the only trust an administrator can create there is a shortcut (cross-link) trust, which shortens the referral path between two domains in different branches of the same forest. Forest trust and external trust are not available options here because both are designed to join separate forests or separate domains outside the forest, and Active Directory will not let you create them between two domains that share a forest.
Trust2: Forest trust or external trust only — Trust2 crosses a forest boundary, connecting a domain in one forest to a domain in another forest, and that scenario supports either a forest trust (created between the two forest root domains, transitive across all domains in both forests, and requiring both forests to be at Windows Server 2003 or higher forest functional level) or an external trust (a non-transitive trust between two specific domains, which also works when the other side is an NT 4.0-style or otherwise non-forest-trust-capable domain). A shortcut trust cannot be used because shortcut trusts are only valid between domains within a single forest.
Your network contains an Active Directory Domain Services (AD DS) domain named contoso.com. The domain contains the users shown in the following table.
| Name | Located in |
| --- | --- |
| User1 | Contoso\Users |
| User2 | Contoso\OU1 |
| User3 | Contoso\OU1\OU2 |
The domain has the Group Policy Objects (GPOs) shown in the following table.
| Name | Linked to | Enforcement |
| --- | --- | --- |
| GPO1 | Contoso.com | Enforce is enabled for the GPO link. |
| GPO2 | OU1 | None |
| GPO3 | OU2 | Block inheritance is enabled for OU2. |
The GPOs are configured to map a drive named H as shown in the following table.
| Name | Configuration |
| --- | --- |
| GPO1 | Drive H maps to \\server1\share. |
| GPO2 | Drive H maps to \\server2\share. |
| GPO3 | Drive H maps to \\server3\share. |
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Explanation
Statement 1 (No): User1 is in the default Users container (Contoso\Users), which is a container, not an OU, so GPOs cannot be linked to it. Only the domain-linked GPO1 applies, so drive H maps to \\server1\share, not \\server2\share.
Statement 2 (Yes): User2 is in OU1 and receives GPO1 (domain) and GPO2 (OU1). Normally the GPO linked closest to the user wins, but the GPO1 link is Enforced. Enforced links are processed last and win over conflicting settings in GPOs linked to lower-level containers, so drive H maps to \\server1\share.
Statement 3 (No): User3 is in OU2, which has Block inheritance enabled. Block inheritance stops GPO2 (linked to OU1) from applying, but it cannot block an Enforced link, so GPO1 still applies along with GPO3. Because GPO1 is enforced, its setting wins over GPO3's conflicting setting, so drive H maps to \\server1\share, not \\server3\share.
Your network contains an Active Directory Domain Services (AD DS) domain. The domain contains a user named User1. User1 is a member of a group named Group1 and is in an organizational unit (OU) named OU1.
The domain has minimum password lengths configured as shown in the following table.
| Value | Location |
|---|---|
| 10 | Default Domain Policy |
| 12 | Default Domain Controllers Policy |
| 8 | Group Policy linked to OU1 |
| 14 | Password settings object applied to Group1 |
| 7 | Password settings object applied to User1 |
What is the minimum password length that User1 should use when changing to a new password?
- A. 7 Correct
- B. 8
- C. 10
- D. 12
- E. 14
Explanation
The minimum password length for User1 is determined by the Password Settings object applied directly to the user (User1), which has a value of 7. This setting takes precedence over all other settings, including those from group policies and organizational units.
Your network contains an Active Directory Domain Services (AD DS) forest named contoso.com. The forest contains the domain controllers shown in the following table.
| Name | Operations master role |
|---|---|
| DC1 | Schema master |
| DC2 | Infrastructure master |
| DC3 | Domain naming master |
| DC4 | PDC emulator, RID master |
You have a partner organization that has an AD DS forest named fabrikam.com.
You create a trust relationship between contoso.com and fabrikam.com.
You need to configure selective authentication for the trust relationship.
Which domain controller should be granted permissions to fabrikam.com?
- A. DC1
- B. DC2
- C. DC3
- D. DC4 Correct
Explanation
DC4 holds the PDC emulator role. After the NTLM pass-through authentication protections (CVE-2022-21857), a trust that uses selective authentication needs the PDC emulator of the forest root domain to be granted the Allowed to Authenticate permission on the domain controller computer accounts in the partner forest. It also needs read access to the partner forest's configuration partition, so that it can validate pass-through requests across the trust. The schema master, infrastructure master, and domain naming master roles (DC1, DC2, DC3) play no part in this check.
You have a Microsoft Entra Domain Services domain named contoso.com.
You need to provide an administrator with the ability to manage Group Policy Objects (GPOs). The solution must use the principle of least privilege.
To which group should you add the administrator?
- A. AAD DC Administrators Correct
- B. Domain Admins
- C. Schema Admins
- D. Enterprise Admins
- E. Group Policy Creator Owners
Explanation
In Microsoft Entra Domain Services, Microsoft manages the domain controllers, and customers do not get Domain Admins, Enterprise Admins, or Schema Admins rights in the managed domain. Members of the AAD DC Administrators group have Group Policy administration privileges in the managed domain. They can edit the built-in AADDC Users and AADDC Computers GPOs and create custom GPOs and OUs. Administering Group Policy requires signing in with an account in that group. Adding the administrator to AAD DC Administrators is therefore the least privileged supported way to let them manage GPOs. Group Policy Creator Owners is not the documented mechanism for GPO administration in a managed domain.
Your network contains an on-premises Active Directory Domain Services (AD DS) domain named contoso.com. Contoso.com contains an organizational unit (OU) named OU1.
You have an Azure subscription that is linked to a Microsoft Entra tenant named fabrikam.com.
You need to sync contoso.com with fabrikam.com. The solution must meet the following requirements:
• Support Windows Hello for Business by using a hybrid certificate deployment.
• Ensure that the passwords in contoso.com do NOT sync to fabrikam.com.
Which Microsoft Entra Connect feature should you use for each requirement? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Explanation
Support Windows Hello for Business by using a hybrid certificate deployment: Device writeback — A hybrid certificate trust deployment requires the on-premises AD DS forest to know about devices that are registered in Microsoft Entra ID, and Microsoft Entra Connect's device writeback feature copies those Entra ID device objects back into the on-premises directory (the Registered Devices container) so that domain controllers and the certificate/conditional-access evaluation can recognize the device. Pass-through authentication and password hash synchronization only affect how user sign-in credentials are validated and do nothing to make device objects visible on-premises.
Ensure that the passwords in contoso.com do NOT sync with fabrikam.com: Pass-through authentication — With pass-through authentication, Microsoft Entra Connect installs a lightweight agent on-premises that validates each sign-in directly against a contoso.com domain controller, so no password or password hash ever leaves the on-premises directory and none is stored in fabrikam.com. Password hash synchronization is the opposite of the requirement because it copies password hashes into Entra ID, and password writeback moves password changes in the other direction (from Entra ID back to AD DS) rather than preventing password sync.
Your network contains an Active Directory Domain Services (AD DS) domain. The domain contains two servers named Server1 and Server2 and the users shown in the following table.
| Name | Member of |
|---|---|
| User1 | Contoso\Administrators |
| User2 | Contoso\Remote Management Users |
| User3 | Server2\Administrators |
| User4 | Server2\Remote Management Users |
Which users can establish a PowerShell remoting session from Server1 to Server2?
- A. User1 and User3 only
- B. User2 and User4 only
- C. User3 and User4 only Correct
- D. User1, User3, and User4 only
- E. User1, User2, User3, and User4
Explanation
User3 is a member of Server2's Administrators group and User4 is a member of Server2's Remote Management Users group, both of which have the necessary permissions to establish a PowerShell remoting session from Server1 to Server2.
Your network contains an on-premises Active Directory Domain Services (AD DS) domain named contoso.com. Contoso.com contains an organizational unit (OU) named OU1.
You have an Azure subscription named Sub1 that is linked to a Microsoft Entra tenant named fabrikam.com. Fabrikam.com syncs with contoso.com.
In Sub1, you create a Microsoft Entra Domain Services domain configured as shown in the following table.
In domain1.onmicrosoft.com, you create two OUs named OU1 and OU2.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
| Property | Value |
| --- | --- |
| DNS domain name | domain1.onmicrosoft.com |
| Location | East US |
| IP addresses | East US/10.0.2.5 10.0.2.4 |
| Secure LDAP | Disabled |
| Secure LDAP external IP addresses | East US/52.188.201.46 |
| Synchronization | All |
| Admin group | AAD DC Administrators |
Explanation
Statement 1 (Yes): contoso.com syncs to the Microsoft Entra tenant fabrikam.com through Microsoft Entra Connect, and the managed domain synchronizes All users from the tenant. User1 therefore reaches fabrikam.com and then domain1.onmicrosoft.com. The managed domain has a flat OU structure: on-premises OUs such as OU1 are not reproduced, and all synchronized user accounts are placed in the built-in AADDC Users container. For User1 to sign in to the managed domain, Microsoft Entra Connect must also synchronize the legacy password hashes.
Statement 2 (No): synchronization is one-way, from Microsoft Entra ID into Microsoft Entra Domain Services. Objects created in a custom OU of the managed domain, such as OU2, exist only in the managed domain and are never synchronized back to fabrikam.com.
Statement 3 (Yes): User3 is created as a cloud account in the tenant, and with synchronization set to All, the account is synchronized into the managed domain's built-in users container (AADDC Users). Synchronized accounts never land in custom OUs such as OU1 or OU2. Cloud-only accounts sync once their password hashes exist, which happens when the user changes their password.
Your network contains an Active Directory Domain Services (AD DS) domain named contoso.com.
You have a Microsoft Entra tenant.
You need to implement Microsoft Entra Connect Sync. The solution must meet the following requirements:
• Prevent the password hashes of contoso.com from being synced to the Microsoft Entra tenant.
• Minimize user effort when authenticating to Microsoft Entra registered apps.
• Minimize the number of on-premises infrastructure components.
What should you include in the solution for each requirement? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Explanation
Prevent contoso.com password hashes from being synced to the tenant: Pass-through authentication — With pass-through authentication (PTA), Microsoft Entra Connect Sync synchronizes only directory objects and attributes; the password validation is handed off to a lightweight PTA agent that checks the credential directly against an on-premises domain controller, so no password hashes ever leave contoso.com. Password hash synchronization is exactly what the requirement forbids, and while AD FS federation would also keep hashes on-premises, it requires a whole federation server and web application proxy farm, which conflicts with minimizing on-premises infrastructure — PTA only needs an agent (which can even run on the Entra Connect server itself).
Minimize user effort when authenticating to Microsoft Entra registered apps: Single sign-on (SSO) — Microsoft Entra seamless single sign-on is the companion feature to pass-through authentication: domain-joined machines on the corporate network get a Kerberos ticket for the Entra service and are signed in to Entra-integrated apps automatically, without the user retyping a password. It is enabled as an option in Microsoft Entra Connect and adds only a computer account (AZUREADSSOACC) in AD DS, so unlike AD FS it delivers the seamless sign-in experience without deploying additional on-premises servers.
Your network contains an Active Directory Domain Services (AD DS) forest. The forest contains two domains named contoso.com and east.contoso.com. Contoso.com contains two users named CONTOSO\User1 and EAST\User2.
You need to ensure that the users can perform the following tasks:
• User1 must deploy an additional domain controller to east.contoso.com.
• User2 must deploy a new domain controller that will host a domain named west.contoso.com.
The solution must follow the principle of least privilege.
To which group should you add each user? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Explanation
User1: EAST\Domain Admins — Adding a domain controller to an existing domain requires membership in the Domain Admins group of that domain. The domain is east.contoso.com, so EAST\Domain Admins is the least-privileged choice. CONTOSO\Domain Admins has no administrative rights in the child domain, CONTOSO\Enterprise Admins would work but grants forest-wide rights, and Schema Admins only controls changes to the schema.
User2: CONTOSO\Enterprise Admins — A domain controller that hosts west.contoso.com is the first domain controller of a new child domain in the forest. Installing a new child domain or a new domain tree requires membership in the Enterprise Admins group, because it adds a domain to the forest's partitions and trusts. Domain Admins of contoso.com or of east.contoso.com does not have the rights to add a new domain to the forest, and Schema Admins only controls changes to the schema.
Your network contains an Active Directory Domain Services (AD DS) forest. The forest contains the groups shown in the following table.
You need to implement a group nesting strategy.
Which groups can be added as members of Group12, and which groups can be added as members of Group21? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
| Name | Type | In domain |
| --- | --- | --- |
| Group11 | Domain local | contoso.com |
| Group12 | Global | contoso.com |
| Group13 | Global | contoso.com |
| Group14 | Universal | contoso.com |
| Group21 | Universal | east.contoso.com |
Explanation
Group12: Group13 only — Group12 is a global group, and in AD DS a global group can only contain user accounts, computer accounts, and other global groups from its own domain. Group13 is the only other same-domain global group available, so it is the only valid nested member; Group14 (universal scope) and Group11 (domain local scope) cannot be nested inside a global group, and Group21 is in a different domain, which global scope never permits.
Group21: Group12, Group13, and Group14 only — Group21's scope accepts members from any domain in the forest, so the global groups Group12 and Group13 and the universal group Group14 can all be nested into it. The option that also includes Group11 is wrong because Group11 is a domain local group, and a domain local group can only be nested into another domain local group in its own domain — it can never become a member of a group in a different domain.
Your network contains a Microsoft Entra Domain Services domain named sk230128outlook.onmicrosoft.com. The domain contains a server named Server1 that runs Windows Server.
You have the users shown in the following table.
The domain contains the Group Policy Objects (GPOs) shown in the following exhibit.
The minimum password length for each GPO is configured as shown in the following table.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
| Name | Description |
| --- | --- |
| User1 | Domain user in the AADDC Users organizational unit (OU) |
| User2 | Local user on Server1 |
| User3 | Domain user in an organizational unit (OU) named OU1 |
| GPO | Value |
| --- | --- |
| Default Domain Policy | 9 |
| AADDC Computers GPO | 7 |
| AADDC Users GPO | 10 |
| Default Domain Controllers Policy | 12 |
| GPO1 | 13 |
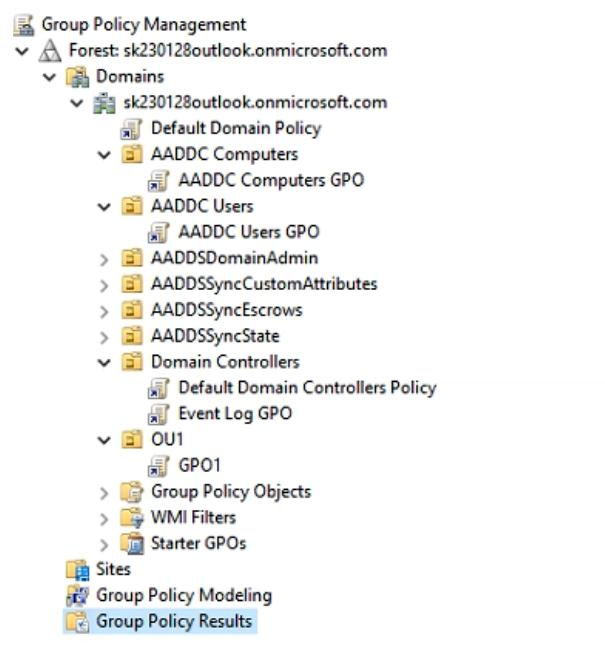
Explanation
Statement 1 (No): Password settings are in the Computer Configuration part of a GPO. For domain accounts, domain controllers apply only the account policy linked at the domain level, or a fine-grained password policy that applies to the user. In a Microsoft Entra Domain Services managed domain, the passwords of users synced from Microsoft Entra ID are set in Microsoft Entra ID. The AADDC Users GPO is linked to an OU, and it holds users rather than computers, so its 10-character setting does not apply to User1's domain password.
Statement 2 (Yes): User2 is a local account on Server1. Local accounts follow the account policy that applies to the computer, including GPOs linked to the computer's OU. Server1 is domain-joined, so it is in AADDC Computers by default, and AADDC Computers GPO requires at least seven characters (every other GPO that could reach Server1 requires more). User2's new password must therefore have at least seven characters.
Statement 3 (No): GPO1 is linked to OU1. An account policy linked to an OU affects only local accounts on computers in that OU, not domain user accounts placed in the OU. GPO1's 13-character minimum therefore does not apply to User3's domain password.
Your network contains an Active Directory Domain Services (AD DS) forest named contoso.com that has the domains shown in the following table.
You are creating a disaster recovery plan for the forest.
What is the minimum number of domain naming FSMO role holders and RID master FSMO role holders that should be online to maintain full functionality of the forest? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
| Name | Number of domain controllers |
| --- | --- |
| contoso.com | 3 |
| west.contoso.com | 2 |
| east.contoso.com | 2 |
| sub.west.contoso.com | 2 |
| adatum.com | 2 |
Explanation
Domain naming: 1 — The domain naming master is a forest-wide FSMO role, so exactly one holder exists in the entire contoso.com forest regardless of how many domains it contains; it is the role that authorizes adding, removing, and renaming domains and application partitions, so a single online holder is all that is required (and all that is possible) for full forest functionality. Higher values such as 2 or 5 would imply one holder per domain, which is how the domain-level roles behave, not the forest-level ones.
RID master: 5 — The RID master is a domain-wide FSMO role, so every domain in the forest has its own holder, and with five domains in contoso.com all five must be online for full functionality. Each RID master issues RID pools to the DCs in its own domain so they can mint unique SIDs for new users, groups, and computers; a domain whose RID master is offline eventually cannot create new security principals, so no single holder can cover the whole forest the way the domain naming master does.
Your network contains an Active Directory Domain Services (AD DS) forest named contoso.com.
You have a partner company named ADatum Corporation that has an AD DS forest named adatum.com.
You configure the trust relationship shown in the following exhibit.
The forests contain the groups shown in the following table.
The ADatum domains contain the member servers shown in the following table.
For each of the following statements, select Yes if the statement is true Otherwise, select No.
NOTE: Each correct selection is worth one point.
| Name | Type | In domain |
| --- | --- | --- |
| Group1 | Domain local | contoso.com |
| Group2 | Domain local | adatum.com |
| Group3 | Global | west.adatum.com |
| Group4 | Universal | contoso.com |
| Name | In domain |
| --- | --- |
| Server1 | adatum.com |
| Server2 | west.adatum.com |
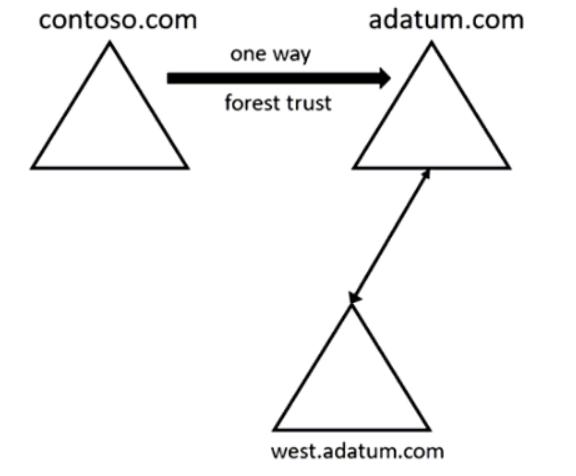
Explanation
The exhibit shows a one-way forest trust with the arrow pointing from contoso.com to adatum.com: contoso.com is the trusting forest and adatum.com is the trusted forest, so principals from the adatum.com forest (including west.adatum.com, a child domain in that forest) can be granted access to contoso.com resources, but not the other way round. Statement 1 (No): Group2 is a domain local group, and a domain local group can be assigned permissions only within its own domain (adatum.com). Server2 is in west.adatum.com. Statement 2 (Yes): A domain local group can contain global groups from any trusted domain. Group3 is a global group in west.adatum.com, which is trusted by contoso.com through the transitive forest trust, so Group3 can be added to Group1 in contoso.com. Statement 3 (No): A universal group can be assigned permissions in its own forest or in trusting forests. Group4 is in contoso.com, and adatum.com does not trust contoso.com (the trust is one-way), so Group4 cannot be assigned permissions on Server1 in adatum.com.
Note: This section contains one or more sets of questions with the same scenario and problem. Each question presents a unique solution to the problem. You must determine whether the solution meets the stated goals. More than one solution in the set might solve the problem. It is also possible that none of the solutions in the set solve the problem.
After you answer a question in this section, you will NOT be able to return. As a result, these questions do not appear on the Review Screen.
Your network contains an Active Directory Domain Services (AD DS) domain named contoso.com.
You implement a central store.
You create a new Group Policy Object (GPO) named GPO1.
When you attempt to edit GPO1, you see the settings shown in the exhibit. (Click the Exhibit tab.)
You need to ensure that all settings are available.
Solution: You delete the \\contoso.com\SYSVOL\contoso.com\Policies\PolicyDefinitions folder.
Does this meet the goal?
Explanation
The exhibit shows that Administrative Templates are retrieved from the central store, and only the ActiveX Installer Service settings (2 settings) are listed. This means the central store contains only that one ADMX file. When a central store exists, the Group Policy Management Editor reads ADMX files only from it and ignores the local store. The \\contoso.com\SYSVOL\contoso.com\Policies\PolicyDefinitions folder is the central store. If you delete it, the editor falls back to the local ADMX files in C:\Windows\PolicyDefinitions on the management computer, and the full set of Administrative Templates settings becomes available. The solution meets the goal.
Note: This section contains one or more sets of questions with the same scenario and problem. Each question presents a unique solution to the problem. You must determine whether the solution meets the stated goals. More than one solution in the set might solve the problem. It is also possible that none of the solutions in the set solve the problem.
After you answer a question in this section, you will NOT be able to return. As a result, these questions do not appear on the Review Screen.
Your network contains an Active Directory Domain Services (AD DS) domain named contoso.com.
You implement a central store.
You create a new Group Policy Object (GPO) named GPO1.
When you attempt to edit GPO1, you see the settings shown in the exhibit. (Click the Exhibit tab.)
You need to ensure that all settings are available.
Solution: You modify the properties of GPO1.
Does this meet the goal?
Explanation
The exhibit shows that Administrative Templates are retrieved from the central store, and only the ActiveX Installer Service settings (2 settings) are listed. The central store contains only that one ADMX file. The settings the editor can show depend on which ADMX and ADML files are in the central store, not on the GPO itself. GPO properties, such as disabling the Computer or User Configuration settings, control how the GPO is processed. They do not change which administrative templates are loaded. To make all settings available, you must fill the central store with the full set of ADMX/ADML files, for example by copying C:\Windows\PolicyDefinitions into it, or remove the incomplete central store. The solution does not meet the goal.
Note: This section contains one or more sets of questions with the same scenario and problem. Each question presents a unique solution to the problem. You must determine whether the solution meets the stated goals. More than one solution in the set might solve the problem. It is also possible that none of the solutions in the set solve the problem.
After you answer a question in this section, you will NOT be able to return. As a result, these questions do not appear on the Review Screen.
Your network contains an Active Directory Domain Services (AD DS) domain named contoso.com.
You implement a central store.
You create a new Group Policy Object (GPO) named GPO1.
When you attempt to edit GPO1, you see the settings shown in the exhibit. (Click the Exhibit tab.)
You need to ensure that all settings are available.
Solution: You copy the contents of the C:\Windows\PolicyDefinitions folder to the central store.
Does this meet the goal?
Explanation
The exhibit shows that Administrative Templates are retrieved from the central store, and only the ActiveX Installer Service settings (2 settings) are listed. The central store contains only that one ADMX file. When a central store exists, the Group Policy Management Editor reads ADMX files only from it. Copying the full contents of C:\Windows\PolicyDefinitions into the central store (\\contoso.com\SYSVOL\contoso.com\Policies\PolicyDefinitions) adds all the ADMX files and their language-specific ADML subfolders. This is the documented way to populate a central store, and afterwards all Administrative Templates settings are available when you edit GPO1. The solution meets the goal.
Your network contains an Active Directory Domains Services (AD DS) forest named adatum.com. Adatum.com contains the users shown in the following table.
| Name | In domain | Member of |
|---|---|---|
| User1 | adatum.com | ADATUM\Enterprise Admins, Domain Users |
| User2 | east.adatum.com | EAST\Domain Admins, Domain Users |
| User3 | east.adatum.com | Domain Users |
You deploy a workgroup server named RODC1 that runs Windows Server. RODC1 contains a user named User4 that is a member of the local Administrators group.
You pre-create a read-only domain controller (RODC) account named RODC1 in east.adatum.com and delegate RODC installation and administration permissions to User3.
You sign-in to RODC1 as User4.
Which credentials can be used to promote RODC1 to a RODC in east.adatum.com?
- A. User3 only
- B. User3 and User1 only
- C. User3 and User2 only
- D. User1, User2, and User3 Correct
Explanation
User3 can promote RODC1 due to delegated permissions. User2 can do so as a member of EAST\Domain Admins, and User1 can because they are an Enterprise Admin with forest-wide rights.
Your on-premises network contains an Active Directory Domain Services (AD DS) domain named fabrikam.com. The domain contains a domain controller named DC1. DC1 has the DNS Server role installed and hosts the DNS primary zone for fabrikam.com.
You have an Azure subscription that contains a virtual network named VNet1. VNet1 contains a virtual machine named VM1.
The on-premises network is connected to Azure by using a Site-to-Site (S2S) VPN.
From the Azure Command-Line interface (CLI), you run the following commands.
New-AzPrivateDnsZone -Name azure.fabrikam.com -ResourceGroupName RG1
New-AzPrivateDnsVirtualNetworkLink -ZoneName "azure.fabrikam.com" -ResourceGroupName "RG1" -Name "DNSlink" -VirtualNetworkId $VNET1.id
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Explanation
Statement 1 (No): azure.fabrikam.com is an Azure private DNS zone. Private zones are resolvable only from linked virtual networks and have no publicly reachable name servers that a delegation could point to, so adding a delegation to the on-premises fabrikam.com zone does not let on-premises hosts resolve its records.
Statement 2 (Yes): A conditional forwarder for azure.fabrikam.com on DC1 sends those queries over the Site-to-Site VPN to a DNS server or Azure DNS Private Resolver inbound endpoint in VNet1, which answers from the linked private zone. This lets on-premises hosts resolve the records.
Statement 3 (No): The virtual network link was created without the -EnableRegistration switch, so it is a resolution-only link. VM records are registered automatically only when registration is enabled on the virtual network link.
Your network contains an Active Directory Domain Services (AD DS) domain. The domain contains two domain controllers named DC1 and DC2. DC2 runs on a Hyper-V virtual machine.
You plan to deploy a new domain controller by cloning DC2.
You need to create the CustomDCCloneAllowList.xml and the DCCloneConfig.xml files for DC2.
In which folder should you save the files?
- A. C:\Windows
- B. C:\Windows\Setup
- C. C:\
- D. C:\Windows\NTDS Correct
Explanation
When a cloned virtual domain controller starts, the cloning process looks for DCCloneConfig.xml in a fixed order: the DSA Working Directory, then %windir%\NTDS, then the root of removable read/write media. It searches for CustomDCCloneAllowList.xml in the folder named by the AllowListFolder registry value, then the DSA Working Directory, then %windir%\NTDS, then the root of removable media. These paths can't be changed. By default the DSA Working Directory is %windir%\NTDS, which is also where New-ADDCCloneConfigFile writes the file when no -Path is given. Both files should therefore be saved in C:\Windows\NTDS on DC2. C:\, C:\Windows and C:\Windows\Setup are not locations the cloning process checks.
Your network contains an Active Directory Domain Services (AD DS) forest named contoso.com. The forest contains the users shown in following table.
| Name | Member of |
|---|---|
| User1 | Enterprise Admins group |
| User2 | Domain Users group |
You have a workgroup server named Server1 that runs Windows Server and contains the local users shown in the following table.
| Name | Member of |
|---|---|
| User3 | Administrators group |
| User4 | Users group |
You promote Server1 to the first domain controller in a new child domain named east.contoso.com.
Which users can sign in to Server1 locally?
- A. User1 only
- B. User3 only
- C. User1 and User2 only
- D. User1 and User3 only Correct
- E. User3 and User4 only
- F. User1, User2, User3 and User4
Explanation
When a workgroup server is promoted to the first domain controller in a new domain, its local accounts are converted to domain accounts in that domain and added to the matching built-in domain groups. User3 becomes a member of the built-in Administrators group of east.contoso.com, and User4 becomes a member of the built-in Users group. On a domain controller, the Allow log on locally right is granted by default only to administrative and operator groups such as Administrators, Account Operators, Backup Operators, Print Operators and Server Operators, not to Users or Domain Users. The Enterprise Admins group is automatically added to the Administrators group in every domain in the forest, so User1 can sign in locally. User2 (Domain Users) and User4 (Users) cannot. Therefore only User1 and User3 can sign in to Server1 locally.
Your network contains two Active Directory Domain Services (AD DS) forests named contoso.com and adatum.com. A two-way external trust exists between contoso.com and adatum.com. The forests contain the servers shown in the following table.
You need to ensure that users from contoso.com can access only shared resources hosted on SRV1. The solution must meet the following requirements:
• Ensure that users from adatum.com can access the resources hosted in contoso.com.
• Prevent the contoso.com users from accessing any other resources in adatum.com.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
| Name | In domain | Description |
| --- | --- | --- |
| DC1 | contoso.com | Hosts all FSMO roles |
| DC2 | adatum.com | Hosts all FSMO roles |
| SRV1 | adatum.com | File server |
| SRV2 | adatum.com | File server |
Explanation
Modify the trust on: DC2. Selective authentication restricts users from the trusted domain (contoso.com) when they access computers in the trusting domain (adatum.com), so it is set on adatum.com's outgoing trust to contoso.com. Active Directory Domains and Trusts shows authentication settings only for the outgoing side of a trust, so you make the change on a domain controller in adatum.com, which is DC2. Changing the trust on DC1 would restrict adatum.com users instead, and they must keep their access to contoso.com, so neither DC1 nor DC1 and DC2 is right.
Modify the permissions for the: Computer object of SRV1. Once selective authentication is on, contoso.com users can authenticate only to computers on which they have been granted the Allowed to Authenticate permission. You grant that permission on SRV1's computer object in adatum.com, so they can reach SRV1 and no other server. Share and NTFS permissions on the file shares still apply afterwards, but on their own they do not let the users authenticate to SRV1. The DC1 computer object belongs to contoso.com and does not control access to adatum.com resources.
Your company has an office in New York.
The network contains an Active Directory Domain Services (AD DS) forest.
You plan to open a new office in Seattle. The Seattle office will connect to the New York office by using a high-speed WAN link.
You need to recommend a solution for the Seattle office that meets the following requirements.
• Ensures that users in the Seattle office authenticate against a local domain controller, whenever possible
• Ensures that the Seattle office users can change their password in the event of a WAN outage
• Minimizes administrative effort
What should you include in the recommendation?
- A. a subnet, an SMTP site link, and a read-only domain controller (RODC)
- B. a custom AD DS partition, a subnet, and a site link bridge
- C. a subnet, a site, and a domain controller Correct
- D. a subnet, an IP site link, and an Active Directory Lightweight Directory Services (AD LDS) server
Explanation
Option C ensures that users in the Seattle office can authenticate against a local domain controller by creating a subnet and site for the new location, with a domain controller deployed there. This setup minimizes administrative effort while ensuring local authentication and password changes during WAN outages.
Your network contains two Active Directory Domain Services (AD DS) forests as shown in the following table.
| Name | Domain |
|---|---|
| Contoso.com | South.contoso.com |
| Contoso.com | North.contoso.com |
| Fabrikam.com | West.fabrikam.com |
| Fabrikam.com | East.fabrikam.com |
West.fabrikam.com contains a file server named Fileserver01. South.contoso.com contains a global group named Group1.
You need to ensure that the members of Group1 can access a share on Fileserver01. The solution must ensure that the users in the fabrikam.com forest cannot access the resources in south.contoso.com.
Which type of trust should you implement?
- A. realm
- B. external Correct
- C. shortcut
- D. forest
Explanation
Create a one-way external trust in which West.fabrikam.com (the resource domain) trusts South.contoso.com (the account domain). An external trust is a non-transitive trust between two domains in different forests, so it links only these two domains instead of the whole forests. Because it is one-way, members of Group1 in South.contoso.com can be granted access to the share on Fileserver01, while users in the fabrikam.com forest gain no access to resources in south.contoso.com. A forest trust would join every domain of both forests, a shortcut trust works only between domains in the same forest, and a realm trust is for non-Windows Kerberos realms.
You have 10 on-premises servers that run Windows Server.
You plan to use Azure Network Adapter to connect the servers to the resources in Azure.
Which prerequisites do you require on-premises and in Azure? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Explanation
To configure the on-premises servers, use: Windows Admin Center. Azure Network Adapter is set up only through Windows Admin Center (Networks tool > Add Azure Network Adapter). It sets up the point-to-site VPN client configuration on the server automatically. Server Manager and Azure CLI have no Azure Network Adapter feature. Routing and Remote Access is not the console used to set it up.
To connect the Azure resources and Azure Network Adapter, use: An Azure virtual network gateway. Azure Network Adapter creates a point-to-site VPN from each server into an Azure virtual network. Point-to-site connections end on a VPN-type virtual network gateway in that VNet, which needs a gateway subnet and a point-to-site address pool. Azure Bastion only brokers RDP/SSH into VMs. Azure Firewall filters traffic but does not end VPN tunnels. A private endpoint exposes a single PaaS service over a private IP. A public load balancer spreads inbound traffic. None of these can end the server's point-to-site tunnel.
You have a server named Server1 that has Windows Admin Center installed. The certificate used by Windows Admin Center was obtained from a certification authority (CA).
The certificate expires.
You need to replace the certificate.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Explanation
First obtain and install the new CA-issued certificate in the local computer's certificate store (LocalMachine\My), because the installer can only use a certificate that is already installed. Next copy the certificate's thumbprint, which identifies the certificate to Windows Admin Center. Finally run Windows Admin Center Setup, select Change, choose to use a pre-installed TLS certificate, and enter the thumbprint so the gateway starts using the new certificate. Remove and Repair do not switch the certificate, and Windows Admin Center does not use IIS bindings.
You have an on-premises server named Server1 that runs Windows Server and has internet connectivity.
You have an Azure subscription.
You need to monitor Server1 by using Azure Monitor.
Which resources should you create in the subscription, and what should you install on Server1? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Hot Area:
Explanation
In the subscription, create: A Log Analytics workspace — Azure Monitor stores and queries machine telemetry (performance counters, events, syslog) in a Log Analytics workspace, so a workspace is the prerequisite resource that must exist before Server1 can be onboarded and its data ingested for alerts, workbooks, and KQL queries. An Azure Files storage account is only file-share storage and has no role in Azure Monitor ingestion, and the Azure SQL database or Azure Blob Storage account choices are wrong because Azure Monitor does not send agent log data into a SQL database or a blob container as its collection target.
On Server1, install: The Azure Monitor agent — for an on-premises Windows Server, the machine is onboarded through Azure Arc and the Azure Monitor agent (AMA) is deployed as the extension that collects the data defined by a data collection rule and forwards it to the Log Analytics workspace over the server's internet connection. The Analytics gateway (Log Analytics gateway) is only a proxy for machines with no direct internet access, which Server1 already has, and the Device Health Attestation server role is an unrelated health-attestation service that collects nothing for Azure Monitor.
You have an on premises Active Directory Domain Services (AD DS) domain that syncs with an Azure Active Directory (Azure AD) tenant. The domain contains two servers named Server1 and Server2.
A user named Admin1 is a member of the local Administrators group on Server1 and Server2.
You plan to manage Server1 and Server2 by using Azure Arc. Azure Arc objects will be added to a resource group named RG1.
You need to ensure that Admin1 can configure Server1 and Server2 to be managed by using Azure Arc.
What should you do first?
- A. From the Azure portal, generate a new onboarding script.
- B. Assign Admin1 the Azure Connected Machine Onboarding role for RG1. Correct
- C. Hybrid Azure AD join Server1 and Server2.
- D. Create an Azure cloud-only account for Admin1.
Explanation
Assigning Admin1 the Azure Connected Machine Onboarding role for RG1 ensures that they have the necessary permissions to configure Server1 and Server2 for management via Azure Arc. This role grants the required access without needing additional steps like generating scripts or joining machines to a different domain.
Your network contains two Active Directory Domain Services (AD DS) forests named contoso.com and fabrikam.com. A two-way forest trust exists between the forests. Each forest contains a single domain.
The domains contain the servers shown in the following table.
You need to configure resource based constrained delegation so that the users in contoso.com can use Windows Admin Center on Server1 to connect to Server2.
How should you complete the command? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Hot Area:
| Name | Domain | Description |
| --- | --- | --- |
| Server1 | contoso.com | Hosts a Windows Admin Center gateway |
| Server2 | fabrikam.com | Hosts resources that will be managed remotely by using Windows Admin Center on Server1 |
Explanation
Resource-based constrained delegation is configured on the resource that accepts the delegated credentials, not on the front-end service. The target node, Server2 in fabrikam.com, is therefore the object you modify with -Identity (Get-ADComputer server2.fabrikam.com). The -PrincipalsAllowedToDelegateToAccount parameter lists the accounts that are allowed to delegate to that node, which is the Windows Admin Center gateway computer, (Get-ADComputer server1.contoso.com). Delegation is granted to the gateway's computer account, not to a user group: the users' own access to Server2 still depends on their permissions there. The command is Set-ADComputer -Identity (Get-ADComputer server2.fabrikam.com) -PrincipalsAllowedToDelegateToAccount (Get-ADComputer server1.contoso.com). Resource-based constrained delegation works across domains and forests with a trust, which the two-way forest trust provides.
You have a server named Server1 that runs Windows Server and has the Hyper-V server role installed.
You need to limit which Hyper-V module cmdlets helpdesk users can use when administering Server1 remotely.
You configure Just Enough Administration (JEA) and successfully build the role capabilities and session configuration files.
How should you complete the PowerShell command? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Hot Area:
Explanation
[dropdown] -Path .\HyperVJeaConfig: Register-PSSessionConfiguration — The role capability (.psrc) and session configuration (.pssc) files have already been built, so the remaining step is to register the session configuration on Server1 so helpdesk users connecting remotely land in the constrained JEA endpoint; Register-PSSessionConfiguration takes the -Path to the .pssc file and the -Name of the endpoint to create. New-PSSessionConfigurationFile is wrong because that cmdlet only creates the .pssc file, which the scenario states is already done, and Enter-PSSession merely opens an interactive remote session against an endpoint that must already exist.
[dropdown] -Name 'HyperVJeaHelpDesk' -Force: .pssc — Register-PSSessionConfiguration must be pointed at a PowerShell session configuration file, and .pssc is the extension produced by New-PSSessionConfigurationFile; it defines the session type (RestrictedRemoteServer), the run-as virtual or group-managed service account, and the role definitions that map the helpdesk group to the role capability limiting them to specific Hyper-V module cmdlets. The .psrc extension belongs to the role capability file that the .pssc references rather than to the file you register, while .ps1 (script) and .psm1 (module) are not valid inputs for -Path here.
You have an Azure virtual machine named VM1 that runs Windows Server.
You have an Azure subscription that has Microsoft Defender for Cloud enabled.
You need to ensure that you can use the Azure Policy guest configuration feature to manage VM1.
What should you do?
- A. Add the PowerShell Desired State Configuration (DSC) extension to VM1.
- B. Configure VM1 to use a user-assigned managed identity.
- C. Configure VM1 to use a system-assigned managed identity. Correct
- D. Add the Custom Script Extension to VM1.
Explanation
To use the Azure Policy guest configuration feature to manage VM1, VM1 must have a system-assigned managed identity for authentication purposes. This allows the virtual machine to communicate securely with the Guest Configuration service.
You have an Azure subscription named sub1 and 500 on-premises virtual machines that run Windows Server.
You plan to onboard the on-premises virtual machines to Azure Arc by running the Azure Arc deployment script.
You need to create an identity that will be used by the script to authenticate access to sub1. The solution must use the principle of least privilege.
How should you complete the command? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Hot Area:
Explanation
Command for creating identity: New-AzADServicePrincipal — The Azure Arc "at-scale" onboarding script authenticates non-interactively to sub1 with a Microsoft Entra service principal, and New-AzADServicePrincipal creates the app registration plus its service principal object and secret in one step. New-AzADAppCredential only adds credentials to an app registration that already exists, and New-AzUserAssignedIdentity creates a managed identity, which is an Azure resource that can only be assigned to Azure resources and therefore cannot be used by a script running on an on-premises virtual machine.
Role for the identity: 'Azure Connected Machine Onboarding' — This built-in role grants exactly the permissions needed to read and create Azure Arc-enabled server resources (Microsoft.HybridCompute/machines write and read), which satisfies the least-privilege requirement for a one-time onboarding of the 500 servers. 'Virtual Machine Contributor' is far broader and targets Azure VM resources rather than Arc-enabled servers, and 'Virtual Machine User Login' only grants sign-in rights to an already-registered machine, not the ability to register one.
You have an Azure virtual machine named VM1 that has a private IP address only.
You configure the Windows Admin Center extension on VM1.
You have an on-premises computer that runs Windows 11. You use the computer for server management.
You need to ensure that you can use Windows Admin Center from the Azure portal to manage VM1.
What should you configure?
- A. an Azure Bastion host on the virtual network that contains VM1.
- B. a VPN connection to the virtual network that contains VM1. Correct
- C. a private endpoint on the virtual network that contains VM1.
- D. a network security group (NSG) rule that allows inbound traffic on port 443.
Explanation
Windows Admin Center in the Azure portal connects from your browser to the VM's IP address on the port where Windows Admin Center is installed. VM1 has only a private IP address, so the on-premises Windows 11 management computer needs network access to the virtual network that contains VM1. A VPN connection, such as a point-to-site or site-to-site VPN through a VPN gateway, provides that access. Connecting through a private IP address needs no inbound NSG rule; an inbound rule (port 6516 by default, not 443) is needed only for a public IP address, which VM1 does not have. Azure Bastion is not supported with Windows Admin Center in the Azure portal, and a private endpoint is for Azure PaaS services, not for reaching a VM.
Your company has a main office and a branch office. The two offices are connected by using a WAN link. Each office contains a firewall that filters WAN traffic.
The network in the branch office contains 10 servers that run Windows Server. All servers are administered from the main office only.
You plan to manage the servers in the branch office by using a Windows Admin Center gateway.
On a server in the branch office, you install the Windows Admin Center gateway by using the defaults settings.
You need to configure the firewall in the branch office to allow the required inbound connection to the Windows Admin Center gateway.
Which inbound TCP port should you allow?
- A. 443 Correct
- B. 3389
- C. 5985
- D. 6516
Explanation
The Windows Admin Center gateway uses port 443 by default for HTTPS connections to ensure secure communication between the client and the server. This is in line with standard practices for web-based management interfaces.
You have an Azure subscription that contains the following resources.
✑ An Azure Log Analytics workspace
✑ An Azure Automation account
✑ Azure Arc
You have an on-premises server named Server1 that is onboarded to Azure Arc.
You need to manage Microsoft updates on Server1 by using Azure Arc.
Which two actions should you perform? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
- A. From the Automation account, enable Update Management for Server1. Correct
- B. From the Virtual machines data source of the Log Analytics workspace, connect Server1.
- C. On Server1, install the Azure Monitor agent Correct
- D. Add Microsoft Sentinel to the Log Analytics workspace
Explanation
Update Management in Azure Automation (now retired and replaced by Azure Update Manager) supports Azure Arc-enabled servers. You enable Update Management for Server1 from the Automation account (option A), and Server1 must run the monitoring agent that reports update assessment data to the Log Analytics workspace linked to the Automation account (option C); on an Arc-enabled server this agent is deployed as a VM extension. Server1 is already managed by Azure Arc through its Connected Machine agent, so the monitoring agent is needed for update data, not for Arc itself. The Virtual machines data source of a Log Analytics workspace connects only Azure VMs, not on-premises Arc-enabled servers (option B), and Microsoft Sentinel is a security analytics service that plays no part in managing updates (option D).
You have an on-premises Active Directory Domain Services (AD DS) domain that syncs with an Azure Active Directory (Azure AD) tenant.
You have an on-premises web app named WebApp1 that only supports Kerberos authentication.
You need to ensure that users can access WebApp1 by using their Azure AD account. The solution must minimize administrative effort.
What should you configure? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Hot Area:
Explanation
In Azure AD: The Azure AD Application Proxy service — the cloud-side Application Proxy service is what you enable and configure in the Azure AD tenant; it publishes WebApp1 at an external Azure AD URL, pre-authenticates the user with their Azure AD account, and then forwards the request down to your network. Web Application Proxy is a Windows Server (Remote Access) role service that runs on-premises, not something you configure in Azure AD, and the connector is likewise an on-premises component.
On-premises: The Azure AD Application Proxy connector — the lightweight connector agent is installed on a domain-joined Windows Server inside your network, where it makes outbound-only connections to the Application Proxy service and performs Kerberos constrained delegation (KCD) on the user's behalf so WebApp1, which only supports Kerberos, receives a valid Kerberos ticket. Deploying Web Application Proxy instead would require an AD FS infrastructure plus inbound firewall openings and a DMZ server, which is far more administrative effort than the connector.
Your on-premises network contains an Active Directory domain named contoso.com and 500 servers that run Windows Server. All the servers are Azure Arc-enabled and joined to contoso.com.
You need to implement PowerShell Desired State Configuration (DSC) on all the servers. The solution must minimize administrative effort.
Where should you store the DSC scripts, and what should you use to apply DSC to the servers? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Explanation
Store in: An Azure Automation account. The Automation account hosts Azure Automation State Configuration, where you import, compile, and keep DSC configurations and modules centrally. An Azure App Configuration store holds application settings and feature flags, not DSC configurations, and an Azure Policy definition is a rule that describes what to evaluate or enforce, not a place to keep scripts.
Use: Guest configuration in Azure Policy. Guest configuration (Azure Machine Configuration) audits and applies DSC-based settings inside the operating system, and it works on Azure Arc-enabled servers through the Connected Machine agent just as on Azure VMs, so a single policy assignment at the subscription or resource group scope covers all 500 servers with minimal administrative effort. A GPO in AD DS cannot deliver or enforce PowerShell DSC configurations without custom startup scripts, and deploying VM extensions machine by machine does not give the central, policy-driven assignment and compliance reporting that guest configuration provides.
Your network contains an Active Directory Domain Services (AD DS) domain. The domain contains a server named Server1.
You implement Just Enough Administration (JEA) on Server1.
You need to perform remote administration tasks on Server1 by using only JEA.
What should you use?
- A. PowerShell only Correct
- B. Remote Server Administration Tools (RSAT) only
- C. PowerShell or Remote Desktop only
- D. PowerShell or Remote Server Administration Tools (RSAT) only
- E. Remote Server Administration Tools (RSAT) or Remote Desktop only
- F. PowerShell, Remote Server Administration Tools (RSAT), or Remote Desktop
Explanation
Just Enough Administration (JEA) is a security technology that leverages PowerShell to enable delegated administration. Since JEA specifically uses PowerShell sessions for remote administration, only option A, 'PowerShell only', aligns with the requirement of performing tasks using only JEA.
You have an Azure subscription. The subscription contains a virtual machine named VM1 that runs Windows Server.
You plan to manage VM1 by using a PowerShell runbook.
You need to create the runbook.
What should you create first?
- A. an Azure Automation account Correct
- B. an Azure workbook
- C. a Log Analytics workspace
- D. a Microsoft Power Automate flow
Explanation
An Azure Automation account is required to create and manage PowerShell runbooks. Without an Automation account, you cannot author or execute runbooks in Azure.
You have a server named Server1 that runs Windows Server and has the DHCP Server role installed. Server1 contains the following single scope:
• Scope: 192.168.16.0
• Address pool: 192.168.16.1-192.168.16.254
• Subnet mask: 255.255.255.0
• Lease duration: 8 days
You have four testing devices that are configured with static IP addresses as shown in the following table.
| Name | IP address |
|---|---|
| TestDevice1 | 192.168.16.242 |
| TestDevice2 | 192.168.16.243 |
| TestDevice3 | 192.168.16.244 |
| TestDevice4 | 192.168.16.245 |
The test devices are turned on once a month.
You need to prevent Server1 from assigning the IP addresses allocated to the test devices to other devices when the test devices are offline. The solution must minimize administrative effort.
What should you do?
- A. Create a policy.
- B. Create reservations.
- C. Configure the Scope options.
- D. Create an exclusion range. Correct
Explanation
Creating an exclusion range for the IP addresses used by TestDevice1 to TestDevice4 prevents Server1 from assigning these addresses to other devices when they are offline, minimizing administrative effort.
You have an Active Directory Domain Services (AD DS) domain. The domain contains three servers named Server1, Server2, and Server3 that run Windows Server.
You sign in to Server1 by using a domain account and start a remote PowerShell session to Server2. From the remote PowerShell session, you attempt to access a resource on Server3, but access to the resource is denied.
You need to ensure that your credentials are passed from Server1 to Server3. The solution must minimize administrative effort.
What should you do?
- A. Configure Kerberos constrained delegation. Correct
- B. Configure Just Enough Administration (JEA).
- C. Configure selective authentication for the domain.
- D. Disable the Enforce user logon restrictions policy setting for the domain.
Explanation
Configuring Kerberos constrained delegation allows Server2 to pass the credentials of the user signed in on Server1 to Server3 for accessing resources, thereby resolving the access issue with minimal administrative effort.
You have an Active Directory Domain Services (AD DS) domain. The domain contains a member server named Server1 that runs Windows Server.
You need to ensure that you can manage password policies for the domain from Server1.
Which command should you run first on Server1?
- A. Install-WindowsFeature RSAT-AD-Tools
- B. Install-WindowsFeature RSAT-ADRMS
- C. Install-WindowsFeature GPMC Correct
- D. Install-WindowsFeature RSAT-AD-PowerShell
Explanation
The GPMC (Group Policy Management Console) is necessary to manage password policies for the domain through Group Policy Objects (GPOs). Installing RSAT-AD-Tools alone does not provide this capability.
Your network contains an Active Directory Domain Services (AD DS) domain. The domain contains two servers named Server1 and Server2 that run Windows Server 2022.
You plan to deploy an app named App1 that will be load balanced between Server1 and Server2.
You need to create an identity that will be used to run App1 on Server1 and Server2. The solution must meet the following requirements:
• The password for the identity must be changed regularly.
• Administrative effort must be minimized.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Explanation
1. Create a Key Distribution Services (KDS) root key (Add-KdsRootKey). Domain controllers use the KDS root key to generate gMSA passwords, so it must exist before you can create a gMSA.
2. Create a group managed service account (gMSA) (New-ADServiceAccount) and allow Server1 and Server2 to retrieve its password. A gMSA can be used on several servers at once, which suits App1's load-balanced deployment. AD changes its password automatically, so it is changed regularly with no administrative effort.
3. Install the service account on Server1 and Server2 (Install-ADServiceAccount), then configure App1 to run as it.
An sMSA can be used on only one computer, so it cannot serve both load-balanced servers. Creating an SPN or enabling constrained delegation does not create the identity or manage its password.
Your network contains an Active Directory Domain Services (AD DS) domain. The domain contains a server named Server1.
On Server1, you install Windows Admin Center and use Windows Admin Center to remove BUILTIN\Users from the allowed groups.
You discover that all users can still sign in to Windows Admin Center.
You need to prevent unauthorized users from signing in to Windows Admin Center.
What should you do in Windows Admin Center?
- A. Set Performance Profile to On.
- B. Set Require manage-as sessions to re-authenticate to On.
- C. From the Proxy settings, configure a bypass list.
- D. Add a security group to the allowed groups. Correct
Explanation
Adding a security group to the allowed groups restricts access to Windows Admin Center to only members of that specified group, thereby preventing unauthorized users from signing in.
You have on-premises servers that run Windows Server as shown in the following table.
| Name | Type |
|---|---|
| Server1 | Physical server |
| VM2 | Hyper-V virtual machine |
You have an Azure subscription that contains a virtual machine named VM1.
You need to ensure that you can manage all the servers by using Azure Arc. The solution must minimize administrative effort.
On which servers should you install the Azure Connected Machine agent?
- A. Server1 only
- B. VM1 only
- C. VM2 only
- D. VM1 and VM2 only
- E. Server1 and VM2 only Correct
- F. Server1, VM1, and VM2
Explanation
Install the Azure Connected Machine agent on Server1 and VM2 only. Azure Arc-enabled servers projects machines that run outside Azure (physical servers and on-premises Hyper-V VMs such as Server1 and VM2) into Azure Resource Manager. VM1 is already an Azure virtual machine managed natively by Azure Resource Manager, and installing the Connected Machine agent on an Azure VM is not supported (it is only for test scenarios with special configuration), so no agent is needed or allowed on VM1.
Your network contains an Active Directory Domain Services (AD DS) domain. The domain contains the servers shown in the following table.
| Name | Type |
| --- | --- |
| DC1 | Domain controller |
| Server1 | Member server |
| Server2 | Member server |
The domain contains the users shown in the following table.
| Name | Member of |
| --- | --- |
| User1 | Contoso\Administrators |
| User2 | Contoso\Remote Management Users |
| User3 | Server2\Power Users |
On Server2, you run the Enable-PSRemoting cmdlet.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Explanation
Statement 1 (Yes): Enable-PSRemoting on Server2 starts WinRM, creates the listener, opens the firewall rules and registers the default Microsoft.PowerShell endpoint. By default, that endpoint lets administrators and members of Remote Management Users connect. User1 is treated as an administrator, so User1 can connect to Server2 from Server1.
Statement 2 (Yes): PowerShell remoting is on by default on Windows Server 2012 and later, including DC1. On a domain controller, the domain's built-in Remote Management Users group is the group the default endpoint authorizes. User2 is a member, so User2 can connect from Server2 to DC1.
Statement 3 (No): User3 is only a member of Server2's local Power Users group. That group is not on the default endpoint's access list, which allows only Administrators and Remote Management Users, so the connection is denied.
Your network contains an on-premises Active Directory Domain Services (AD DS) domain. The domain contains a user named User1 and the servers shown in the following table.
| Name | Operating system |
|------|------------------|
| Server1 | Windows Server 2016 |
| Server2 | Windows Server 2022 |
| Backup1 | Windows Server 2019 |
User1 is a member of the Protected Users security group.
User1 performs the following actions:
• From Server1, establishes a remote PowerShell session on Server2
• From the PowerShell session on Server2, attempts to access a resource on Backup1
The request to access the resource on Backup1 is denied.
You need to ensure that User1 can access the resources on Backup1 by using the PowerShell session on Server2. The solution must follow the principle of least privilege and minimize administrative effort.
What should you configure?
- A. Kerberos delegation (unconstrained)
- B. CredSSP
- C. PSSessionConfiguration by using RunAs Correct
- D. resource-based Kerberos constrained delegation
Explanation
User1 is a member of Protected Users, and accounts in that group cannot be delegated with unconstrained or constrained delegation (resource-based constrained delegation included), and CredSSP does not work for them, so options A, B and D all fail for this user. A PowerShell session configuration registered on Server2 with a RunAs credential (Register-PSSessionConfiguration -RunAsCredential) runs the commands in User1's session under a separate account, so Server2 reaches Backup1 with that account's own credentials and no delegation of User1's credentials is needed. Give the RunAs account access only to the required resource on Backup1 and allow only User1 to use the endpoint, which follows least privilege and is configured on one server.
You have 50 on-premises servers that run Windows Server.
You have an Azure subscription.
You plan to monitor the on-premises servers by using Azure Monitor.
You need to collect event logs from the on-premises servers.
What should you do first?
- A. From the Azure portal, create a storage account.
- B. From the Azure portal, create a Log Analytics workspace. Correct
- C. From the on-premises servers, run azuremonitoragentclientsetup.msi.
- D. From the Azure portal, create a data collection rule (DCR) in Azure Monitor.
Explanation
A Log Analytics workspace is required to store and analyze the event logs collected from on-premises servers. Creating this workspace first ensures that there is a destination for the data collected by Azure Monitor agents installed on the servers.
Your network contains an Active Directory Domain Services (AD DS) domain. The domain contains servers that run Windows Server and computers that run Windows.
You link a Group Policy Object (GPO) to the domain and set Turn on BranchCache to Enabled.
You need to enable BranchCache in BranchCache Distributed Cache mode.
What should you configure on the computers?
- A. Background Intelligent Transfer Service (BITS)
- B. Offline Files
- C. Advanced sharing settings
- D. Windows Firewall inbound traffic rules Correct
Explanation
To enable BranchCache in Distributed Cache mode, Windows Firewall inbound traffic rules must be configured to allow the necessary network traffic. This ensures that computers can communicate with each other for caching content.
Your network contains an Active Directory Domain Services (AD DS) domain. The domain contains the servers shown in the following table.
| Name | Description |
|---|---|
| Server1 | Has Windows Admin Center installed |
| Server2 | Has the DHCP Server role installed |
You need to ensure that from Server1, you can use Windows Admin Center to manage the DHCP Server role on Server2.
What should you do first?
- A. Install the DHCP Server Tools feature on Server1.
- B. Install a Windows Admin Center extension. Correct
- C. Install the DHCP Server Tools feature on Server2.
- D. Modify the PowerShell remoting settings for Server2.
Explanation
In Windows Admin Center, the DHCP tool is not built in. Microsoft provides it as an extension on the Windows Admin Center extension feed. Before you can view or manage DHCP scopes, exclusions and reservations on Server2, you must first install the DHCP extension in Windows Admin Center on Server1 (Settings > Extensions). Installing the DHCP Server Tools on Server1 is not needed, because Windows Admin Center runs its management commands remotely on the target server, not on the gateway. If the DHCP PowerShell module is missing on Server2, the DHCP tool prompts you to install it later, but the extension comes first. Changing the PowerShell remoting settings on Server2 is not required, because Windows Admin Center already uses WinRM to manage domain-joined servers.
Your network contains an Active Directory Domain Services (AD DS) domain. The domain contains three servers named SRV1, SRV2, and SRV3 that run Windows Server. The domain contains a user named User1.
You plan to perform the following tasks:
• Sign in to SRV1 as User1.
• Establish a PowerShell remoting session from SRV1 to SRV2.
• From the remoting session, invoke a command that targets SRV3 and runs the command in the security context of User1.
You need to configure resource-based Kerberos constrained delegation to support the planned tasks.
How should you complete the PowerShell script? To answer, select the appropriate options in the answer area.
```powershell
$SRV1 = $env:COMPUTERNAME
$SRV2 = Get-ADComputer -Identity SRV2
$SRV3 = Get-ADComputer -Identity SRV3
Set-ADComputer -Identity [1] -PrincipalsAllowedToDelegateToAccount [2]
```
NOTE: Each correct selection is worth one point.
Explanation
Set-ADComputer -Identity: $SRV3 — Resource-based Kerberos constrained delegation is configured on the *resource* (target) computer account, not on the front-end or middle-tier server, so the object being modified is SRV3, the machine that finally receives the command and must accept a delegated ticket for User1. Choosing $SRV1 or $SRV2 would set the attribute on the client or the intermediary, which has no effect on whether SRV3 honours the forwarded identity.
-PrincipalsAllowedToDelegateToAccount: $SRV2 — This parameter writes the msDS-AllowedToActOnBehalfOfOtherIdentity attribute on SRV3, naming the account permitted to obtain a service ticket to SRV3 on behalf of another user; that account is SRV2, the middle-tier server hosting the PowerShell remoting session that must impersonate User1 when it reaches out to SRV3. $SRV1 is only the originating client and never requests the second-hop ticket itself, and $SRV3 cannot be its own delegating principal.
You have 100 on-premises servers that run Windows Server and are Azure Arc-enabled.
You have an Azure subscription.
You deploy a Custom Script Extension to the servers by using the following Azure Resource Manager (ARM) template.
You regenerate the storage account key and update the template.
You need to meet the following requirements:
• Ensure that the script runs again on the servers.
• Minimize the risk of the key being compromised on the servers.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Explanation
To ensure that the script runs again: Modify the value of the timestamp property. The Custom Script Extension runs a script only once. It runs it again only when the extension configuration changes. The timestamp setting exists for exactly this purpose: change it to any integer different from the previous value to trigger a rerun. Setting autoUpgradeMinorVersion to true only allows newer minor versions of the extension handler to be used and does not rerun the script. Raising typeHandlerVersion selects a different handler version and is not the supported way to rerun the script.
To minimize the risk of a compromised key: Move the storageAccountName property and the storageAccountKey property to the protectedSettings object. Public settings are sent to the server in clear text and saved there that way. Protected settings are encrypted with a key known only to Azure and the machine. The documentation also requires storageAccountName and storageAccountKey to be placed together in protectedSettings. Managed identity is not an option here. The Custom Script Extension does not currently support managed identity authentication on Azure Arc-enabled servers. The managedIdentity property must also be specified only in protected settings and cannot be combined with storageAccountName, which both managedIdentity options leave in place.
Your network contains an Active Directory Domain Services (AD DS) domain named contoso.com. The domain contains two servers named Server1 and Server2 that run Windows Server. The domain contains two users named User1 and User2.
You perform the following tasks:
• Enable Remote SSH Access on Server2.
• Sign in to Server1 as User1.
You need to establish an SSH session from Server1 to Server2 and sign in as User2.
Which command should you run?
- A. sshd Contoso\User2@Server2
- B. ssh Contoso\User2@Server2 Correct
- C. ssh Server2 Contoso\User2
- D. sshd Server2 Contoso\User2
Explanation
The correct command to establish an SSH session from Server1 to Server2 and sign in as User2 is 'ssh Contoso\User2@Server2'. This uses the standard SSH syntax where 'Contoso\User2' specifies the user and domain, and '@Server2' indicates the target server.
You have a server that runs Windows Server and contains 10 physical disks.
You plan to implement storage spaces that will use the disks.
You are evaluating whether to configure the following options:
• A two-way mirror
• A parity storage layout
What is the maximum number of disks that can fail without data loss for each option? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Explanation
Two-way mirror: 1 — A two-way mirror in Storage Spaces keeps two copies of every slab of data on separate physical disks, so any single disk can fail and a complete second copy of all data remains available. Losing two disks could take out both copies of the same slab, so 1 is the maximum guaranteed fault tolerance; only a three-way mirror (three copies, minimum five disks) survives two simultaneous failures.
Parity storage layout: 2 — With 10 physical disks the server meets the seven-disk minimum for dual parity, which writes two independent parity symbols per stripe and therefore tolerates the loss of two disks without data loss while still being far more capacity-efficient than mirroring. Single parity would only survive 1 failure, but the disk count here allows the dual-parity layout, so 2 is the maximum for a parity configuration on this server.
You have a server named Host1 that has the Hyper-V server role installed. Host1 hosts a virtual machine named VM1.
You have a management server named Server1 that runs Windows Server. You remotely manage Host1 from Server1 by using Hyper-V Manager.
You need to ensure that you can access a USB hard drive connected to Server1 when you connect to VM1 by using Virtual Machine Connection.
Which two actions should you perform? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
- A. From the Hyper-V Settings of Host1, select Allow enhanced session mode. Correct
- B. From Virtual Machine Connection, select Show Options, and then select the USB hard drive. Correct
- C. From Virtual Machine Connection, switch to a basic session.
- D. From Disk Management on Host1, select Rescan Disks.
- E. From Disk Management on Host1, attach a virtual hard disk.
Explanation
Option A enables enhanced session mode on Host1, which is necessary for USB redirection. Option B allows selecting the USB hard drive from Server1 when connecting to VM1 via Virtual Machine Connection.
You have a Windows Server container host named Server1 and a container image named image1.
You need to start a container from image1. The solution must run the container on a Hyper-V virtual machine.
Which parameter should you specify when you run the docker run command?
- A. --expose
- B. --privileged
- C. --runtime
- D. --isolation Correct
- E. --entrypoint
Explanation
The --isolation parameter is used to specify the isolation technology for Windows containers. Setting it to 'hyperv' ensures that the container runs in a Hyper-V isolated environment, which meets the requirement of running the container on a Hyper-V virtual machine.
You plan to deploy a containerized application that requires .NET Core.
You need to create a container image for the application. The image must be as small as possible.
Which base image should you use?
- A. Windows Server
- B. Nano Server Correct
- C. Windows
- D. Server Core
Explanation
Nano Server provides the smallest base container image size suitable for .NET Core applications. It is optimized for cloud and server workloads with a minimal set of APIs, making it ideal for creating lightweight container images.
You have an Azure virtual machine named VM1 that runs Windows Server.
You perform the following actions on VM1:
✑ Create a folder named Folder1 on volume C.
✑ Create a folder named Folder2 on volume D.
✑ Add a new data disk to VM1 and create a new volume that is assigned drive letter E.
✑ Install an app named App1 on volume E.
You plan to resize VM1.
Which objects will present after you resize VM1?
- A. Folder1, volume E, and App1 only Correct
- B. Folder1 only
- C. Folder1 and Folder2 only
- D. Folder1, Folder2, App1, and volume E
Explanation
In Azure, the D drive is typically used as a temporary disk that gets wiped during a VM resize operation. Therefore, Folder2 on volume D will not be present after resizing. Volume E and App1 installed there persist because they are on an additional data disk.
You have an Azure virtual machine named VM1 that runs Windows Server and has the following configurations:
✑ Size: D2s_v4
✑ Operating system disk: 127-GiB standard SSD
✑ Data disk 128-GiB standard SSD
✑ Virtual machine generation: Gen 2
You plan to perform the following changes to VM1:
✑ Change the virtual machine size to D4s_v4.
✑ Detach the data disk.
✑ Add a new standard SSD.
Which changes require downtime for VM1?
- A. Detaching the data disk only and adding a new standard SSD.
- B. Detaching the data disk only.
- C. Changing the virtual machine size only. Correct
- D. Adding a new standard SSD only.
Explanation
Changing the virtual machine size requires downtime because resizing a VM will cause it to reboot. Detaching and adding data disks can be done without causing downtime.
You have a Windows Server container host named Server1 that has a single disk.
On Server1, you plan to start the containers shown in the following table.
| Name | Description |
| --- | --- |
| Container1 | Container1 is a Windows container that contains a web app in development. The container must NOT share a kernel with other containers. |
| Container2 | Container2 is a Linux container that runs a web app. The container requires two static IP addresses. |
| Container3 | Container3 is a Windows container that runs a database. The container requires a static IP address. |
Which isolation mode can you use for each container? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Explanation
Container1: Hyper-V isolation only. Process-isolated containers share the host's kernel with the host and with each other. Hyper-V isolation runs each container in its own lightweight utility VM with its own kernel, so it is the only mode that meets the requirement that Container1 must not share a kernel with other containers.
Container2: Hyper-V isolation only. Containers share the kernel of the host they run on, so a Linux container cannot run directly on the Windows kernel with process isolation. On a Windows host, a Linux container runs inside a lightweight Hyper-V VM that supplies a Linux kernel. Static IP addresses are a networking setting and do not change which isolation mode is possible.
Container3: Hyper-V isolation or process isolation. Container3 is a Windows container with no kernel-separation requirement, and a static IP address can be assigned in either mode (for example, on a transparent or l2bridge network). Both process isolation and Hyper-V isolation are therefore supported.
You have a server named Server1 that runs Windows Server and has the Hyper V server role installed. Server1 hosts a virtual machine named VM1.
Server1 has an NVMe storage device. The device is currently assigned to VM1 by using Discrete Device Assignment.
You need to make the device available to Server1.
Which four actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Explanation
Stopping VM1 ensures no active processes interfere with the device. Removing the device from VM1 and mounting it back to Server1 allows the NVMe storage to be reassigned to the host server. Enabling the device on Server1 makes it available for use.
You have a server named Server1 that hosts Windows containers.
You plan to deploy an application that will have multiple containers. Each container will be on the same subnet. Each container requires a separate MAC address and IP address. Each container must be able to communicate by using its IP address.
You need to create a Docker network that supports the deployment of the application.
Which type of network should you create?
- A. NAT
- B. transparent Correct
- C. l2bridge
- D. l2tunnel
Explanation
The 'transparent' network driver directly connects containers to the physical network through an external Hyper-V switch, allowing each container to have a separate MAC and IP address for direct communication.
You have an on-premises Active Directory Domain Services (AD DS) domain that syncs with an Azure Active Directory (Azure AD) tenant.
You plan deploy 100 new Azure virtual machines that will run Windows Server.
You need to ensure that each new virtual machine is joined to the AD DS domain.
What should you use?
- A. an Azure Resource Manager (ARM) template Correct
- B. a Group Policy Object (GPO)
- C. Azure AD Connect
- D. an Azure management group
Explanation
An Azure Resource Manager (ARM) template is the correct choice for automating the deployment and configuration of multiple Azure virtual machines, including joining them to an on-premises AD DS domain. ARM templates allow for consistent and automated deployments with included extensions that can configure VMs during setup.
Your network contains an on-premises Active Directory Domain Services (AD DS) domain named contoso.com. The domain contains three servers that run
Windows Server and have the Hyper-V server role installed. Each server has a Switch Embedded Teaming (SET) team.
You need to verify that Remote Direct Memory Access (RDMA) and all the required Windows Server settings are configured properly on each server to support an
Azure Stack HCI cluster.
What should you use?
- A. Server Manager
- B. the Get-NetAdapter cmdlet
- C. Failover Cluster Manager
- D. the Validate-DCB cmdlet Correct
Explanation
The Validate-DCB cmdlet is specifically designed to verify that Remote Direct Memory Access (RDMA) and all required Windows Server settings are configured properly for an Azure Stack HCI cluster. This tool checks the configuration of Data Center Bridging (DCB) and RDMA on each server, ensuring they meet the necessary requirements.
You plan to deploy an Azure virtual machine that will run Windows Server.
You need to ensure that an Azure Active Directory (Azure AD) user named User1 can connect to the virtual machine by using the Azure Serial
Console.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Hot Area:
Explanation
Configure on the Azure virtual machine: Boot diagnostics with a custom storage account — the Azure Serial Console attaches to the VM's serial port through the boot diagnostics channel, so boot diagnostics must be enabled on the VM before the console will connect; without it the Serial Console reports that it is unavailable. Operating system guest diagnostics only collects in-guest performance counters and logs through the diagnostics extension and does nothing for serial port access, and a system-assigned managed identity governs how the VM authenticates to other Azure resources, not how an administrator reaches its console.
Assign the following role to User1: Virtual Machine Contributor — access to the Serial Console requires at minimum the Virtual Machine Contributor role on the virtual machine, because opening the console is a control-plane operation on the VM resource rather than a guest sign-in. Virtual Machine Administrator Login and Virtual Machine User Login only grant Azure AD-based sign-in rights inside the guest over RDP or SSH (as a local administrator or as a standard user, respectively) and do not carry the resource-level permission needed to open the Serial Console.
You have a Windows Server container host named Server1 and an Azure subscription.
You deploy an Azure container registry named Registry1 to the subscription.
On Server1, you create a container image named image1.
You need to store image1 in Registry1.
Which command should you run on Server1? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
The command has the form: [command] [action] Registry1.azurecr.io/image1
Hot Area:
Explanation
Select the command to use: docker — Server1 is a Windows Server container host, so the Docker CLI (installed with a container runtime such as Docker/Mirantis Container Runtime) is the tool that manages local container images and talks to an OCI-compliant registry such as Azure Container Registry. azcopy is for Azure Blob/File data transfer, xcopy is a plain file-copy utility, and git works with source repositories — none of them understand container image manifests or layers, so none can upload image1 to Registry1.
Select the action to perform: push — after tagging image1 with the registry login server name (registry1.azurecr.io/image1) and authenticating with az acr login or docker login, docker push uploads the image layers and manifest into Registry1. pull works in the opposite direction (downloading an image from the registry to the host), while docker export and docker import move a container's filesystem to and from a local tar archive rather than transferring an image to a remote registry.
You plan to deploy an Azure virtual machine that will run Windows Server. The virtual machine will host an Active Directory Domain Services (AD DS) domain controller and a drive named F: on a new virtual disk.
You need to configure storage for the virtual machine. The solution must meet the following requirements:
* Maximize resiliency for AD DS.
* Prevent accidental data loss.
How should you configure the storage? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Hot Area:
Explanation
Volume for the AD DS database: F — The AD DS database (NTDS.dit), its log files, and SYSVOL must be placed on a dedicated Azure data disk, which is the new virtual disk mounted as F:. C: is the OS disk and is not the supported location for the directory database on an Azure domain controller, and D: in an Azure VM is the temporary (ephemeral) local disk whose contents are lost on deallocation, host maintenance, or resize — placing the database there would guarantee eventual data loss rather than prevent it.
Caching configuration for the volume that hosts the database: NONE — Azure host caching must be set to None on the data disk holding the AD DS database and logs, because AD DS relies on write-through semantics and forced-unit-access writes to guarantee transaction durability, and host-level write caching can acknowledge or reorder writes in a way that corrupts the ESE database after an unclean shutdown. READ/WRITE is the specific configuration Microsoft warns against for domain controllers, and even READ caching is not the supported setting for the volume hosting the database, since only NONE preserves the durability guarantees AD DS expects.
You create an Azure virtual machine named Server1 that runs Windows Server.
Server1 has the disk configurations shown in the following exhibit.
You need to create a new 100-GB volume on Server1.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Explanation
The exhibit shows that Disk 0 (the OS disk) is fully allocated and Disk 1 is the 8-GB temporary disk, whose data is not persistent, so there is no space for a 100-GB volume. First, create and attach a new data disk to Server1 in Azure; data disks can be hot-added to a running VM, so there is no need to shut down or restart Server1. Next, initialize the new disk in Disk Management so Windows can use it. Finally, create a new simple volume on the disk; a spanned volume is only needed to combine free space from several disks, which is not the case here.
You have an Azure virtual machine named Server1 that runs a network management application. Server1 has the following network configurations:
* Network interface: Nic1
* IP address: 10.1.1.1/24
* Connected to: Vnet1/Subnet1
You need to connect Server1 to an additional subnet named Vnet1/Subnet2.
What should you do?
- A. Modify the IP configurations of Nic1.
- B. Add an IP configuration to Nic1.
- C. Add a network interface to Server1. Correct
- D. Create a private endpoint on Subnet2.
Explanation
To connect Server1 to an additional subnet named Vnet1/Subnet2, you need to add a network interface (Nic2) to Server1. Each network interface can be connected to a different subnet within the same virtual network.
You have a server named Server1 that runs Windows Server 2019 and hosts a container named Container1. Container1 uses a Windows Server 2019 base image that was built by using a Docker file.
You upgrade Server1 to Windows Server 2022.
You need to ensure that Container1 will run on Server1. The solution must minimize administrative effort.
What should you do?
- A. Start Container1 in Hyper-V isolation mode. Correct
- B. Modify the Docker file.
- C. Start Container1 in process isolation mode.
- D. Rebuild the base image for Container1.
Explanation
On a Windows Server 2022 host, a container whose base image is Windows Server 2019 is supported only with Hyper-V isolation; process isolation requires the host and image build numbers to match, so starting Container1 in process isolation mode fails with an OS mismatch error. Starting Container1 with Hyper-V isolation (for example, docker run --isolation=hyperv) gives the container its own matching kernel, so it runs without any change to the image. Modifying the Docker file and rebuilding the image onto a Windows Server 2022 base would also work, but it takes more administrative effort than simply changing the isolation mode.
You have an Azure subscription that contains the virtual networks shown in the following table.
| Name | Subnet | Location |
|---|---|---|
| VNet1 | Subnet11, Subnet12 | West US |
| VNet2 | Subnet21 | West US |
| VNet3 | Subnet31 | Central US |
You deploy a virtual machine named VM1 that runs Windows Server. VM1 is connected to Subnet11.
You plan to add an additional network interface named NIC1 to VM1.
To which subnets can NIC1 be attached?
- A. Subnet11 only
- B. Subnet12 only
- C. Subnet11 and Subnet12 only Correct
- D. Subnet12 and Subnet21 only
- E. Subnet11, Subnet12, Subnet21, and Subnet31
Explanation
VM1 is connected to Subnet11 in VNet1. According to Azure networking principles, a virtual machine can have multiple network interfaces (NICs) that can be attached to different subnets within the same virtual network. Therefore, NIC1 can be attached to either Subnet11 or Subnet12 within VNet1.
You have an Azure subscription. The subscription contains a virtual machine named VM1 that runs Windows Server. VM1 contains a 128-GB operating system disk.
You need to increase the size of volume C on VM1 to 250 GB.
Which four actions should you perform in sequence.
To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Explanation
To increase the size of volume C on a Windows Server virtual machine in Azure, you must first stop the VM to resize its operating system disk. After resizing the disk, start the VM and then resize volume C to utilize the additional space.
You have an Azure subscription that contains a virtual machine named VM1 as shown in the following exhibit.
The subscription has the disks shown in the following table.
| Name | Resource group | Location | Availability zone |
|---|---|---|---|
| Disk1 | RG1 | East US | None |
| Disk2 | RG2 | East US | 1 |
| Disk3 | RG1 | Central US | None |
| Disk4 | RG1 | Central US | 1 |
Which disks can you attach as data disks to VM1?
- A. Disk2 only Correct
- B. Disk4 only
- C. Disk1 and Disk2 only
- D. Disk2 and Disk4 only
- E. Disk1, Disk3, and Disk4 only
- F. Disk1, Disk2, Disk3, and Disk4
Explanation
The exhibit shows that VM1 runs in East US, availability zone 1. A managed data disk must be in the same region as the VM, and a zonal VM can attach a zonal (locally redundant) disk only when the disk is in the same zone as the VM. The resource group does not matter: a VM can attach a disk from a different resource group.
Disk2 is in East US, zone 1, so it can be attached, even though it is in RG2.
Disk1 is in East US but is a regional disk with no zone pinned to zone 1, so it cannot be attached to the zonal VM1.
Disk3 and Disk4 are in Central US, a different region, so neither can be attached.
Only Disk2 can be attached as a data disk to VM1.
Your on-premises network contains a server named Server1 and uses an IP address space of 192.168.10.0/24.
You have an Azure virtual network that contains a subnet named Subnet1. Subnet1 uses an IP address space of 192.168.10.0/24.
You need to migrate Server1 to Subnet1. You must use Azure Extended Network to maintain the existing IP address of Server1.
What is the minimum number of virtual machines that you should deploy? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Explanation
Azure Extended Network stretches an on-premises subnet into Azure by using a bidirectional VXLAN tunnel between two virtual appliances, and each extended subnet needs exactly one pair of appliances. Only one subnet (192.168.10.0/24) is extended here, so the minimum is one pair.
Virtual machines that run Windows Server 2022 Azure Edition: 1. The appliance in Azure must run Windows Server 2022 Datacenter: Azure Edition (Windows Admin Center lists only Azure Edition VMs for this role). It has Hyper-V enabled, its primary network interface on a routable subnet and a second network interface on the extended subnet, Subnet1.
Virtual machines that run Windows Server 2019 or Windows Server 2022: 1. The on-premises appliance can run Windows Server 2019 or Windows Server 2022 on a hypervisor that supports nested virtualization, connected to the routable subnet and to the 192.168.10.0/24 subnet being extended. Server1 then keeps its IP address after it moves to Subnet1.
You have a server named Server1 that has the Hyper-V server role installed. Server1 hosts the virtual machines shown in the following exhibit.
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.
Explanation
The exhibit shows the configuration version of each virtual machine: VM1 is 10.0, VM2 is 9.0 and VM3 is 8.0. Several Hyper-V features require a minimum virtual machine configuration version.
Production checkpoints: VM1, VM2, and VM3. Production checkpoints require configuration version 6.2 or later, and all three virtual machines meet that minimum.
Hibernation: Only VM1 and VM2. Hibernation support requires configuration version 9.0 or later. VM1 (10.0) and VM2 (9.0) meet it, but VM3 (8.0) does not; VM3 would need its configuration version upgraded (with Update-VMVersion while it is shut down) before it could be hibernated.
You have an Azure subscription. The subscription contains a virtual machine named VM1 that runs Windows Server.
You build an app named App1.
You need to configure continuous integration and continuous deployment (CI/CD) of App1 to VM1.
What should you create first?
- A. an App Service Environment
- B. an Azure DevOps organization Correct
- C. a managed identity
- D. an Azure Automation account
Explanation
To configure CI/CD for an application deployed to a Windows Server virtual machine in Azure, creating an Azure DevOps organization is necessary. This provides the tools and services required to implement continuous integration and deployment processes.
You have a Windows Server container host named Server1.
You start the containers on Server1 as shown in the following table.
You need to validate the status of ProcessA and ProcessC.
Where can you verify that ProcessA and ProcessC are in a running state? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
| Name | Image | Uses Hyper-V isolation | Process running on container |
| --- | --- | --- | --- |
| Container1 | microsoft/iis | No | ProcessA |
| Container2 | microsoft/iis | No | ProcessB |
| Container3 | microsoft/iis | Yes | ProcessC |
| Container4 | microsoft/iis | Yes | ProcessD |
Explanation
ProcessA: Container1 and Server1 only. Container1 uses process isolation, so it shares the kernel with the host. A process running in it is a real process on Server1 and appears in Get-Process on the host with the same process ID it has inside the container. Windows containers still isolate the process and thread ID space per container, so ProcessA is not visible from Container2, Container3 or Container4.
ProcessC: Container3 only. Container3 uses Hyper-V isolation, so it runs inside its own lightweight utility VM with its own kernel. ProcessC exists only in that VM. On Server1, searching for the process with Get-Process fails, and only the vmwp worker process that hosts the utility VM is visible. Other containers cannot see it either, because each Hyper-V isolated container has its own kernel boundary.
You have an Azure subscription that contains the virtual machines shown in the following table.
| Name | Operating system |
| --- | --- |
| VM1 | Windows Server 2022 Datacenter: Azure Edition |
| VM2 | Windows Server 2022 Datacenter: Azure Edition Core |
| VM3 | Windows Server 2022 Datacenter |
| VM4 | Windows Server 2019 Datacenter |
You plan to implement Azure Automanage for Windows Server.
You need to identify the operating system prerequisites.
Which virtual machines support Hotpatch, and which virtual machines support SMB over QUIC? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Explanation
Hotpatch: VM2 only. Windows Server 2022 Hotpatch works only on specific Azure Edition images. The standard image for this is the Server Core image (2022-Datacenter-Azure-Edition-Core). A Desktop Experience VM supports Hotpatch only when it is deployed from the separate 2022-Datacenter-Azure-Edition-Hotpatch image, not from the regular Azure Edition image that VM1 uses. Windows Server 2022 Datacenter (VM3) and Windows Server 2019 Datacenter (VM4) are not Azure Edition, so they cannot use Hotpatch.
SMB over QUIC: VM1 and VM2 only. For Windows Server 2022, the SMB over QUIC server role requires Windows Server 2022 Datacenter: Azure Edition. Both installation options of that edition are supported: Desktop Experience (VM1) and Server Core (VM2). Automanage machine best practices then keep SMB over QUIC enabled and watch its certificate. VM3 and VM4 are not Azure Edition, so they cannot act as SMB over QUIC servers.
You have an Azure subscription that contains a virtual network named VNet1. Vnet1 contains three subnets named Subnet1, Subnet2, and Subnet3.
You deploy a virtual machine that has the following settings:
• Name:VM1
• Subnet: Subnet2
• Network interface name: NIC1
• Operating system: Windows Server 2022
You need to ensure that VM1 can route traffic between Subnet1 and Subnet3. The solution must minimize administrative effort.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Explanation
From the Azure portal: Enable IP forwarding for NIC1. — By default the Azure software-defined network drops any packet arriving at a NIC whose destination IP does not match one of that NIC's own IP configurations, so VM1 could never pass traffic on behalf of Subnet1 and Subnet3; enabling IP forwarding on NIC1 tells the Azure host to allow VM1 to send and receive packets addressed to other IPs, which is the prerequisite for any NVA-style routing VM. Associating a route table with Subnet2 is not the answer here, because a user-defined route on Subnet2 controls where traffic leaving Subnet2 goes rather than granting VM1 the right to forward transit traffic, and attaching two more interfaces is unnecessary since a single NIC in Subnet2 can route between the other subnets over the VNet's built-in system routes.
On VM1: Run the route add command. — Inside the guest, Windows Server 2022 needs routing entries pointing to the Subnet2 default gateway (the .1 address of the subnet) for the Subnet1 and Subnet3 prefixes, and `route add -p` (or the equivalent New-NetRoute) creates those persistent entries with a single command and no role installation. Installing and configuring Routing and Remote Access would add a server role, RRAS configuration, and ongoing management for a result the routing table already provides, so it does not minimize administrative effort, and Network Controller is the SDN management role for on-premises Hyper-V fabrics, not a router for an Azure VM.
You have an Azure subscription and a computer named Computer1 that runs Windows 11.
From the Azure portal, you deploy a virtual machine named VM1 that runs Windows Server. You configure VM1 to use the default settings.
You need to ensure that you can connect to VM1 by using PowerShell remoting.
Which cmdlet should you run, and what should you use to run the cmdlet? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Explanation
Run from: Azure Cloud Shell. Enable-AzVMPSRemoting is an Azure PowerShell cmdlet that works against the VM as an Azure resource. It uses the Azure control plane (Run Command) to turn on remoting inside the guest and adds the network security group rule that allows WinRM traffic, so you run it from an Azure PowerShell session that is signed in to the subscription. Microsoft's documentation runs it from Azure Cloud Shell, which already has the Az modules and an authenticated session. A PowerShell session on VM1 is not the right place, because the cmdlet manages the VM from outside, and a VM deployed with the default settings does not allow inbound WinRM to start with.
Cmdlet: Enable-AzVMPsRemoting. It is the only option that configures both the guest (the WinRM listener and firewall) and the Azure network path in one step. Enable-PSRemoting -Force only configures the computer it runs on and leaves the NSG closed. Enable-PSSessionConfiguration only re-enables session configuration endpoints that already exist on that computer.
You have a server named Server1 that runs Windows Server and has the Hyper-V server role installed. Server1 contains a virtual machine named VM1 that runs Windows Server.
You need to install the Hyper-V server role on VM1.
Which PowerShell command should you run first? To answer, select the appropriate options in the answer area.
The command has the form: [Cmdlet] [Parameter] $true
NOTE: Each correct selection is worth one point.
Explanation
Cmdlet: Set-VMProcessor VM1. To run Hyper-V inside a virtual machine you must enable nested virtualization, and that is a processor setting of the VM. You run Set-VMProcessor on the physical host (Server1) while VM1 is turned off, then start VM1 and install the Hyper-V role in it. Set-VMHost changes host-wide settings, and Set-VM, Set-VMFirmware and Set-VMSecurity do not expose virtualization extensions.
Parameter: -ExposeVirtualizationExtensions. Set-VMProcessor VM1 -ExposeVirtualizationExtensions $true passes the processor's virtualization extensions (Intel VT-x or AMD-V) through to VM1, which Hyper-V needs to install and run. -EnableEnhancedSessionMode is a Set-VMHost setting for Virtual Machine Connection sessions, -EnableHostResourceProtection limits a VM's use of host resources, and -CompatibilityForOlderOperatingSystemsEnabled limits the processor features for old guest operating systems.
You have a Windows Server 2022 container host named Host1 and a container registry that contains the container images shown in the following table.
You need to run the containers on Host1.
Which isolation mode can you use for each image? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
| Name | Container base image OS version |
| --- | --- |
| Image1 | Windows Server 2022 |
| Image2 | Windows Server 2019 |
Explanation
Image1: Hyper-V isolation or process isolation — Image1's base operating system matches Host1's Windows Server 2022 build, and process isolation is only supported when the container image's OS version matches the container host's OS version, because the containers share the host kernel directly. Since the versions match, process isolation works, and Hyper-V isolation is always available as well on a Windows Server container host, so both modes are valid for Image1.
Image2: Hyper-V isolation only — Image2 is based on a different Windows Server release than Host1, so it cannot share Host1's kernel and process isolation is not supported for it. Hyper-V isolation runs the container inside a lightweight utility VM that supplies its own matching kernel, which is exactly how Windows lets you run a container image whose OS version differs from the host, so "Hyper-V isolation or process isolation" would be incorrect here.
You have an Azure virtual machine named VM1 that contains the drives shown in the following table.
| Letter | Name |
|---|---|
| C | Operating System |
| D | Temporary Storage |
| E | Data Disk |
On VM1, you plan to install an app named App1. The data for App1 must be stored on a persistent data disk assigned to drive D.
You need assign the data disk to drive D.
What should you do on VM1 first?
- A. Change the drive letter of the Temporary Storage drive to F.
- B. Move pagefile.sys to the Operating System drive. Correct
- C. Stop (deallocate) VM1.
- D. Expand the Temporary Storage drive.
Explanation
The temporary storage drive (D:) holds pagefile.sys, so its drive letter cannot be changed while the page file is on it. First move pagefile.sys to the operating system drive (C:) and restart VM1. Then change the temporary drive's letter (for example to T:), assign D: to the data disk, and optionally move the page file back to the temporary drive. Stopping (deallocating) the VM or expanding the temporary drive does not free the letter, and changing the temporary drive letter cannot be done first because the page file is still on it.
Your on-premises network has an IP address range of 10.0.0.0/23.
You have an Azure virtual network named VNet1 that contains a virtual machine named VM1.
VNet1 has an IP address range of 10.0.1.0/24.
You need to deploy a Site-to-Site (S2S) VPN to connect the on-premises network to VNet1.
What should you do first?
- A. Deploy Azure Bastion to VNet1.
- B. Deploy Azure Extended Network.
- C. Configure VNet1 to use the IP address range of 10.0.2.0/24. Correct
- D. Configure VNet1 to use an IP address range of 10.0.1.128/25.
Explanation
The on-premises network IP range of 10.0.0.0/23 overlaps with VNet1's current IP range of 10.0.1.0/24, which would cause routing conflicts in a Site-to-Site (S2S) VPN setup. Changing VNet1’s IP address range to 10.0.2.0/24 avoids this overlap and ensures proper network connectivity.
You have a server that runs Windows Server 2022 and has the network adapters shown in the following table.
| Name | Vendor | Interface | Link speed | Remote Direct Memory Access (RDMA) support |
|---|---|---|---|---|
| LAN1 | Vendor1 | Network Adapter #1 | 1 Gbps | No |
| LAN2 | Vendor2 | Network Adapter #2 | 25 Gbps | Yes |
| LAN3 | Vendor3 | Network Adapter #3 | 25 Gbps | Yes |
| LAN4 | Vendor4 | Network Adapter #4 | 1 Gbps | No |
You need to configure NIC teaming for LAN2 and LAN3. The solution must support Dynamic Virtual Machine Multi-Queue (d.VMMQ).
What should you use?
- A. LACP teaming mode
- B. Switch Embedded Teaming (SET) Correct
- C. load balancing and failover (LBFO)
- D. Static teaming mode
Explanation
Switch Embedded Teaming (SET) is the correct choice for configuring NIC teaming with Dynamic Virtual Machine Multi-Queue (d.VMMQ) support on Windows Server 2022. SET provides advanced features like d.VMMQ and is designed to work seamlessly within the operating system, making it suitable for modern network requirements.
You have a server named Host1 that runs Windows Server 2022 and is configured as a container host. Host1 stores a container image named image1 that is based on Windows Server 2019.
You need to start a container from image1 on Host1.
How should you complete the command? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Command:
[Selection 1] run -d [Selection 2] image1
Explanation
Docker: containers on a Windows Server container host are started with the Docker CLI (docker run -d ...). MsiExec installs MSI packages, Start launches processes, and Start-VM starts Hyper-V virtual machines; none of them start a container from an image.
-isolation=hyperv: Process-isolated Windows Server containers share the host kernel, so the image's OS build must match the host's. On a Windows Server 2022 host, a Windows Server 2019 image supports only Hyper-V isolation. Hyper-V isolation runs the container in a lightweight utility VM with its own matching kernel, so the version mismatch does not matter. With -isolation=process, the container fails with the error 'The operating system of the container does not match the operating system of the host'. 'container' is not an isolation value.
You have a Windows Server container host named Server1.
You create a Dockerfile named df1.
You need to generate a container image by using df1.
Which command should you run?
- A. docker build Correct
- B. docker exec
- C. docker create
- D. docker images
Explanation
The command 'docker build' is used to generate a container image from a Dockerfile. The other commands listed do not serve this purpose: 'docker exec' runs a command in a running container, 'docker create' creates a new container but does not start it, and 'docker images' lists the available images.
You have a Windows Server 2022 container host named Host1 that has the Subsystem for Linux installed and the container images shown in the following table.
You need to deploy the images to Host1. The solution must maximize the isolation of the containers.
Which images can you run by using process isolation, and which images can you run by using Hyper-V isolation? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
| Name | Base image operating system |
| --- | --- |
| image1 | Windows Server 2022 |
| image2 | Windows Server 2019 |
| image3 | Windows Server 2016 |
| image4 | Linux |
Explanation
Process isolation: image1 only. A process-isolated container shares the host's kernel, so its base image must match the host's Windows build. On a Windows Server 2022 host, only Windows Server 2022 images support process isolation; Windows Server 2019 (image2) and Windows Server 2016 (image3) images are blocked from running process-isolated because the build numbers differ. A Linux image (image4) can never share the Windows kernel.
Hyper-V isolation: image1, image2, image3, and image4. Hyper-V isolation runs each container in its own lightweight utility VM with its own kernel, so the image does not have to match the host build. The compatibility matrix for a Windows Server 2022 host lists Hyper-V isolation as supported for Windows Server 2022, 2019, and 2016 images. Linux containers on a Windows host always run inside a virtualized Linux kernel, so image4 also runs only with VM-based isolation. Running all four with Hyper-V isolation also maximizes isolation, as the question requires.
Your on-premises network contains an Active Directory Domain Services (AD DS) domain. The domain contains a server named Server1 that runs Windows Server.
You have an Azure subscription that is linked to a Microsoft Entra tenant.
You need to add an Azure network adapter to Server1.
Which type of credential should you provide for the adapter?
- A. FIDO2 key
- B. Active Directory user account
- C. Microsoft Entra user account Correct
- D. certificate
Explanation
A Microsoft Entra user account is required to authenticate to Azure and manage virtual networks. This type of credential has the necessary permissions within the Azure environment, unlike local AD DS accounts or certificates which do not provide the needed authority in Azure.
You have an Azure subscription. The subscription contains a virtual machine that has the following configurations:
• Name: VM1
• Size: Standard DS1 v2
• Operating system: Windows Server 2022 Datacenter: Azure Edition
VM1 contains an OS disk named Disk0 that has the following configurations:
• Size: 127 GB
• Type: Standard SSD
• Redundancy: Locally-redundant storage (LRS)
You perform the following actions:
• From the Azure portal, you add a new data disk named Disk1 to VM1.
• From VM1, you install an app named App1.
You need to ensure that Disk1 will be used as the D drive for VM1. The solution must ensure that data written by App1 to drive D will be retained when VM1 restarts.
What should you do first?
- A. Move Pagefile.sys to the C drive. Correct
- B. From Disk Management, change the drive letter assigned to the volume on Disk0.
- C. From Disk Management, change the drive letter assigned to the volume on Disk1.
- D. Resize VM1 to Standard DS2 v2.
Explanation
On a Standard DS1 v2 VM, drive D is the temporary disk. Its data is lost when the VM is resized, deallocated or moved to another host, and it holds pagefile.sys. To make the data disk Disk1 the D drive, follow Microsoft's procedure: first move pagefile.sys to the C drive and restart; then, in Disk Management, change the temporary disk's letter (for example to T) and assign D to the volume on Disk1; finally move the page file back to the temporary drive. You cannot change the drive letter of the D volume while the page file is on it, so changing Disk1's letter is not the first step, and it is the temporary disk's letter that must change, not Disk0's (C). Resizing the VM does not remove the temporary disk.
You have a Hyper-V host named Server1 that is connected to a managed switch. The switch is connected to multiple VLANs.
On Server1, you configure a new virtual machine named VM1.
You need to configure VM1 to communicate with all the VLANs. Any network traffic that is not tagged must be directed to VLAN 20.
How should you complete the PowerShell command? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Explanation
Select cmdlet for VM1 network adapter: Set-VMNetworkAdapterVlan is the Hyper-V cmdlet that sets the VLAN mode (access, trunk, isolated, community, promiscuous or untagged) on a virtual machine's network adapter, which is what controls how VM1 handles 802.1Q tags. Set-VMNetworkAdapter changes general adapter properties such as bandwidth, MAC address spoofing, DHCP guard or VMQ weight and has no VLAN mode parameters. Set-VMNetworkAdapterTeamMapping only maps a VM adapter to a specific physical member of a SET team.
Select VLAN configuration for VM1: -Trunk -NativeVlanId 20. Trunk mode passes tagged frames from multiple VLANs to the guest, so VM1 can communicate with all the VLANs on the managed switch. -NativeVlanId 20 makes VLAN 20 the native VLAN, so untagged traffic is placed on VLAN 20. (In a full command, trunk mode also takes -AllowedVlanIdList to list the allowed VLANs.) -Access -VlanId 20 would limit the adapter to a single VLAN. -Untagged removes VLAN tagging altogether. -VmqWeight is a Set-VMNetworkAdapter queue setting, not a VLAN mode.
You have an Azure subscription. The subscription contains a virtual machine named Server1 that runs Windows Server 2019 Standard and has the following configurations:
• Size: Standard_D2_v3
• vCPUs: 2
• RAM: 8 GB
• Temp storage: 50 GB
• Max data disks: 4
You need to resize Server1 to use a virtual machine that has the following configurations:
• Size: Standard_D4_v5
• vCPUs: 4
• RAM: 16 GB
• Temp storage: None
• Max data disks: 16
What should you do first?
- A. Reformat the OS disk as ReFS.
- B. Move Pagefile.sys to drive C. Correct
- C. Upgrade Server1 to Windows Server 2022 Datacenter: Azure Edition.
- D. Convert the data disks into GTP disks.
Explanation
Before resizing Server1 to a new size that does not include temporary storage, you should move the Pagefile.sys from the temporary drive (if it exists) to drive C. This ensures there is no dependency on the temp storage which will be removed in the new configuration.
You have an Azure subscription. The subscription contains a virtual network named VNet1. VNet1 contains two virtual machines named VM1 and VM2 that run Windows Server.
You need to ensure that when you sign in to the Azure portal from VM2, you can manage the operating system of VM1. The solution must minimize costs.
Which two settings should you configure for VM1? To answer, select the appropriate settings in the answer area.
NOTE: Each correct answer is worth one point.
Explanation
First setting to configure for VM1: Access control (IAM). Access to Windows Admin Center in the Azure portal is controlled by Azure RBAC. To connect, your account needs the Reader and Windows Admin Center Administrator Login roles on VM1, and installing the extension needs Owner or Contributor. You assign these roles on VM1's Access control (IAM) blade. Owner or Contributor on its own does not let you sign in to the VM through Windows Admin Center.
Second setting to configure for VM1: Windows Admin Center. To manage the operating system from the portal, the Windows Admin Center extension must be installed in VM1. You do this from VM1's Windows Admin Center blade by selecting Install, and afterwards you use Connect on the same blade. Because you sign in to the portal from VM2, which is in the same virtual network, you connect over VM1's private IP address. That needs no inbound port rule, so Network settings does not have to change. Windows Admin Center in the Azure portal costs nothing. Bastion is billed by the hour and does not work with Windows Admin Center in the portal, so it does not meet the minimize-costs requirement.
You have an Azure subscription. The subscription contains a virtual machine named VM1 that runs Windows Server and has the following disks:
• OS disk: Disk1
o Size: 512 GiB
o Free space: 260 GiB
o Encryption: SSE with PMK
o Storage type: Standard SSD
• Data disk: Disk2
o Size: 512 GiB
o Free space: 45 GiB
o Storage type: Standard HDD
o Encryption: Platform-managed key
You are planning a maintenance strategy for VM1.
You need to identify which task can be performed on Disk2 without causing downtime to VM1.
What should you do on Disk2?
- A. Increase the size. Correct
- B. Change the encryption type.
- C. Decrease the size.
- D. Change the storage type to Premium SSD.
Explanation
Increasing the size of Disk2 can be done without downtime. Azure supports "Expand without downtime" for managed data disks such as Disk2 (a 512 GiB Standard HDD, well under the 4 TiB limit for this feature), so you can raise the disk size while VM1 keeps running and then extend the volume in Windows. This feature applies only to data disks; expanding an OS disk still requires deallocating the VM.
The other options cause downtime: decreasing the size of a managed disk is not supported at all; changing the disk type (Standard HDD to Premium SSD) requires VM1 to be stopped (deallocated) first; and switching an attached disk from platform-managed keys to customer-managed keys requires the disk to be detached or the VM to be deallocated.
You have an Azure subscription named Sub1 that is linked to a Microsoft Entra tenant named contoso.com. Contoso.com contains the users shown in the following table.
You deploy a virtual machine that has the following configurations:
• Name: VM1
• Resource group: RG1
• Operating system: Windows Server
• Login with Microsoft Entra ID: Enabled
You have the Azure role assignments shown in the following table.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
| Name | Type |
| --- | --- |
| User1 | Member |
| User2 | Guest |
| User3 | Member |
| User | Role | Scope |
| --- | --- | --- |
| User1 | Virtual Machine Contributor | RG1 |
| User2 | Virtual Machine User Login | RG1 |
| User3 | Virtual Machine Administrator Login | Sub1 |
Explanation
Statement 1 (No): Signing in to a Windows VM with Microsoft Entra credentials requires the Virtual Machine Administrator Login or Virtual Machine User Login role. User1 has Virtual Machine Contributor, a management-plane role that lets User1 manage VM1 but does not grant sign-in rights.
Statement 2 (No): User2 has Virtual Machine User Login at RG1, which would normally allow sign-in, but User2 is a guest (B2B) account. Microsoft Entra sign-in to Windows VMs supports only standard user accounts from the same tenant as the VM; guest accounts cannot be used for authentication.
Statement 3 (Yes): User3 is a member account with Virtual Machine Administrator Login assigned at the Sub1 scope. Azure role assignments are inherited by child scopes, so the assignment applies to RG1 and VM1, and User3 can sign in with administrator privileges.
You have a Hyper-V host.
You are evaluating the available schedulers.
Which type of scheduler maximizes isolation between guests and the host?
- A. classic
- B. root
- C. core Correct
- D. classic with Simultaneous Multithreading (SMT) disabled
Explanation
The core scheduler maximizes isolation between guests and the host. It schedules a guest's virtual processors in groups onto the SMT sibling threads of the same physical core, so a physical core is never shared at the same time between two different VMs or between a VM and the root partition. This uses the VM's virtualization boundary as a security boundary and mitigates side-channel attacks between workloads. The classic scheduler (with or without SMT disabled) uses fair-share scheduling of virtual processors across any logical processor, so it does not provide this guest-to-host isolation. The root scheduler hands scheduling decisions to the root partition's OS scheduler and is not designed for isolation.
You have the servers shown in the following table.
| Name | Role |
|------|------|
| Server1 | Hyper-V |
| Server2 | Hyper-V |
| Server3 | DHCP Server |
Server1 contains a virtual machine named VM1 that runs Windows Server. Server1 has an external switch named Switch1. VM1 is connected to Switch1.
You provision containers on VM1.
You need to configure networking for VM1. The solution must meet the following requirements:
• Ensure that Server3 automatically assigns IP addresses to the containers.
• Ensure that the containers can communicate with Server2.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Explanation
On the network adapter for VM1, enable: MAC address spoofing — The containers inside VM1 each use their own MAC address. By default, the Hyper-V switch port on Server1 forwards only frames whose source MAC matches VM1's adapter, so container traffic would be dropped. Microsoft documents that the transparent network driver requires MAC address spoofing when the container host is a virtual machine. DHCP guard drops DHCP server messages sent from a VM, and Router guard drops router advertisement and redirect messages; neither lets the containers' traffic through.
On the container for VM1, set the network driver type to: Transparent — Containers on a transparent network connect directly to the physical network through an external Hyper-V switch, and their IP addresses come from the physical network either statically or dynamically from an external DHCP server. This lets Server3 assign their addresses and lets them reach Server2 directly. The l2bridge (Bridge) driver rewrites container traffic to the host's MAC address, and its IP addresses are allocated by the Host Networking Service from a provided subnet prefix, not by an external DHCP server. Overlay is for multi-host swarm or Kubernetes clusters, uses VXLAN encapsulation, and gets its addresses from swarm-managed prefixes.
You deploy a Windows Server container host.
You need to create a container image that will be based on the Nano Server base image and will contain a custom file.
Which four commands should you run in sequence? To answer, move the appropriate commands from the list of commands to the answer area and arrange them in the correct order.
Explanation
1. docker pull downloads the Nano Server base image (for example mcr.microsoft.com/windows/nanoserver:ltsc2022).
2. docker run -it starts a container from that image with an interactive session. Inside it you create the custom file (for example echo "Hello World!" > Hello.txt) and then exit.
3. docker commit <container-ID> <new-image-name> saves the changes made in the container as a new image that includes the custom file.
4. docker images lists the local images so you can confirm that the new image exists.
There is no docker add command (ADD is a Dockerfile instruction). docker build creates an image from a Dockerfile, which this procedure does not use.
You have an Azure subscription. The subscription contains multiple virtual machines that run Windows Server.
You need to create an Azure Machine Configuration package.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Explanation
1. Create a PS1 file: write the PowerShell Desired State Configuration (DSC) configuration, for example Configuration MyConfig { ... }, and save it as a script such as MyConfig.ps1.
2. Generate a MOF file: run the script to compile the configuration. This produces localhost.mof, which you usually rename to the package name, for example MyConfig.mof.
3. Generate a ZIP file: run New-GuestConfigurationPackage with the compiled MOF. It bundles the MOF, the required DSC resource modules and a metaconfig file into the package. The package must be a .zip file and can't exceed 100 MB uncompressed.
Machine configuration does not use YAML or CAB files.
You have an Azure subscription. The subscription contains a virtual machine named VM1 that runs Windows Server.
You plan to automate tasks on VM1 by using a runbook.
You need to recommend which languages can be used to develop the tasks in the runbook and the minimum interval that can be used when scheduling the tasks.
What should recommend? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Explanation
Languages: PowerShell and Python — Azure Automation runbooks can be authored only in the runbook types the service supports: PowerShell, PowerShell Workflow, graphical (which is itself PowerShell-based), and Python. Compiled languages such as C#, Java, or general .NET assemblies are not runbook types, so the options that include C#, Java, or .NET are not valid choices for developing the tasks.
Interval: 1 hour — an Azure Automation recurring schedule has a minimum supported frequency of one hour, so the shortest interval you can configure when linking a schedule to the runbook is hourly. Shorter values such as 1, 5, or 15 minutes cannot be set on an Automation schedule; achieving sub-hour execution would require an external trigger (for example a Logic App or a webhook call) rather than the built-in scheduler.
You have a Docker host.
You need to create a Windows Server container image that will include an installation of Python.
How should you complete the Dockerfile? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Dockerfile:
[Selection 1: parser directive]
FROM mcr.microsoft.com/windows/servercore:ltsc2025
RUN powershell.exe -Command wget https://www.python.org/ftp/python/3.10.16/python-3.10.16.exe; [Selection 2]
Start-Process c:\python-3.10.16.exe -ArgumentList '/quiet InstallAllUsers=1 PrependPath=1' -Wait
Explanation
Parser directive line (before FROM): # escape=` — The escape parser directive changes the character Docker treats as the escape and line-continuation character, and it must appear at the very top of the Dockerfile, before FROM. Windows Dockerfiles commonly switch it to the backtick because the default escape character, the backslash, is also the Windows path separator, so paths such as c:\python-3.10.16.exe could otherwise be misread. # syntax= selects a BuildKit frontend and # check= configures build checks; neither changes the escape character.
Line-continuation character at the end of the first RUN line: ` — After the directive sets the escape character to the backtick, that character continues the RUN instruction onto the next line, so the download and the silent Start-Process install of python-3.10.16.exe run as one instruction. The backslash no longer has that role once the directive has reassigned it, and the forward slash has no line-continuation meaning in a Dockerfile.
Your network contains two VLANs for client computers and one VLAN for a datacenter. Each VLAN is assigned an IPv4 subnet. Currently, all the client computers use static IP addresses.
You plan to deploy a DHCP server to the VLAN in the datacenter.
You need to use the DHCP server to provide IP configurations to all the client computers.
What is the minimum number of scopes and DHCP relays you should create? To answer, select the appropriate option the answer area.
NOTE: Each correct selection is worth one point.
Hot Area:
Explanation
DHCP scopes: 3 — A DHCP scope is bound to a single IPv4 subnet, and the address range in a scope must match the subnet of the segment it serves, so one scope cannot be stretched across multiple VLANs. The environment has three IPv4 subnets (the two client VLANs plus the datacenter VLAN that hosts the DHCP server itself), so the server needs three scopes: one per subnet, with each scope carrying its own default gateway and other subnet-specific options. Choosing 2 would leave the datacenter subnet without a scope of its own.
DHCP relays: 2 — DHCP client traffic (DHCPDISCOVER/DHCPREQUEST) is broadcast-based and routers do not forward broadcasts, so clients on a VLAN other than the server's cannot reach the DHCP server directly. A DHCP relay agent (IP helper on the router/Layer 3 switch, or the Windows Server DHCP Relay Agent role service in Routing and Remote Access) is needed on each of the two client VLANs to convert those broadcasts into unicast traffic aimed at the DHCP server in the datacenter and relay the offers back. A third relay is unnecessary because the datacenter VLAN already contains the DHCP server, so no relaying is required there.
You have a server that runs Windows Server and has the DHCP Server role installed. The server has a scope named Scope1 that has the following configurations:
• Address range: 192.168.0.2 to 192.168.1.254
• Mask: 255.255.254.0
• Router: 192.168.0.1
• Lease duration: 3 days
• DNS server: 172.16.0.254
You have 50 Microsoft Teams Phone devices from the same vendor. All the devices have MAC addresses within the same range.
You need to ensure that all the Teams Phone devices that receive a lease from Scope1 have IP addresses in the range of 192.168.1.100 to 192.168.1.200. The solution must NOT affect other DHCP clients that receive IP configurations from Scope1.
What should you create?
- A. a scope
- B. a filter
- C. scope options
- D. a policy Correct
Explanation
A policy should be created to ensure that all Microsoft Teams Phone devices receive IP addresses within the specified range without affecting other DHCP clients. Policies in DHCP allow for specific configurations based on criteria such as MAC address ranges, which is suitable for this scenario.
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You are planning the deployment of DNS to a new network.
You have three internal DNS servers as shown in the following table.
| Name | Location | IP address | Local DNS zone |
|---|---|---|---|
| Server1 | Montreal | 10.0.1.10 | contoso.local |
| Server2 | Toronto | 10.0.2.10 | east.contoso.local |
| Server3 | Seattle | 10.0.3.10 | west.contoso.local |
The contoso.local zone contains zone delegations for east.contoso.local and west.contoso.local. All the DNS servers use root hints.
You need to ensure that all the DNS servers can resolve the names of all the internal namespaces and internet hosts.
Solution: You configure Server2 and Server3 to forward DNS requests to 10.0.1.10.
Does this meet the goal?
Explanation
Yes. A DNS server first answers from the zones it hosts and from its cache, and sends only the remaining queries to its forwarder. Server2 and Server3 still answer for their own zones and forward everything else to Server1 (10.0.1.10). Server1 hosts contoso.local, which contains delegations for east.contoso.local and west.contoso.local, so it resolves names in contoso.local directly and follows the delegations to Server2 and Server3 for the child zones. For internet names, Server1 uses root hints. As a result, Server2 resolves contoso.local and west.contoso.local through Server1, Server3 resolves contoso.local and east.contoso.local through Server1, and all three servers can resolve internet hosts.
You have an on-premises network that is connected to an Azure virtual network by using a Site-to-Site VPN. Each network contains a subnet that has the same IP address space. The on-premises subnet contains a virtual machine.
You plan to migrate the virtual machine to the Azure subnet.
You need to migrate the on-premises virtual machine to Azure without modifying the IP address. The solution must minimize administrative effort.
What should you implement before you perform the migration?
- A. Azure Extended Network Correct
- B. Azure Virtual Network NAT
- C. Azure Application Gateway
- D. Azure virtual network peering
Explanation
Azure Extended Network allows extending the on-premises network to Azure, enabling the virtual machine to retain its IP address during migration with minimal administrative effort.
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You are planning the deployment of DNS to a new network.
You have three internal DNS servers as shown in the following table.
| Name | Location | IP address | Local DNS zone |
|---|---|---|---|
| Server1 | Montreal | 10.0.1.10 | contoso.local |
| Server2 | Toronto | 10.0.2.10 | east.contoso.local |
| Server3 | Seattle | 10.0.3.10 | west.contoso.local |
The contoso.local zone contains zone delegations for east.contoso.local and west.contoso.local. All the DNS servers use root hints.
You need to ensure that all the DNS servers can resolve the names of all the internal namespaces and internet hosts.
Solution: On Server2 and Server3, you configure a conditional forwarder for contoso.local.
Does this meet the goal?
Explanation
Yes. Server1 hosts contoso.local, and that zone has delegations for east.contoso.local and west.contoso.local, so Server1 can resolve names in all three internal namespaces by following the delegations to Server2 and Server3. When Server2 and Server3 have a conditional forwarder for contoso.local that points to Server1, they send every query for contoso.local and its subdomains to Server1. A query from Server2 for a name in west.contoso.local matches the contoso.local forwarder, and Server1 resolves it through the west delegation. Each server answers queries for its own zone authoritatively, and all the servers resolve internet hosts through root hints. Conditional forwarders from a child zone to its parent, combined with delegations from the parent to the children, is a supported design, so every DNS server can resolve all the internal namespaces and internet hosts.
You have servers that have the DNS Server role installed. The servers are configured as shown in the following table.
| Name | Office | Local DNS zone | IP address |
|---|---|---|---|
| Server1 | Paris | contoso.com | 10.1.1.1 |
| Server2 | New York | None | 10.2.2.2 |
All the client computers in the New York office use Server2 as the DNS server.
You need to configure name resolution in the New York office to meet the following requirements:
✑ Ensure that the client computers in New York can resolve names from contoso.com.
✑ Ensure that Server2 forwards all DNS queries for internet hosts to 131. 107.100.200.
The solution must NOT require modifications to Server1.
Which two components should you configure on Server2? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
- A. a forwarder Correct
- B. a conditional forwarder Correct
- C. a delegation
- D. a secondary zone
- E. a reverse lookup zone
Explanation
Option A is correct because configuring a forwarder on Server2 allows it to forward all DNS queries for internet hosts to the specified IP address (131.107.100.200). Option B is also correct as setting up a conditional forwarder specifically for the contoso.com zone ensures that client computers in New York can resolve names from this domain by forwarding those requests to Server1, which hosts the contoso.com zone.
You have an Azure virtual machine named VM1 that runs Windows Server.
You need to configure the management of VM1 to meet the following requirements:
✑ Require administrators to request access to VM1 before establishing a Remote Desktop connection.
✑ Limit access to VM1 from specific source IP addresses.
✑ Limit access to VM1 to a specific management port.
What should you configure?
- A. a network security group (NSG)
- B. Azure Active Directory (Azure AD) Privileged Identity Management (PIM)
- C. Microsoft Defender for Cloud Correct
- D. Azure Front Door
Explanation
Microsoft Defender for Cloud's Just-in-Time (JIT) VM access feature meets all the requirements: it requires administrators to request access, limits access from specific IP addresses, and restricts access to a specific management port.
Your network contains an Active Directory Domain Services (AD DS) domain named contoso.com. The domain contains a DNS server named Server1. Server1 hosts a DNS zone named fabrikam.com that was signed by DNSSEC.
You need to ensure that all the member servers in the domain perform DNSSEC validation for the fabrikam.com namespace.
What should you do?
- A. On Server1, run the Add-DnsServerTrustAnchor cmdlet.
- B. On each member server, run the Add-DnsServerTrustAnchor cmdlet.
- C. From a Group Policy Object (GPO), add a rule to the Name Resolution Policy Table (NRPT). Correct
- D. From a Group Policy Object (GPO), modify the Network List Manager policies.
Explanation
To ensure all member servers in the domain perform DNSSEC validation for the fabrikam.com namespace, you should configure a rule in the Name Resolution Policy Table (NRPT) via a Group Policy Object (GPO). This method allows centralized management and application of DNSSEC validation settings to multiple machines.
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You are planning the deployment of DNS to a new network.
You have three internal DNS servers as shown in the following table.
| Name | Location | IP address | Local DNS zone |
|---|---|---|---|
| Server1 | Montreal | 10.0.1.10 | contoso.local |
| Server2 | Toronto | 10.0.2.10 | east.contoso.local |
| Server3 | Seattle | 10.0.3.10 | west.contoso.local |
The contoso.local zone contains zone delegations for east.contoso.local and west.contoso.local. All the DNS servers use root hints.
You need to ensure that all the DNS servers can resolve the names of all the internal namespaces and internet hosts.
Solution: On Server2, you create a conditional forwarder for contoso.local and west.contoso.local. On Server3, you create a conditional forwarder for contoso.local and east.contoso.local.
Does this meet the goal?
Explanation
Yes. Server1 hosts contoso.local, which contains delegations for east.contoso.local and west.contoso.local, so Server1 can resolve all three internal namespaces by following the delegations. Server2 and Server3 host only their own child zones and would otherwise send queries for the other internal zones to the internet root servers, which cannot resolve .local names. The conditional forwarders on Server2 (for contoso.local and west.contoso.local) and on Server3 (for contoso.local and east.contoso.local) send those queries to the servers that can answer them. Because all three servers use root hints, they can also resolve internet host names. Therefore every server can resolve all internal namespaces and internet hosts.
Your network contains an Active Directory Domain Services (AD DS) domain. The domain contains 10 servers that run Windows Server. The servers have static
IP addresses.
You plan to use DHCP to assign IP addresses to the servers.
You need to ensure that each server always receives the same IP address.
Which type of identifier should you use to create a DHCP reservation for each server?
- A. NetBIOS name
- B. MAC address Correct
- C. fully qualified domain name (FQDN)
- D. universally unique identifier (UUID)
Explanation
The MAC address is used to create a DHCP reservation for each server because it uniquely identifies the network interface of the server. This ensures that each server always receives the same IP address from the DHCP server.
Your network contains an Active Directory Domain Services (AD DS) domain named contoso.com. The domain contains the VPN servers shown in the following table.
| Name | IP address |
|------|------------|
| VPN1 | 172.16.0.254 |
| VPN2 | 131.10.15.254 |
| VPN3 | 10.10.0.254 |
You have a server named NPS1 that has Network Policy Server (NPS) installed. NPS1 has the RADIUS clients shown in the following exhibit.
VPN1, VPN2, and VPN3 use NPS1 for RADIUS authentication. All the users in contoso.com are allowed to establish VPN connections.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Explanation
Statement 1 (No): NPSclient1 has the address of VPN1 (172.16.0.254) but Enabled is False. NPS ignores requests from a disabled RADIUS client, so authentication through VPN1 fails.
Statement 2 (Yes): NPSclient2 matches VPN2's address (131.10.15.254), is enabled, and uses the shared secret, so NPS1 processes VPN2's requests and users can authenticate.
Statement 3 (No): NPSclient3 is enabled but its address is 172.16.1.254, not VPN3's 10.10.0.254. No RADIUS client is defined for VPN3, so NPS1 discards its requests.
You have an on-premises Active Directory Domain Services (AD DS) domain that syncs with an Azure Active Directory (Azure AD) tenant. The on-premises network is connected to Azure by using a Site-to-Site VPN.
You have the DNS zones shown in the following table.
| Name | Location | Description |
|---|---|---|
| contoso.com | A domain controller named DC1 on the on-premises network | Provide name resolution on-premises |
| fabrikam.com | An Azure private DNS zone | Provides name resolution for all Azure virtual networks |
You need to ensure that names from fabrikam.com can be resolved from the on-premises network.
Which two actions should you perform? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
- A. Create a stub zone for fabrikam.com on DC1.
- B. Create a conditional forwarder for fabrikam.com on DC1. Correct
- C. Create a secondary zone for fabrikam.com on DC1.
- D. Deploy an Azure virtual machine that runs Windows Server. Modify the DNS Servers settings for the virtual network.
- E. Deploy an Azure virtual machine that runs Windows Server. Configure the virtual machine as a DNS forwarder. Correct
Explanation
An Azure private DNS zone can be resolved only from inside a linked Azure virtual network, through the Azure-provided DNS address 168.63.129.16, which on-premises clients cannot reach. Deploy a Windows Server VM in Azure and configure it as a DNS forwarder that sends queries to Azure DNS. Then create a conditional forwarder for fabrikam.com on DC1 that points to that VM's private IP address over the Site-to-Site VPN. A stub zone or a secondary zone would need zone transfers, which a private DNS zone does not support. Changing the virtual network's DNS servers affects only Azure resources, not on-premises resolution.
You have an on-premises server named Server1 that runs Windows Server.
You have an Azure virtual network that contains an Azure virtual network gateway.
You need to connect only Server1 to the Azure virtual network.
What should you use?
- A. a Site-to-Site VPN
- B. Azure Network Adapter Correct
- C. an ExpressRoute circuit
- D. Azure Extended Network
Explanation
Azure Network Adapter enables a direct network connection from an on-premises server to an Azure virtual network without setting up a full Site-to-Site VPN, making it suitable for connecting a single server like Server1.
Your network contains an Active Directory Domain Services (AD DS) forest. The forest contains three domains. Each domain contains 10 domain controllers.
You plan to store a DNS zone in a custom Active Directory partition.
You need to create the Active Directory partition for the zone. The partition must replicate to only four of the domain controllers.
What should you use?
- A. Active Directory Administrative Center
- B. Set-DnsServer
- C. New-ADObject
- D. ntdsutil.exe Correct
Explanation
ntdsutil.exe is the correct tool for creating a custom Active Directory partition. This utility provides commands to manage and manipulate AD DS partitions, including specifying which domain controllers should replicate the new partition.
Your network contains an Active Directory Domain Services (AD DS) domain. The domain contains 10 servers that run Windows Server. The servers have static IPv4 addresses.
You plan to use DHCP to assign IPv4 addresses to the servers.
You need to ensure that each server always receives the same IPv4 address.
Which type of identifier should you use to create a DHCP reservation for each server?
- A. fully qualified domain name (FQDN)
- B. universally unique identifier (UUID)
- C. NetBIOS name
- D. MAC address Correct
Explanation
DHCP reservations are created using the MAC address of a network interface to ensure that a specific IPv4 address is always assigned to that device. Using the MAC address guarantees consistent IP assignment regardless of changes in domain names or other identifiers.
You have an on-premises server named Server1 that runs Windows Server.
You have an Azure subscription that contains a virtual network named VNet1.
You need to connect Server1 to VNet1 by using Azure Network Adapter.
What should you use?
- A. the Azure portal
- B. Azure AD Connect
- C. Device Manager
- D. Windows Admin Center Correct
Explanation
Windows Admin Center is the correct tool for connecting an on-premises server to an Azure virtual network using Azure Network Adapter. This functionality allows for seamless integration of on-premises servers into Azure's networking environment.
Your network contains an Active Directory domain, a web app named App1, and a perimeter network. The perimeter network contains a server named Server1 that runs Windows Server.
You plan to provide external access to App1.
You need to implement the Web Application Proxy role service on Server1.
Which role should you add to Server1, and which role should you add to the network? To answer, drag the appropriate roles to the correct targets. Each role may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
Explanation
To implement Web Application Proxy, the Remote Access role with the Web Application Proxy role service must be installed on Server1. Additionally, Active Directory Federation Services (AD FS) should be configured in the network to enable secure access to App1.
Your network contains an Active Directory Domain Services (AD DS) domain. The domain contains a user named User1 and the servers shown in the following table.
| Name | Server role | DHCP scope |
|---|---|---|
| Server1 | DHCP Server | Scope1, Scope2 |
| Server2 | DHCP Server | Scope3, Scope4 |
You need to ensure that User1 can manage only Scope1 and Scope3.
What should you do?
- A. Add User1 to the DHCP Administrators group on Server1 and Server2.
- B. Implement IP Address Management (IPAM). Correct
- C. Add User1 to the DHCP Administrators domain local group.
- D. Implement Windows Admin Center and add connections to Server1 and Server2.
Explanation
IP Address Management (IPAM) role-based access control lets you delegate DHCP administration below the server level. You assign User1 the IPAM DHCP Scope Administrator role through an access policy, with an access scope that contains only Scope1 and Scope3, so User1 can manage those two scopes and nothing else. Adding User1 to the DHCP Administrators group on Server1 and Server2, or to a domain DHCP Administrators group, gives full control of every scope on the servers, including Scope2 and Scope4. Windows Admin Center connects with the user's own server permissions and has no scope-level delegation.
Your network contains an Active Directory Domain Services (AD DS) forest. The forest contains three domains. Each domain contains 10 domain controllers.
You plan to store a DNS zone in a custom Active Directory partition.
You need to create the Active Directory partition for the zone. The partition must replicate to only four of the domain controllers.
What should you use?
- A. dnscmd.exe Correct
- B. Active Directory Sites and Services
- C. Set-DnsServer
- D. New-ADObject
Explanation
A custom DNS application directory partition is created with dnscmd. Run dnscmd /CreateDirectoryPartition <partitionFQDN> to create the partition, then run dnscmd <server> /EnlistDirectoryPartition <partitionFQDN> on each of the four domain controllers that must hold a replica. The partition replicates only to the DCs enlisted in its replica set, and the zone can then be stored in it. Active Directory Sites and Services manages sites, site links and connection objects, not application partitions. Set-DnsServer applies a whole DNS server configuration object and does not create a directory partition (the DNS PowerShell cmdlet for that is Add-DnsServerDirectoryPartition, which is not offered). New-ADObject is the generic cmdlet for creating directory objects and is not the supported way to create and enlist a DNS application partition.
You have servers that run Windows Server 2022 as shown in the following table.
| Name | Location | Description |
|---|---|---|
| Server1 | On-premises | Hosts a Microsoft SQL Server 2019 instance |
| Server2 | Azure | Contains the .NET SDK |
Server2 contains a .NET app named App1.
You need to establish a WebSocket connection from App1 to the SQL Server instance on Server1. The solution must meet the following requirements:
• Minimize the number of network ports that must be open on the on-premises network firewall.
• Minimize administrative effort.
What should you create first?
- A. an Azure Relay namespace Correct
- B. an Azure VPN gateway
- C. a WFC relay connection
- D. a hybrid connection
Explanation
Azure Relay Namespace is the correct choice because it enables secure communication between on-premises and cloud services using Hybrid Connections, which support WebSocket connections. This minimizes network port openings and administrative effort by leveraging Azure's managed service.
You have an on-premises server named Server1 that runs Windows Server. Server1 contains an app named App1 and a firewall named Firewall1.
You have an Azure subscription.
Internal users connect to App1 by using WebSockets.
You need to make App1 available to users on the internet. The solution must minimize the number of inbound ports open on Firewall1.
What should you include in the solution?
- A. Microsoft Application Request Routing (ARR) Version 2
- B. Azure Application Gateway
- C. Azure Relay Correct
- D. Web Application Proxy
Explanation
Azure Relay enables secure exposure of services running in a corporate network to the public cloud without opening ports on the firewall or making changes to the network infrastructure, which aligns with the requirement to minimize open inbound ports.
Your network contains an Active Directory Domain Services (AD DS) domain. The domain contains the offices shown in the following table.
| Location | Number of VPN servers | Number of remote users |
|---|---|---|
| Boston | 2 | 30 |
| Dallas | 2 | 50 |
| Seattle | 4 | 100 |
You need to deploy a Network Policy Server (NPS) named NPS1 to enforce network access policies for all remote connections.
What is the minimum number of RADIUS clients that you should add to NPS1?
- A. 1
- B. 3
- C. 8 Correct
- D. 180
- E. 188
Explanation
Each VPN server acts as a RADIUS client to the NPS server for enforcing network access policies. With a total of 8 VPN servers across all locations, you need to add 8 RADIUS clients to NPS1.
Your network contains a DHCP server.
You plan to add a new subnet and deploy Windows Server to the subnet.
You need to use the server as a DHCP relay agent.
Which role should you install on the server?
- A. Network Policy and Access Services
- B. Remote Access Correct
- C. Network Controller
- D. DHCP Server
Explanation
The Remote Access role includes the DHCP relay agent feature. Installing this role on a Windows Server allows it to forward DHCP requests from clients in other subnets to the actual DHCP server, which is essential for managing IP address distribution across multiple subnets.
You have an Azure virtual machine named VM1 that runs Windows Server.
You need to ensure that administrators request access to VM1 before establishing a Remote Desktop connection.
What should you configure?
- A. Azure Front Door
- B. Microsoft Defender for Cloud Correct
- C. Azure AD Privileged Identity Management (PIM)
- D. a network security group (NSG)
Explanation
Just-in-time (JIT) VM access in Microsoft Defender for Cloud (Defender for Servers Plan 2) locks down inbound management ports such as RDP 3389 with deny rules in the VM's network security group. An administrator must request access to VM1. Defender for Cloud checks the user's Azure RBAC permissions and, if the request is approved, opens the port for the requester's IP address for a limited time, then restores the rules. Azure AD Privileged Identity Management controls activation of role assignments, not network access to the VM. An NSG on its own has no request workflow. Azure Front Door is a global HTTP load balancer and does not handle RDP.
You have a server named Server1 that runs Windows Server. Server1 has a single network interface and the Hyper-V virtual switches shown in the following exhibit.
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.
Explanation
On Server1, you can create additional private and internal virtual switches only. An external virtual switch must bind to a physical network adapter, and Server1's only network interface is already bound to the external switch VSwitch3, so no further external switch can be created. Internal and private switches do not use a physical adapter, so more of either type can be created. Each new internal switch simply adds another virtual network adapter to the management operating system.
Server1 can access network shares on virtual machines that are connected to VSwitch2 or VSwitch3 only. VSwitch2 is an internal switch, which provides networking between the host and its virtual machines. VSwitch3 is an external switch shared with the management operating system, so the host and the VMs on it are on the same network. VSwitch1 is a private switch, which connects virtual machines only to each other and gives no connectivity to the host, so Server1 cannot reach shares on VMs that use only VSwitch1.
Your network contains an Active Directory Domain Services (AD DS) forest. The forest contains the servers shown in the following table.
| Name | In domain | Description |
|---|---|---|
| Server1 | contoso.com | Domain controller, DNS server |
| Server2 | contoso.com | Domain controller, DNS server |
| Server3 | contoso.com | DNS server |
| Server4 | east.contoso.com | Domain controller, DNS server |
| Server5 | east.contoso.com | DNS server |
On Server1, you create a DNS zone named Zone1.com as shown in the following exhibit.
To which DNS servers is Zone1.com replicated?
- A. Server2 only Correct
- B. Server2 and Server3 only
- C. Server2 and Server4 only
- D. Server2, Server3, and Server4 only
- E. Server2, Server3, Server4, and Server5
Explanation
Zone1.com is an Active Directory-integrated zone, and its replication scope is set to All DNS servers in this domain. Its data is stored in the DomainDnsZones application directory partition of contoso.com, and that partition replicates only to domain controllers in contoso.com that run the DNS Server role. Server2 is the only other domain controller in contoso.com that runs DNS, so the zone replicates only to Server2. Server3 is a DNS server in contoso.com but not a domain controller, so it holds no copy of the Active Directory database and cannot host an AD-integrated zone. Server4 and Server5 are in east.contoso.com, outside the selected domain scope. Only the All DNS servers in this forest scope would include Server4, and even then Server5 would be left out because it is not a domain controller.
Your network contains the segments shown in the following table.
You have servers that run Windows Server and are configured as shown in the following table.
You deploy a server named Server4 that runs Windows Server and has a static IP address of 172.16.1.1. You connect Server4 to Segment1.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point,
| Name | IPv4 address space | Gateway |
| --- | --- | --- |
| Segment1 | 172.16.1.0/24 | 172.16.1.1 |
| Segment2 | 172.16.2.0/24 | 172.16.2.1 |
| Name | IPv4 address | Connected to | Windows Defender Firewall configuration |
| --- | --- | --- | --- |
| Server1 | 172.16.1.10 | Segment1 | Allow ICMP traffic |
| Server2 | 172.16.2.2 | Segment1 | Allow ICMP traffic |
| Server3 | 172.16.2.20 | Segment2 | Allow ICMP traffic |
Explanation
Statement 1 (No): Server2 has the address 172.16.2.2, which belongs to Segment2's address space, but it is connected to Segment1. Server1 (172.16.1.10) sees 172.16.2.2 as a remote subnet and sends traffic for it to the gateway 172.16.1.1. The router forwards it to Segment2, where Server2 is not connected. Server2's replies to 172.16.1.10 would also have to go through its gateway 172.16.2.1, which it cannot reach from Segment1. Communication fails, so the ping by name fails too.
Statement 2 (No): With the address 172.16.2.2/24, Server2 treats Server3 (172.16.2.20) as being on its own link and sends an ARP request for it directly on Segment1. Server3 is on Segment2, a different broadcast domain, so the ARP request is never answered and the ping fails.
Statement 3 (Yes): Server4's static address 172.16.1.1 is already used by the Segment1 gateway. When the address is bound, Windows duplicate address detection finds the conflict, marks the static address as (Duplicate) and assigns an Automatic Private IP Addressing (APIPA) address. ipconfig /all then lists an Autoconfiguration IPv4 address from 169.254.0.0/16.
Your network contains an Active Directory Domain Services (AD DS) forest. The forest contains the sites and site links shown in the following exhibit.
The sites contain the bridgehead domain controllers shown in the following table.
| Name | Site |
|------|------|
| DC1 | Site1 |
| DC2 | Site2 |
| DC3 | Site3 |
| DC4 | Site4 |
The IP intersite transport container is configured as shown in the following exhibit.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
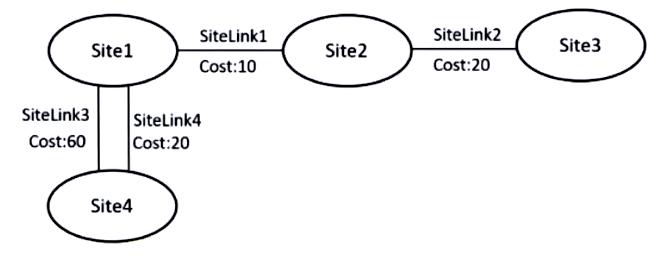
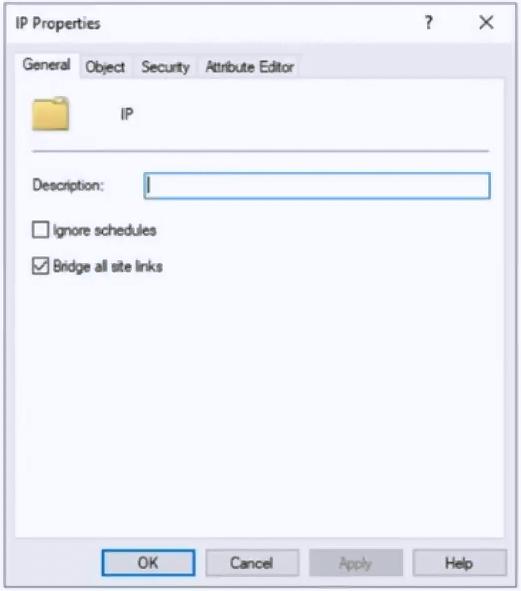
Explanation
Statement 1 (Yes): No site link connects Site1 and Site3 directly; Site1 reaches Site3 through SiteLink1 and SiteLink2. However, Bridge all site links is selected on the IP intersite transport, so all site links are transitive. The Intersite Topology Generator can therefore create a connection object directly between the bridgeheads DC1 and DC3, with a path cost of 10 + 20 = 30, and DC1 replicates directly with DC3 over the routed IP network.
Statement 2 (No): Active Directory does not load balance intersite replication across parallel site links. The KCC uses the least-cost path, so replication between Site1 and Site4 uses SiteLink4 (cost 20). SiteLink3 (cost 60) is used only if SiteLink4 becomes unavailable.
Statement 3 (Yes): Because Bridge all site links is enabled, the ISTG can build a direct connection between DC4 in Site4 and DC2 in Site2 (SiteLink4 + SiteLink1), so the changes do not pass through DC1. To make replication store-and-forward through DC1 in Site1, you must clear Bridge all site links on the IP intersite transport container. Site links then become nontransitive, and Site4 can replicate only with Site1, which in turn replicates with Site2.
You have a server named Server1 that runs Windows Server and has the Active Directory Federation Services role installed.
You plan to deploy Web Application Proxy to a server named Server2.
You export the Active Directory Federation Services (AD FS) certificate from Server1.
Which actions should you perform on Server2 in sequence? To answer, drag the appropriate actions to the correct order. Each action may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
Explanation
Web Application Proxy is a role service of the Remote Access server role, so first install the Remote Access role (with the Web Application Proxy role service) on Server2. Next import the AD FS certificate exported from Server1 into the local computer certificate store on Server2, because the proxy has to present the same federation service certificate. Finally run the Web Application Proxy Configuration Wizard, which connects Server2 to the AD FS farm and selects that certificate. Server2 is a proxy, not a federation server, so it does not need the Active Directory Federation Services role, and Application Request Routing for IIS is a separate reverse-proxy product that Web Application Proxy does not use.
Your network contains an Active Directory Domain Services (AD DS) domain. The domain contains the servers shown in the following table.
| Name | Operating system |
|---|---|
| Server1 | Windows Server 2016 |
| Server2 | Windows Server 2016 |
| Server3 | Windows Server 2019 |
| Server4 | Windows Server 2022 |
| Server5 | Windows Server 2022 |
You need to deploy inbound firewall rules to the servers. The solution must minimize administrative effort.
What should you use?
- A. PowerShell Desired State Configuration (DSC)
- B. local security objects
- C. Group Policy Objects (GPOs) Correct
- D. Microsoft Intune configuration profiles
Explanation
Group Policy Objects (GPOs) enable centralized management of configurations across multiple servers in an AD DS domain. This method minimizes administrative effort by allowing the deployment and enforcement of inbound firewall rules from a single point.
You have a server that runs Windows Server.
You need to prevent the creation of SMB Direct connections.
Which cmdlet should you run?
- A. Disable-WindowsOptionalFeature Correct
- B. Remove-WindowsFeature
- C. Set-NetAdapterAdvancedProperty
- D. Disable-NetAdapterBinding
Explanation
SMB Direct is an optional Windows feature named SMBDirect, and Microsoft documents disabling it with Disable-WindowsOptionalFeature -Online -FeatureName SMBDirect (and re-enabling it with Enable-WindowsOptionalFeature). Once the feature is disabled, SMB cannot create SMB Direct (RDMA) connections. Remove-WindowsFeature removes server roles and features installed through Server Manager, not the SMBDirect optional component. Set-NetAdapterAdvancedProperty changes driver-level adapter properties, and Disable-NetAdapterBinding unbinds protocols such as IPv6 or File and Printer Sharing from an adapter; neither is the documented way to stop SMB Direct.
You have an on-premises server named DNS1 that runs Windows Server and has the DNS Server role.
You have an Azure subscription that contains an Azure Private DNS zone named contoso.com.
You implement an Azure DNS Private Resolver named Resolver1.
You need to ensure that DNS1 can resolve names from contoso.com by using Resolver1. The solution must minimize administrative effort.
What should you configure?
- A. DNS policy Correct
- B. a Site-to-Site (S2S) VPN connection
- C. root hints
- D. a secondary DNS zone
Explanation
On-premises DNS servers resolve names in an Azure Private DNS zone by forwarding those queries to the inbound endpoint of the Azure DNS Private Resolver. On DNS1, a DNS policy can do this per domain: create a recursion scope whose forwarder is Resolver1's inbound endpoint IP address, then add a query resolution policy that applies that recursion scope to queries matching *.contoso.com. A secondary DNS zone would need a zone transfer from the Azure Private DNS zone, which Azure Private DNS does not support. Root hints point to the public internet root servers and cannot reach a private zone. A Site-to-Site VPN only provides network connectivity; it does not make DNS1 send contoso.com queries to Resolver1.
You have an on-premises server that runs Windows Server and contains the folders shown in the following table.
| Name | Drive | Volume file system |
|---|---|---|
| Folder1 | C | NTFS |
| Folder2 | D | NTFS |
| Folder3 | E | ReFS |
You have an Azure subscription.
You plan to implement Azure File Sync.
Which folders can be added as Azure File Sync server endpoints?
- A. Folder1 and Folder2 only Correct
- B. Folder1, Folder2, and Folder3
- C. Folder1 only
- D. Folder2 and Folder3 only
- E. Folder3 only
- F. Folder2 only
Explanation
Azure File Sync supports only NTFS file systems for server endpoints. Folder1 and Folder2 are on NTFS volumes, while Folder3 is on a ReFS volume which is not supported by Azure File Sync.
Your network contains an Active Directory Domain Services (AD DS) forest named contoso.com. The forest contains the servers shown in the following table.
Server1 hosts the DNS zone for contoso.com. The General tab of the contoso.com properties is configured as shown in the following exhibit.
Server3 hosts the DNS zone for east.contoso.com and is configured as shown in the following exhibit.
For each of the following statements, select Yes if the statement is true. Otherwise. select No.
NOTE: Each correct selection is worth one point.
| Name | In domain | Type |
| --- | --- | --- |
| Server1 | contoso.com | Domain controller, DNS server |
| Server2 | contoso.com | DNS server |
| Server3 | east.contoso.com | Domain controller, DNS server |
| Server4 | east.contoso.com | DNS server |
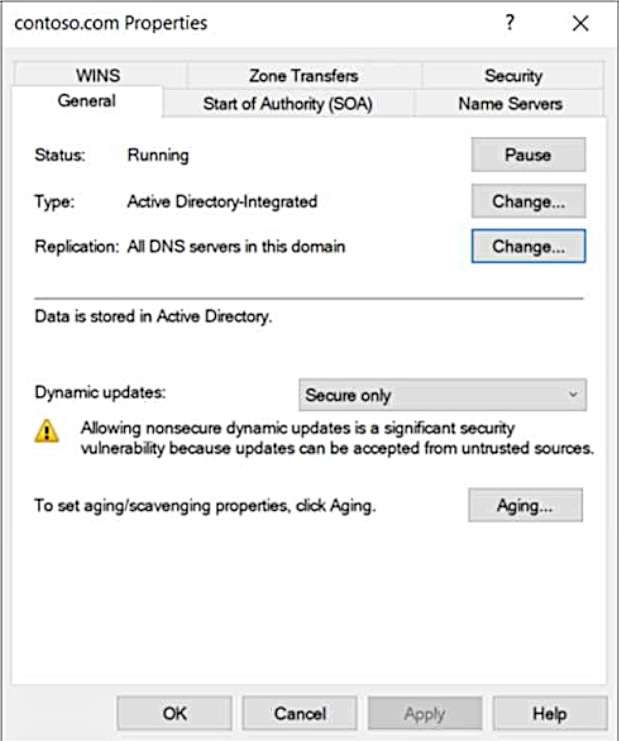
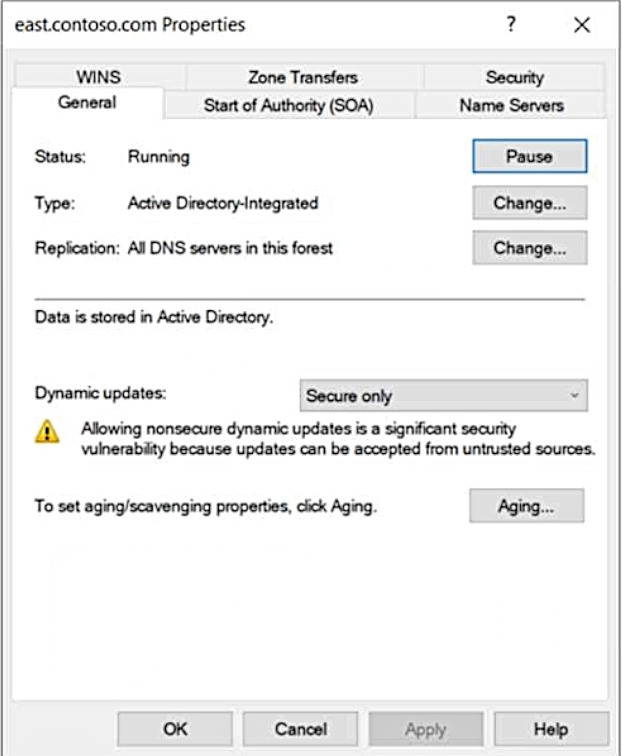
Explanation
Statement 1 (Yes): A secondary zone is a read-only, file-based copy loaded through zone transfer. It can be created on any DNS server, including a domain controller in another domain such as Server3. Server3 does not already hold contoso.com, because that zone replicates only within the contoso.com domain, so nothing conflicts.
Statement 2 (No): contoso.com is Active Directory-integrated with the scope 'All DNS servers in this domain'. Active Directory-integrated zones are stored in the directory and replicate only to DNS servers that are also domain controllers. Server2 is a DNS server but not a domain controller, so it does not receive the record.
Statement 3 (Yes): east.contoso.com is Active Directory-integrated with the scope 'All DNS servers in this forest' (the ForestDnsZones partition). It replicates to every DNS server that is a domain controller anywhere in the forest. Server1 is a domain controller and DNS server in contoso.com, so it receives the record.
You have an on-premises server named Server1 that runs Windows Server and is managed by using Windows Admin Center.
You have an Azure subscription that contains a virtual network named VNet1.
You need to connect Server1 to VNet1 by using an Azure Network Adapter.
What should you do first in Windows Admin Center?
- A. Select Roles & features and install the DirectAccess and VPN (RAS) role service.
- B. Select Register and register Windows Admin Center with Azure. Correct
- C. Select Extensions and install the Azure Cloud Shell extension.
- D. Select Internet Access and modify the Internet Access settings.
Explanation
Azure Network Adapter uses a point-to-site VPN that Windows Admin Center configures for you, creating the virtual network gateway in Azure if needed. Its requirements are an Azure subscription, an existing virtual network, internet access for the server, and a Windows Admin Center connection to Azure. So the first step is to register Windows Admin Center with Azure. After that, open Server1, select Networks and then Add Azure Network Adapter. The Azure Cloud Shell extension is not required. Installing the RAS role service or changing internet access settings is not a prerequisite, because Windows Admin Center configures the VPN client itself.
You have an on-premises server named Server1 that runs Windows Server.
You have an Azure subscription. The subscription contains a virtual machine named VM1 that runs Windows Server. The subscription contains a network security group (NSG) named NSG1 that has the following custom rules.
| Name | Priority | Port | Protocol | Source | Destination | Action | Direction |
| --- | --- | --- | --- | --- | --- | --- | --- |
| Rule1 | 100 | 443 | TCP | VirtualNetwork | Internet | Block | Outbound |
| Rule2 | 200 | Any | Any | Internet | VirtualNetwork | Block | Inbound |
The network interface of VM1 is associated with NSG1.
You plan to manage VM1 from Server1 by using Windows Admin Center from the Azure portal.
You need to ensure that you can install Windows Admin Center on VM1 by using the Azure portal. The solution must minimize administrative effort.
What should you do?
- A. Modify the priority of Rule2 and add an outbound port rule.
- B. Modify the priority of Rule1 and add an inbound port rule.
- C. Modify the priority of Rule2 and add an inbound port rule.
- D. Modify the priority of Rule1 and add an outbound port rule. Correct
Explanation
To install Windows Admin Center from the Azure portal, the VM must reach the Windows Admin Center service over HTTPS. The requirement is outbound internet access or an outbound port rule that allows TCP 443 to the WindowsAdminCenter and AzureActiveDirectory service tags. Rule1 blocks outbound TCP 443 from VirtualNetwork to Internet at priority 100, the highest custom priority, and the outbound rule the portal creates also uses priority 100. You therefore change Rule1 to a lower priority (a higher number) and add an outbound allow rule for 443 that is processed before it. Rule2 only blocks inbound traffic from the Internet. An inbound rule is needed only to connect to Windows Admin Center through a public IP address, not to install it, so changing Rule2 or adding an inbound rule does not fix the installation.
You have on-premises Windows devices.
You have an Azure subscription that contains a virtual network named VNet1.
You need to create a Site-to-Site (S2S) VPN between the on-premises network and VNet1.
Which three resources should you create? Each correct answer present part of the solution.
NOTE: Each correct selection is worth one point.
- A. a network security group (NSG)
- B. an Azure NAT gateway
- C. an Azure Route Server
- D. a VPN connection Correct
- E. a virtual network gateway Correct
- F. a local network gateway Correct
Explanation
To establish a Site-to-Site (S2S) VPN between on-premises Windows devices and VNet1 in Azure, you need to create a virtual network gateway (E), a local network gateway (F), and configure the actual VPN connection (D). These components are essential for setting up the secure tunnel required for S2S connectivity.
You have an on-premises datacenter named DC1.
You have an Azure subscription that contains the resources shown in the following table.
| Name | Type | Description |
|---|---|---|
| VNet1 | Virtual network | None |
| contoso.com | Azure Private DNS zone | Linked to VNet1 |
| Server1 | Virtual machine | • Runs Windows Server<br>• Connects to VNet1<br>• Has the DNS Server role installed<br>• Resolves names for contoso.com by using a conditional forwarder. |
| ER1 | ExpressRoute circuit | Connects DC1 and VNet1 |
You plan to perform the following actions:
• Provision an Azure DNS Private Resolver named PR1 on VNet1.
• Migrate Server1 to the on-premises datacenter.
You need to ensure that once Server1 is migrated to the datacenter, the server can resolve names for entries created in contoso.com.
What should you do?
- A. On Server1, create a secondary zone.
- B. On PR1, create an outbound endpoint.
- C. Create a DNS forwarding ruleset and associate the ruleset with PR1.
- D. On Server1, modify the conditional forwarder for contoso.com. Correct
Explanation
While Server1 runs in VNet1, its conditional forwarder for contoso.com can send queries to Azure-provided DNS (168.63.129.16), which resolves the private zone linked to VNet1. That address cannot be reached from on-premises. After the migration, on-premises DNS servers resolve an Azure Private DNS zone by forwarding queries to the inbound endpoint of an Azure DNS Private Resolver over ExpressRoute. You therefore modify the conditional forwarder for contoso.com on Server1 to point to the inbound endpoint IP address of PR1. An outbound endpoint and a DNS forwarding ruleset handle the opposite direction: queries from Azure to on-premises or other custom DNS servers. A secondary zone cannot be created from an Azure Private DNS zone, because Azure Private DNS does not support zone transfers.
You have on-premises file servers that run Windows Server as shown in the following table.
| Name | Relevant folder |
| --- | --- |
| Server1 | D:\Folder1, E:\Folder2 |
| Server2 | D:\Data |
You have the Azure file shares shown in the following table.
| Name | Location |
| --- | --- |
| share1 | East US |
| share2 | East US |
You add a Storage Sync Service named Sync1 and an Azure File Sync sync group named Group1. Group1 uses share1 as a cloud endpoint.
You register Server1 and Server2 with Sync1. You add D:\Folder1 from Server1 as a server endpoint in Group1.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Explanation
Statement 1 (No): A sync group contains exactly one cloud endpoint, and Group1 already uses share1. To sync share2 you would create another sync group.
Statement 2 (No): A registered server can have several server endpoints, but a sync group can have only one server endpoint per registered server at a time. Server1 already provides D:\Folder1 to Group1, so E:\Folder2 would have to sync through a different sync group.
Statement 3 (Yes): Server2 is registered with Sync1 and has no server endpoint in Group1 yet, so D:\Data can be added. Other server endpoints in a sync group must be on different registered servers, which is the case here.
You need to sync files from an on premises server named Server1 to Azure by using Azure File Sync.
You have a cloud tiering policy that is configured for 30 percent free space and 70 days.
Volume E on Server1 is 500 GB.
A year ago, you configured E:\Data on Server1 to sync by using Azure File Sync. The files that are visible in E:\Data are shown in the following table.
Volume E does NOT contain any other files.
Where are File1 and File3 located? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Hot Area:
| Name | Size | Last accessed |
|------|------|---------------|
| File1 | 200 GB | 2 days ago |
| File2 | 100 GB | 10 days ago |
| File3 | 200 GB | 60 days ago |
| File4 | 50 GB | 100 days ago |
Explanation
File1: Server1 and the Azure file share — Every file in a synced folder is uploaded to the Azure file share, so the cloud copy always exists. File1 is the most recently accessed file, so cloud tiering keeps its content cached on volume E as well.
File3: The Azure file share only — Two cloud tiering policies apply. The date policy (70 days) tiers File4, which was last accessed 100 days ago. The volume free space policy (30 percent) requires 150 GB of the 500 GB volume to stay free, so at most 350 GB of file content can be cached locally. Files are kept in order of most recent access: File1 (200 GB) and File2 (100 GB) use 300 GB, and caching File3 (200 GB) as well would exceed 350 GB. So File3 is tiered: its content exists only in the Azure file share, and Server1 keeps only a reparse point that recalls the file when it is opened.
You have on-premises servers that run Windows Server as shown in the following table.
You have an Azure file share named share1 that stores two files named File2.docx and File3.docx.
You create an Azure File Sync sync group that includes the following endpoints:
✑ share1
✑ D:\Folder1 on Server1
✑ D:\Data1 on Server2
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Hot Area:
| Name | Local content |
| --- | --- |
| Server1 | D:\Folder1\File1.docx |
| Server2 | D:\Data1\File3.docx |
Explanation
Statement 1 (Yes): A server endpoint stays an ordinary writable NTFS folder. Creating File2.docx in D:\Folder1 on Server1 succeeds; if the name collides with File2.docx in share1, Azure File Sync keeps both files as a sync conflict instead of blocking the write.
Statement 2 (Yes): File1.docx can be created in D:\Data1 on Server2 like any other file; it is then uploaded to share1 and synced to the other endpoints.
Statement 3 (Yes): Sync is multi-master: every file in the sync group is synced to every server endpoint. File3.docx existed in both share1 and D:\Data1 on Server2 before the server endpoint was created, so Azure File Sync creates a conflict file and keeps both versions: the most recently written one keeps the name File3.docx and the older one is renamed with its endpoint name (for example File3-Server2.docx or File3-Cloud.docx). File3.docx is therefore synced to D:\Folder1 on Server1.
You have a file server named Server1 that runs Windows Server and contains the volumes shown in the following table.
On which volumes can you use BitLocker Drive Encryption (BitLocker) and disk quotas? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Hot Area:
| Name | File system |
|------|-------------|
| C | NTFS |
| D | NTFS |
| E | REFS |
Explanation
BitLocker: C, D, and E — BitLocker Drive Encryption works at the volume level, below the file system, so it supports every volume Windows Server can mount, including the operating system volume C and the data volumes D and E regardless of whether they are formatted with NTFS or ReFS (BitLocker also supports FAT32/exFAT on removable data drives). Because encryption is applied to the underlying volume rather than to individual files or metadata, the non-NTFS volume E is not excluded, which is why the narrower answers such as "C and D only" are incorrect.
Disk quotas: C and D only — the per-user disk quota feature configured on the Quota tab of a volume's properties is an NTFS-only feature; it relies on NTFS metadata that tracks file ownership and per-owner charged space, so it can only be enabled on NTFS-formatted volumes such as C and D. Volume E is not NTFS (ReFS and FAT-based file systems have no quota metadata), so "C, D, and E" is wrong; note that File Server Resource Manager quotas are a separate, folder-based mechanism and are not what the built-in disk quota feature offers here.
You have a server that runs Windows Server and contains a shared folder named UserData.
You need to limit the amount of storage space that each user can consume in UserData.
What should you use?
- A. Storage Spaces
- B. Work Folders
- C. Distributed File System (DFS) Namespaces
- D. File Server Resource Manager (FSRM) Correct
Explanation
File Server Resource Manager (FSRM) provides quota management capabilities that allow you to limit the amount of storage space each user can consume in a shared folder like UserData. This feature directly addresses the requirement specified in the question.
Your network contains an Active Directory Domain Services (AD DS) domain named contoso.com. The domain contains two servers named Server1 and Server2.
Server1 contains a disk named Disk2. Disk2 contains a folder named UserData. UserData is shared to the Domain Users group. Disk2 is configured for deduplication. Server1 is protected by using Azure Backup.
Server1 fails.
You connect Disk2 to Server2.
You need to ensure that you can access all the files on Disk2 as quickly as possible.
What should you do?
- A. Create a storage pool.
- B. Restore files from Azure Backup.
- C. Install the File Server Resource Manager server role.
- D. Install the Data Deduplication server role. Correct
Explanation
Disk2 was configured for deduplication on Server1. To access all files quickly after connecting Disk2 to Server2, the Data Deduplication server role must be installed on Server2 to recognize and process the deduplicated data correctly.
You have five file servers that run Windows Server.
You need to block users from uploading video files that have the .mov extension to shared folders on the file servers. All other types of files must be allowed. The solution must minimize administrative effort.
What should you create?
- A. a Dynamic Access Control central access policy
- B. a data loss prevention (DLP) policy
- C. a Dynamic Access Control central access rule
- D. a file screen Correct
Explanation
A file screen is the appropriate solution to block users from uploading .mov files while allowing other types of files. File Server Resource Manager (FSRM) enables creating file screening rules that monitor and restrict specific file types, minimizing administrative effort.
Your network contains an Active Directory Domain Services (AD DS) domain named adatum.com. The domain contains a file server named Server1 and three users named User1, User2, and User3.
Server1 contains a shared folder named Share1 that has the configurations shown in the Share Configuration exhibit.
The share permissions for Share1 are configured as shown in the Share Permissions exhibit.
Share1 contains a file named File1.txt. The advanced security settings for File1.txt are configured as shown in the File Permissions exhibit.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Explanation
Statement 1 (No): When a file is reached through a share, the effective access is the more restrictive of the share permission and the NTFS permission. Domain Users have only Change (and Read) on Share1. Taking ownership requires the Take ownership right, which only the Full Control share permission passes through, so User1's NTFS Full Control is limited by the share and User1 cannot take ownership over the network. Statement 2 (Yes): Share1 uses access-based enumeration (FolderEnumerationMode is AccessBased), which hides only the files and folders a user has no permission to access. User2 has the NTFS Read permission on File1.txt and the share allows Read, so File1.txt is listed. Statement 3 (Yes): User3 has an explicit NTFS Write permission on File1.txt and the share allows Change, so User3 has permissions on the file and access-based enumeration does not hide it. User3 can see File1.txt, although Write alone does not let User3 open the file to read its contents.
You have a server named Server1.
You plan to use Storage Spaces to expand the storage available to Server1. You attach eight physical disks to Server1. Four disks are HDDs and four are SSDs.
You need to create a volume on Server1 that will use the storage on all the new disks. The solution must provide the fastest read performance for frequently used files.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Explanation
1. Create a storage pool: Storage Spaces first groups all eight new physical disks (four SSDs and four HDDs) into one storage pool. The disks do not need to be converted to dynamic or GPT disks first; that is handled when they are added to the pool.
2. Create a virtual disk: in the New Virtual Disk Wizard, select Create storage tiers on this virtual disk. With tiering, Storage Spaces keeps the most frequently used data on the SSD tier and moves less-used data to the HDD tier, which gives the fastest reads for frequently used files while still using the space on all the disks.
3. Create a simple volume: create a volume on the new virtual disk, assign a drive letter and format it. A spanned volume is a dynamic-disk feature and is not used with Storage Spaces.
Your network contains an Active Directory Domain Services (AD DS) domain named adatum.com. The domain contains a server named Server1 and the users shown in the following table.
Server1 contains a folder named D:\Folder1. The advanced security settings for Folder1 are configured as shown in the Permissions exhibit. (Click the
Permissions tab.)
Folder1 is shared by using the following configurations:
The share permissions for Share1 are shown in the following table.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Hot Area:
| Name | Member of |
| --- | --- |
| User1 | Group1 |
| User2 | Group2 |
| User3 | Group3 |
| Group | Permission |
| --- | --- |
| Group1 | Allow – Change |
| Group3 | Allow – Full Control |
Explanation
Statement 1 (Yes): User1 is a member of Group1. Group1 has Allow - Change on Share1 and Allow - Read in the NTFS permissions on D:\Folder1. Effective access over the share is the more restrictive of the two, which is Read, so User1 can read the files.
Statement 2 (No): User3 is a member of Group3. Group3 has Full Control on the share but no NTFS entry on Folder1 (only Administrators, Group1 and Group2 are listed). Without NTFS permission, User3 cannot access the files, so User3 cannot delete them.
Statement 3 (Yes): FolderEnumerationMode for Share1 is Unrestricted, which means access-based enumeration is off. Every user who browses \\Server1.adatum.com sees Share1, even User2, whose group (Group2) has no share permission. User2 can see the share but cannot open it.
Your network contains an Active Directory Domain Services (AD DS) domain named contoso.com. The domain contains a server named Server1 that has the
DFS Namespaces role service installed. Server1 hosts a domain-based Distributed File System (DFS) Namespace named Files.
The domain contains a file server named Server2. Server2 contains a shared folder named Share1. Share1 contains a subfolder named Folder1.
In the Files namespace, you create a folder named Folder1 that has a target of \\Server2.contoso.com\Share1\Folder1.
You need to configure a logon script that will map drive letter M to Folder1. The solution must use the path of the DFS Namespace.
How should you configure the command to map the drive letter? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Hot Area:
Explanation
net use m: (namespace server): \\contoso.com — Files is a domain-based namespace, so its UNC path begins with the fully qualified domain name of the AD DS domain that hosts it (\\contoso.com\...), and clients resolve that name through a domain controller to a referral list of namespace servers. Using \\Server1.contoso.com would work only as a stand-alone/server-based path that hard-codes one namespace server and loses the fault tolerance and referral behavior of the domain-based namespace, and \\Server2.contoso.com would bypass DFS entirely by pointing straight at the folder target instead of the namespace; \\files.contoso.com is not a valid form because "Files" is the namespace name, not a DNS host name.
net use m: (folder path): \files\folder1 — After the domain name, a domain-based namespace path continues with the namespace root name (Files) and then the namespace folder name (Folder1), producing \\contoso.com\Files\Folder1. The namespace hides the physical target, so the share and subfolder names on the file server (Share1\Folder1) do not appear in the path — that is why \files\share1\folder1 and \share1\folder1 are incorrect — and \folder1 alone is wrong because it omits the namespace root that must follow the domain name.
You have two on-premises servers named Server1 and Server2 that run Windows Server.
You have an Azure Storage account named storage1 that contains a file share named share1. Server1 syncs with share1 by using Azure File Sync.
You need to configure Server2 to sync with share1.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Explanation
First, install the Azure File Sync agent on Server2; the agent is what performs synchronization and it provides the server registration UI. Next, register Server2 with the existing Storage Sync Service, which establishes trust between the server and the service (a server can be registered with only one Storage Sync Service). Finally, add a server endpoint for Server2 to the existing sync group that already contains share1 as its cloud endpoint. A new Storage Sync Service and a new cloud endpoint are not needed because Server1 already syncs with share1 through an existing service and sync group.
You have a server named Server1 that runs Windows Server. Server1 has the storage pools shown in the following table.
| Name | Number of 7,200-RPM HDDs | Number of 10,000-RPM HDDs | Number of SSDs |
|---|---|---|---|
| Pool1 | 4 | 4 | None |
| Pool2 | None | 2 | 2 |
| Pool3 | 8 | None | 4 |
You plan to create a virtual disk named VDisk1 that will use storage tiers.
Which pools can you use to create VDisk1?
- A. Pool2 only
- B. Pool1 only
- C. Pool1, Pool2, and Pool3
- D. Pool1 and Pool2 only
- E. Pool3 only
- F. Pool2 and Pool3 only Correct
- G. Pool1 and Pool3 only
Explanation
To create a virtual disk with storage tiers in Windows Server, you need at least one SSD and one physical drive (HDD). Pool2 and Pool3 meet this requirement as both include SSDs along with HDDs.
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result these questions will not appear in the review screen.
You have a server named Server1 that runs Windows Server 2022 and has the DHCP Server role. Server1 contains a single DHCP scope named Scope1.
You deploy five printers to the network.
You need to ensure that the printers are always assigned the same IP address.
Solution: You create a DHCP address exclusion for each printer.
Does this meet the requirement?
Explanation
Creating a DHCP address exclusion prevents IP addresses from being assigned to any device, which does not ensure that printers are always assigned the same IP address. Instead, reservations should be created for each printer to guarantee consistent IP assignments.
You have two servers that have the Hyper-V server role installed. The servers are joined to a failover cluster. Both servers can connect to the same disk on an iSCSI storage device.
You plan to use the iSCSI storage to store highly available Hyper-V virtual machines that will support live migration functionality.
You need to configure a storage resource in the failover cluster to store the virtual machines.
What should you configure?
- A. Cluster Shared Volumes (CSV) Correct
- B. Distributed File System (DFS) Replication
- C. a storage pool
- D. a mirrored volume
Explanation
Cluster Shared Volumes (CSV) is the correct configuration for storing highly available Hyper-V virtual machines that support live migration. CSV allows multiple nodes in a failover cluster to simultaneously access the same LUN on an iSCSI storage device, enabling seamless live migrations.
You have a server named Server1 that runs Windows Server.
You plan to host applications in Windows containers.
You need to configure Server1 to run containers.
What should you install?
- A. Windows Admin Center
- B. Docker Correct
- C. the Windows Subsystem for Linux
- D. Hyper-V
Explanation
To run Windows containers, Server1 needs the Containers feature and a container runtime. Docker provides the runtime and the tools to pull images, then create, run and manage containers, so Docker is what you install. Hyper-V is not required: Windows Server containers run with process isolation by default, and the Hyper-V role is needed only if you choose Hyper-V isolation. Windows Admin Center is a management console and can manage containers, but it does not run them. The Windows Subsystem for Linux runs Linux binaries and is not used for Windows containers.
You have a server named Server1 that runs Windows Server. Server1 has a just-a-bunch-of-disks (JBOD) enclosure attached.
You plan to create a storage pool on Server1 and a virtual disk that will use a mirror layout.
You are considering whether to use a two-way or a three-way mirror layout.
What is the minimum number of disks required for each type of mirror layout? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Hot Area:
Explanation
Two-way mirror: 2 — A two-way mirror in Storage Spaces writes two identical copies of every slab, so the storage pool must contain at least two physical disks in the JBOD enclosure to hold those copies on separate devices; the layout then tolerates the loss of a single disk. Choosing 1 is impossible because a single disk cannot hold two independent copies, and higher numbers exceed the minimum Windows Server enforces.
Three-way mirror: 5 — Although a three-way mirror keeps three copies of the data, Storage Spaces requires a minimum of five physical disks for this layout so the pool can survive two simultaneous disk failures and still have capacity to repair and redistribute the remaining copies. Answering 3 is the common mistake: three disks match the number of data copies but fall short of the five-disk minimum that Windows Server requires when creating a three-way mirror virtual disk.
Your company has offices in Boston and Montreal. The offices are connected by using a 10-Mbps WAN link that is often saturated.
The office in Boston contains the following:
✑ An Active Directory Domain Services (AD DS) domain controller named DC1
✑ A server named Server1 that runs Windows Server and has the File Server role installed
The office in Montreal contains 20 client computers that run Windows 10. Montreal does NOT have any servers.
The company plans to deploy a new line-of-business (LOB) application to all the client computers. The installation source files for the application are in \\Server1
\Apps.
You need to make the installation source files available to the client computers in the Montreal office by using the minimum amount of WAN bandwidth possible.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Hot Area:
Explanation
On Server1: Install the BranchCache for network files role service. Server1 is a file server, and a Windows Server file server can offer BranchCache content for SMB shares such as \\Server1\Apps only after the BranchCache for Network Files role service of the File Server role is installed (and BranchCache hash publication is enabled for the share or server). Hosted cache mode and distributed cache mode are client or branch caching modes, not settings on the content server.
On the client computers: Enable BranchCache in Distributed cache mode. Montreal has no server, so hosted cache mode is not possible because it needs a hosted cache server in the branch. In distributed cache mode, the first Windows 10 client that downloads the installation files over the WAN caches them, and the other Montreal clients get the content from that peer on the LAN, so the files cross the saturated 10-Mbps link only once.
You have an on-premises Active Directory Domain Services (AD DS) domain that syncs with an Azure Active Directory (Azure AD) tenant. Group writeback is enabled in Azure AD Connect.
The AD DS domain contains a server named Server1. Server1 contains a shared folder named share1.
You have an Azure Storage account named storage2 that uses Azure AD-based access control. The storage2 account contains a share named share2.
You need to create a security group that meets the following requirements:
✑ Can contain users from the AD DS domain
✑ Can be used to authorize user access to share1 and share2
What should you do?
- A. In the Azure AD tenant, create a security group that has assigned membership.
- B. In the AD DS domain, create a universal security group. Correct
- C. In the Azure AD tenant, create a security group that has dynamic membership.
- D. In the Azure AD tenant, create a Microsoft 365 group.
Explanation
A universal security group created in the AD DS domain can contain users from the AD DS domain and can be used in NTFS/share permissions on share1. Azure AD Connect synchronizes the on-premises group to Azure AD, so the same group can be assigned share-level permissions (Azure RBAC) on share2 in storage2, which uses identity-based access with hybrid identities. Groups created in the Azure AD tenant (assigned, dynamic, or Microsoft 365) do not exist in AD DS by default and cannot be used to authorize access to share1; group writeback only writes cloud groups back to AD DS and is not needed for this solution.
You have a Group Policy Object (GPO) named GPO1 that contains user settings only.
You plan to apply GPO1 to a global security group named Group1.
You link GPO1 to the domain, and you remove all the permissions granted to the Authenticated Users group.
You need to configure permissions for GPO1 to meet the following requirements:
✑ GPO1 must apply only to the users in Group1.
✑ The solution must use the principle of least privilege.
Which permissions should you grant to Group1 and the Domain Computers group? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Hot Area:
Explanation
Group1: Apply group policy and Read. GPO1 contains only user settings and must apply only to the users in Group1. Security filtering requires the target users to have both Read and Apply group policy on the GPO; with Read only, the users could read GPO1 but would never process it.
Domain Computers: Read only. Since security update MS16-072, the Group Policy client retrieves user policy in the computer's security context. Because Authenticated Users was removed from GPO1, the computers that Group1 users sign in to need Read on GPO1, or the GPO is never downloaded. Microsoft's guidance is to grant Domain Computers Read and not Apply group policy, which also meets the least-privilege requirement.
Your network contains a two-domain on-premises Active Directory Domain Services (AD DS) forest named contoso.com. The forest contains the domain controllers shown in the following table.
All domain controllers are backed up by using Azure Backup.
You create an Active Directory site named Site3. Site1, Site2, and Site3 each has a dedicated site link to the Hub site.
In Site3, you install a new server named Server1.
You need to promote Server1 to an RODC in child.contoso.com by using the Install from Media (IFM) option. The solution must minimize network traffic.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Hot Area:
| Name | Description | Domain | Active Directory site |
| --- | --- | --- | --- |
| DC1 | Forest-wide and domain-wide FSMO role holder | contoso.com | Hub |
| DC2 | Domain-wide FSMO role holder | child.contoso.com | Site1 |
| RODC3 | Read-only domain controller (RODC) | contoso.com | Site2 |
Explanation
Server to use to create the IFM source: DC2. Install from Media must use media taken from a domain controller in the same domain as the new domain controller. Server1 will become an RODC in child.contoso.com. DC2 is the only domain controller in that domain and it is writable, so its media lets Server1 be promoted with little replication traffic across the site links. DC1 and RODC3 belong to the contoso.com domain, so their databases cannot seed a domain controller for child.contoso.com. Server1 is not yet a domain controller and has no directory database to export.
Tool to use to create the IFM source: Ntdsutil.exe. You run ntdsutil, then 'activate instance ntds', 'ifm', and 'create sysvol rodc <folder>' (or 'create rodc'). This exports the directory database, plus SYSVOL if requested, in the form the AD DS installation wizard expects, and it strips cached secrets such as passwords from RODC media. Azure Backup produces cloud recovery points, not IFM media. Dcdiag.exe and Repadmin.exe are diagnostic and replication tools that cannot create installation media. Windows Server Backup does not prepare the dedicated, secret-free RODC media that the ifm create rodc command produces.
You deploy a single-domain Active Directory Domain Services (AD DS) forest named contoso.com.
You deploy a server to the domain and configure the server to run a service.
You need to ensure that the service can use a group managed service account (gMSA) to authenticate.
Which three PowerShell cmdlets should you run in sequence? To answer, move the appropriate cmdlets from the list of cmdlets to the answer area and arrange them in the correct order.
Explanation
1. Add-KdsRootKey: gMSA passwords are generated by the Key Distribution Service, so the domain needs a KDS root key before you can create any gMSA. In production, allow up to 10 hours for the key to replicate. 2. New-ADServiceAccount: creates the gMSA in contoso.com. Use -PrincipalsAllowedToRetrieveManagedPassword to name the server (or a group that contains it) that may retrieve the password. 3. Install-ADServiceAccount: run this on the server to install the gMSA locally, so the service can be configured to run as the account. Add-ADComputerServiceAccount, Set-KdsConfiguration and Add-ADGroupMember are not required in this sequence.
You have an on-premises DNS server named Server1 that runs Windows Server. Server1 hosts a DNS zone named fabrikam.com.
You have an Azure subscription that contains the resources shown in the following table.
| Name | Type | Description |
| --- | --- | --- |
| Vnet1 | Virtual network | Connects to the on-premises network by using a Site-to-Site VPN |
| VM1 | Virtual machine | Runs Windows Server and has the DNS Server role installed |
| contoso.com | Private DNS zone | Linked to Vnet1 |
| contoso.com | Public DNS zone | Contains the DNS records of all the platform as a service (PaaS) resources |
You need to design a solution that will automatically resolve the names of any PaaS resources for which you configure private endpoints in Vnet1.
How should you configure the name resolution? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Explanation
On Vnet1: Configure VM1 to forward requests for the contoso.com zone to the Azure-provided DNS at 168.63.129.16. The private endpoint A records are written to the private contoso.com zone, which is linked to Vnet1. Only Azure DNS (168.63.129.16) can resolve a private DNS zone, and only for queries that come from a virtual network linked to it. VM1 runs in Vnet1, so it acts as the DNS forwarder and sends contoso.com queries to 168.63.129.16. Forwarding to the public zone would return the public IP addresses of the PaaS resources instead of the private endpoint addresses.
On the on-premises network: Configure forwarding for the contoso.com zone to VM1. Server1 cannot query the private zone directly. 168.63.129.16 is reachable only from inside an Azure virtual network, never from on-premises, even over a VPN. Server1 therefore needs a conditional forwarder for contoso.com that points to VM1, and VM1 proxies the query to Azure DNS from inside Vnet1. New private endpoints then resolve automatically from both networks.
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
Your network contains an Active Directory Domain Services (AD DS) domain named contoso.com.
You need to identify which server is the PDC emulator for the domain.
Solution: From Active Directory Users and Computers, you right-click contoso.com in the console tree, and then select Operations Master.
Does this meet the goal?
Explanation
Yes. In Active Directory Users and Computers, right-clicking the domain node (contoso.com) and selecting Operations Masters opens the Operations Masters dialog. It has RID, PDC, and Infrastructure tabs, and the PDC tab shows which domain controller holds the PDC emulator role for the domain. This is Microsoft's documented way to identify the PDC emulator in the GUI. You can get the same result with netdom query fsmo or Get-ADDomain | Select-Object PDCEmulator.
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result these questions will not appear in the review screen.
You have a server named Server1 that runs Windows Server 2022 and has the DHCP Server role. Server1 contains a single DHCP scope named Scope1.
You deploy five printers to the network.
You need to ensure that the printers are always assigned the same IP address.
Solution: You deploy a DHCP relay agent to the network.
Does this meet the requirement?
Explanation
Deploying a DHCP relay agent does not ensure that the printers are always assigned the same IP address. To meet this requirement, reservations or static assignments within the DHCP scope should be configured for each printer.
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
Your network contains an Active Directory Domain Services (AD DS) forest. The forest contains three Active Directory sites named Site1, Site2, and Site3. Each site contains two domain controllers. The sites are connected by using DEFAULTIPSITELINK.
You open a new branch office that contains only client computers.
You need to ensure that the client computers in the new office are primarily authenticated by the domain controllers in Site1.
Solution: You create a new subnet object that is associated to Site1.
Does this meet the goal?
Explanation
Creating a new subnet object associated with Site1 ensures that client computers in the new office are primarily authenticated by domain controllers within Site1. This is because Active Directory uses subnet-to-site associations to direct authentication requests to the nearest site's domain controllers.
Your network contains an Active Directory Domain Services (AD DS) domain named contoso.com.
The network contains the servers shown in the following table.
| Name | Role | Domain/workgroup | Operating system |
| --- | --- | --- | --- |
| DC1 | Active Directory Domain Services, DNS Server | contoso.com | Windows Server |
| Server1 | DHCP Server | contoso.com | Windows Server |
| Server2 | None | contoso.com | Windows Server Core |
| Server3 | None | Workgroup1 | Windows Server Core |
You plan to implement IP Address Management (IPAM).
You need to use the Group Policy based provisioning method for managed servers. The solution must support server discovery.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Hot Area:
Explanation
Server on which to deploy the IPAM server role: Server2 — The IPAM Server feature must be installed on a domain-joined member server, and Microsoft explicitly does not support installing IPAM on a domain controller or on the same machine as a DHCP server (IPAM disables DHCP server discovery on such a host), so DC1 is not a valid target and Server2 is the member server that carries no conflicting infrastructure role.
Servers that must be provisioned for IPAM: DC1 and Server1 — Provisioning applies only to the managed infrastructure servers that IPAM discovers and administers, namely the domain controllers, DNS servers, DHCP servers, and NPS servers in the domain; the IPAM server itself is never provisioned as a managed server. With Group Policy based provisioning, running Invoke-IpamGpoProvisioning creates the IPAM_DC_NPS_Server, IPAM_DHCP, and IPAM_DNS GPOs, and each discovered server has the matching GPO applied so IPAM gains the firewall rules, security group membership, and audit/share permissions it needs — hence DC1 (domain controller/DNS) and Server1 (DHCP) are the servers to provision, not Server2, which hosts IPAM itself.
Your company has a main office and 10 branch offices that are connected by using WAN links. The network contains an Active Directory domain.
All users have laptops and regularly travel between offices.
You plan to implement BranchCache in the branch offices.
In each branch office, you install a server that runs Windows Server and the BranchCache feature. You register the servers in Active Directory.
You need to configure the laptops to use the local BranchCache server automatically. The solution must minimize administrative effort.
Which two Group Policy settings should you configure? To answer, select the settings in the answer area.
NOTE: Each correct selection is worth one point.
Explanation
Statement 1 (Yes): Turn on BranchCache enables BranchCache on the client laptops. No other BranchCache client setting takes effect without it.
Statement 2 (No): Set BranchCache Distributed Cache mode makes clients cache and share content with peers on the same subnet. It does not use the branch office servers.
Statement 3 (No): Set BranchCache Hosted Cache mode points clients to hosted cache servers by a fixed name. Laptops that travel between offices would keep using one office's server, and every branch would need its own setting.
Statement 4 (Yes): Enable Automatic Hosted Cache Discovery by Service Connection Point makes clients find the hosted cache server for the office they are in, by using the service connection point that the server registered in Active Directory. This works for traveling users and needs no per-office configuration, so it minimizes administrative effort.
Statement 5 (No): Configure Hosted Cache Servers lists specific hosted cache servers by name. This is a static list, so it is not automatic.
Statement 6 (No): Configure BranchCache for network files sets the round-trip latency at which clients start caching SMB content. It does not help clients find a server.
Statement 7 (No): Set percentage of disk space used for client computer cache only sets the size of the local cache.
Statement 8 (No): Set age for segments in the data cache only sets how long cached segments stay valid.
Statement 9 (No): Configure Client BranchCache Version Support only sets which BranchCache version clients use.
You have an Azure subscription that contains the storage accounts shown in the following table.
In the East US Azure region, you create a storage sync service named Sync1.
You need to create a sync group in Sync1.
Which storage accounts can you use, and what can you specify as the cloud endpoints. To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
| Name | Location | Kind | Container | File share |
| --- | --- | --- | --- | --- |
| storage1 | East US | StorageV2 | cont1 | share1 |
| storage2 | East US | BlockBlobStorage | cont2 | Not applicable |
| storage3 | East US | FileStorage | Not applicable | share3 |
| storage4 | Central US | StorageV2 | cont4 | share4 |
Explanation
Storage accounts: storage1 and storage3 only — A sync group's cloud endpoint must live in a storage account that is in the same Azure region as the Storage Sync Service (Sync1 is in East US) and that supports Azure Files, so only the East US, Azure Files–capable accounts qualify; storage1 and storage3 meet both conditions. The wider choices that add storage2 and storage4 fail one of those tests (wrong region, or an account type/configuration that cannot host the Azure file share a cloud endpoint requires), so options such as "storage1, storage2, storage3, and storage4" are not valid.
Cloud endpoints: share1 and share3 only — The cloud endpoint of an Azure File Sync sync group is always an Azure file share, never a blob container, so cont1, cont2, and cont4 can never be selected regardless of which account they sit in. That leaves the file shares in the eligible East US accounts, share1 and share3; share4 is excluded because its storage account is not usable with Sync1, which rules out "share1, share3, and share4 only" and every option that mixes in containers.
You have a server named Server1 that runs Windows Server and contains two drives named C and D. Server1 hosts multiple file shares.
You enable Data Deduplication on drive D and select the General purpose file server workload.
You need to minimize the space consumed by files that were recently modified or deleted.
What should you do?
- A. Run the Set-DedupVolume cmdlet and configure the Scrubbing job.
- B. Run the Set-DedupSchedule cmdlet and configure a GarbageCollection job. Correct
- C. Run the Set-DedupVolume cmdlet and configure the InputOutputScale settings.
- D. Run the Set-DedupSchedule cmdlet and configure the Optimization job.
Explanation
The GarbageCollection job reclaims disk space by removing unnecessary chunks that are no longer referenced by recently modified or deleted files. This directly addresses the need to minimize space consumed by such files.
You have a server named Server1 that runs Windows Server and contains three volumes named C, D, and E.
Files are stored on Server1 as shown in the following table.
| Name | On volume | Size |
| --- | --- | --- |
| File1 | C | 500 KB |
| File2 | D | 10 KB |
| File3 | D | 1 MB |
For volume D, Data Deduplication is enabled and set to General purpose file server.
You perform the following actions:
• Move File1 to volume D.
• Copy File2 to volume D and name the copy File4.
• Move File3 to volume E.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Explanation
Statement 1 (Yes): File1 is moved to volume D, the only volume with Data Deduplication enabled. A move keeps the file's existing timestamps, so it is not treated as a newly created file, and at 500 KB it is well above the 32 KB minimum file size, so the optimization job deduplicates it.
Statement 2 (No): Data Deduplication is enabled per volume. File3 is moved to volume E, which does not have Data Deduplication enabled, so no optimization job processes it there.
Statement 3 (No): File4 is a copy of File2, so it is only 10 KB. Data Deduplication only considers files larger than 32 KB (the MinimumFileSize setting cannot be set below 32 KB), so File4 is never optimized. It is also a newly created file, and the General purpose file server usage type waits 3 days after a file is created (MinimumFileAgeDays) before the file is in policy.
You have an Active Directory domain that contains a file server named Server1. Server1 runs Windows Server and includes the file shares shown in the following table.
| Share Name | Path |
|---|---|
| Users | D:\Users |
| Accounts | D:\Dept\Accounts |
| Marketing | D:\Dept\Marketing |
| CustomerService | D:\Dept\CustomerService |
When users login to the network they receive the following network drive mappings.
• H: maps to \\server1\users\%UserName%
• G: maps to \\server1\%Department%
You need to limit the amount of space consumed by user’s on Server1. The solution must meet the following requirements:
• Prevent users using more than 5GB of space on their H: drive
• Prevent Accounts department users from using more than 10GB of space on the G: drive
• Prevent Marketing department users from using more than 15GB of space on the G: drive
• Prevent Customer Service department users from using more than 2GB of space on the G: drive
• Minimize administrative effort
What should you use?
- A. File Server Resource Manager (FSRM) quotas Correct
- B. Storage tiering
- C. NTFS Disk quotas
- D. Group Policy Preferences
Explanation
File Server Resource Manager (FSRM) quotas are the appropriate solution as they allow for setting space limits on specific shares and paths, which aligns with the requirement to limit user space consumption on H: and G: drives based on department. This minimizes administrative effort by centrally managing these quotas through FSRM.
You have an Azure subscription that contains the storage accounts shown in the following table.
| Name | Location | File share | Blob container |
|---|---|---|---|
| storage1 | West US | share1 | None |
| storage2 | West US | share2 | container2 |
| storage3 | Central US | share3 | None |
| storage4 | Central US | share4 | container4 |
In the West US Azure region, you create a storage sync service named SyncA.
You plan to create a sync group named GroupA.
What is the maximum number of cloud endpoints you can use with GroupA?
- A. 1 Correct
- B. 2
- C. 3
- D. 4
Explanation
According to Microsoft's official documentation on Azure Storage Sync, a sync group can only have one cloud endpoint. This limitation ensures that all data within the sync group is synchronized with a single cloud storage location.
You have an on-premises server named Server1 that runs Windows Server. Server1 contains a file share named Share1.
You have an Azure subscription.
You perform the following actions:
• Deploy Azure File Sync.
• Install the Azure File Sync agent on Server1.
• Register Server1 with Azure File Sync.
You need to ensure that you can add Share1 as an Azure File Sync server endpoint.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Explanation
To add Share1 as an Azure File Sync server endpoint, you must first create an Azure Storage account to host the files. Next, create an Azure file share within this storage account for synchronization purposes. Finally, create a sync group to manage the synchronization between the on-premises file share and the Azure file share.
You have a server named Server1 that runs Windows Server. The disks on Server1 are configured as shown in the following exhibit.
You need to convert volume E to ReFS. The solution must meet the following requirements:
• The data on volume E needs to be retained.
• Minimize administrative effort.
What should you do first?
- A. Back up the data on volume E. Correct
- B. Take Disk 2 offline.
- C. Convert Disk 2 to a dynamic disk.
- D. Run convert.exe.
Explanation
The exhibit shows that volume E is a 127 GB exFAT primary partition on basic Disk 2. Windows cannot convert any file system to ReFS in place, so the only way to get ReFS is to format the volume, which erases it. To keep the data, first back up the data on volume E, then format E as ReFS, then restore the data.
convert.exe converts FAT and FAT32 volumes to NTFS only, never to ReFS. Taking Disk 2 offline or converting it to a dynamic disk does nothing toward the conversion and only adds steps.
You have a disaggregated cluster deployment. The deployment contains a scale-out file server (SOFS) cluster that runs Windows Server and a compute cluster that has the Hyper-V role enabled.
You need to implement Storage Quality of Service (QoS). The solution must ensure that you can control the bandwidth usage between the SOFS cluster and the Hyper-V cluster.
Which cmdlet should you run on each cluster? To answer, drag the appropriate cmdlets to the correct clusters. Each cmdlet may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
Explanation
SOFS: New-StorageQosPolicy. The Storage QoS Policy Manager runs on the Scale-Out File Server cluster, so policies (minimum and maximum normalized IOPS, and maximum bandwidth) are created there with New-StorageQosPolicy. Each policy gets a PolicyId.
Hyper-V: Set-VMHardDiskDrive. A policy only takes effect once it is assigned to virtual hard disks. On the Hyper-V compute cluster, you run Set-VMHardDiskDrive -QoSPolicyID <PolicyId> against the VMs' disks, which links each disk's I/O flow to the policy managed by the SOFS cluster. Set-VMSan configures virtual Fibre Channel SANs and has nothing to do with Storage QoS.
You have an Active Directory Domain Services (AD DS) domain that contains the member servers shown in the following table.
Server3 contains a data disk named Disk1 that has Data Deduplication installed. Disk1 contains the files shown in the following table.
Server3 fails.
You need to recover the files on Disk1.
Which files can you recover if you attach Disk1 to Server1, and which files can you recover if you attach Disk1 to Server2? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
| Name | Operating system | Data Deduplication role service |
| --- | --- | --- |
| Server1 | Windows Server 2019 | Installed |
| Server2 | Windows Server 2022 | Not installed |
| Server3 | Windows Server 2022 | Installed |
| Name | Size |
| --- | --- |
| File1.txt | 5 KB |
| File2.docx | 800 KB |
| File3.sys | 2 MB |
| File4.bmp | 5 GB |
Explanation
Server1: File1.txt only. Data Deduplication replaces the data of each optimized file with a reparse point that points to chunks in the chunk store. Dedup is backward compatible but not forward compatible: an older Windows Server version cannot read data that a newer version deduplicated, and it reports those files as corrupted. Disk1 was deduplicated by Server3 (Windows Server 2022), and Server1 runs Windows Server 2019, so even with Data Deduplication installed it cannot read the optimized files File2.docx, File3.sys and File4.bmp. File1.txt is 5 KB. Data Deduplication only optimizes files larger than 32 KB, so File1.txt was never optimized. It is still a normal NTFS file that Server1 can read.
Server2: File1.txt only. Server2 runs Windows Server 2022 but does not have the Data Deduplication role service, so it has no deduplication filter to resolve the reparse points into the chunk store. The optimized files cannot be read there. File1.txt was never optimized, so it can be read. To recover every file, attach Disk1 to a server that runs Windows Server 2022 or later and has Data Deduplication installed, or install Data Deduplication on Server2.
You have a server named Server1 that runs Windows Server and contains a file share named Share1.
You need to prevent users from storing MP4 files in Share1. The solution must ensure that the users can store other types of files in the share.
What should you configure on Server1?
- A. File Management Tasks
- B. NTFS Quotas
- C. NTFS permissions
- D. file screens Correct
Explanation
File screens are used to prevent specific types of files from being created in a folder. Configuring a file screen on Share1 to block MP4 files meets the requirement without affecting other file types.
Your network contains an Active Directory Domain Services (AD DS) domain named contoso.com. The domain contains the servers shown in the following table.
| Name | Role |
|----------|-------------------------------|
| Server1 | DFS Namespaces |
| Server2 | DFS Replication |
| Server3 | DFS Namespaces, DFS Replication |
| Server4 | None |
You need to create a Distributed File System (DFS) namespace that will contain the following:
• A domain-based namespace named \\contoso.com\Public
• A folder named Finance
Which servers can you configure as folder targets for the Finance folder?
- A. Server3 only
- B. Server2 and Server3 only
- C. Server1 and Server3 only
- D. Server1, Server2, and Server3 only
- E. Server1, Server2, Server3, and Server4 Correct
Explanation
A folder target in a DFS namespace is just the UNC path of a shared folder (or of another namespace) that the namespace folder points to. Only the namespace servers that host the namespace root (\\contoso.com\Public) need the DFS Namespaces role service. The server that hosts a folder target only has to share the folder over SMB; it needs neither DFS Namespaces nor DFS Replication. DFS Replication is needed only if you want to keep several targets in sync. Server1, Server2, Server3 and Server4 can all share a folder, so any of them can be a folder target for Finance.
You have a server named Server1 that runs Windows Server 2022.
You add two 4-TB hard drives named Disk1 and Disk2 to Server1.
You need to format the drives. The solution must meet the following requirements:
• Disk1 must support disk level quotas.
• Disk2 must support Data Deduplication.
Which type of file system should you use for each drive? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Explanation
Disk1: NTFS only. Disk (volume) quotas, set on the Quota tab of a volume's properties, are an NTFS feature that tracks space per user by file ownership. ReFS does not support disk quotas, and exFAT has no ownership metadata to base them on.
Disk2: NTFS or ReFS only. Data Deduplication has supported NTFS data volumes since Windows Server 2012, and Windows Server 2019 added support for ReFS volumes, so on Windows Server 2022 either file system can be used. exFAT is not supported by Data Deduplication, which rules out the options that include exFAT.
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result these questions will not appear in the review screen.
You have a server named Server1 that runs Windows Server 2022 and has the DHCP Server role. Server1 contains a single DHCP scope named Scope1.
You deploy five printers to the network.
You need to ensure that the printers are always assigned the same IP address.
Solution: You configure the DHCP scope options for Scope1.
Does this meet the requirement?
Explanation
Configuring DHCP scope options for Scope1 does not ensure that the printers are always assigned the same IP address. To meet this requirement, you would need to create reservations within the DHCP scope for each printer, assigning them specific IP addresses.
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result these questions will not appear in the review screen.
You have a server named Server1 that runs Windows Server 2022 and has the DHCP Server role. Server1 contains a single DHCP scope named Scope1.
You deploy five printers to the network.
You need to ensure that the printers are always assigned the same IP address.
Solution: You create a DHCP reservation for each printer.
Does this meet the requirement?
Explanation
Creating a DHCP reservation for each printer ensures that the printers are always assigned the same IP address from the DHCP scope. This meets the requirement of providing consistent IP addresses to the networked devices.
You have a server named Server1 that runs Windows Server, has the File Server Resource Manager role service installed, and hosts a file share named Share02.
You need to configure Server1 to meet the following requirements:
• Notify administrators when a user uses more than 50 GB of space on Share02.
• Send administrators a weekly email that lists duplicate files on Server1.
The solution must minimize administrative effort.
What should you create for each requirement? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Explanation
Notify administrators when a user uses more than 50 GB of data on Share02.: A soft quota for Share2 — In File Server Resource Manager a soft quota does not enforce the limit; it simply monitors usage and fires the configured notification thresholds, so you can set a 50 GB quota on Share02 with a threshold action that emails administrators while users keep writing normally. A hard quota would also notify but would additionally block writes once 50 GB is reached, which the requirement never asks for, and a file screen controls which file types may be saved rather than how much space is consumed.
Send administrators a weekly email that lists duplicate files on Server1.: A report task — FSRM storage reports include a built-in Duplicate Files report, and a scheduled report task lets you run it against Server1 on a weekly schedule and have the generated report delivered automatically to an administrator email address, with no scripting involved. A classification rule only tags files with properties and a custom file management task acts on files (move, expire, run a command) rather than producing a scheduled duplicate-file report.
You have an on-premises server named Server1 that runs Windows Server 2022 and is a container host.
You have an Azure subscription.
You plan to develop custom container images.
You need to recommend a storage solution for the containers. The solution must meet the following requirements:
• Support the use of Docker commands.
• Minimize administrative effort
What should you include in the recommendation?
- A. Azure Container instances
- B. Azure Kubernetes Service (AKS)
- C. Azure Container Registry Correct
- D. Azure Files
Explanation
Azure Container Registry is the correct choice as it provides a private registry for storing custom container images and supports Docker commands. It minimizes administrative effort by managing storage, scaling, and security of container images.
Your network contains an Active Directory Domain Services (AD DS) domain. The domain contains a server named Server1 that runs Windows Server 2022.
You need to manage Storage Quality of Service (QoS) from Server1.
Which Remote Server Administration Tools (RSAT) feature should you install?
- A. RSAT: Failover Clustering Tools Correct
- B. RSAT: File Services Tools
- C. RSAT: Storage Replica Module for Windows PowerShell
- D. RSAT: Data Center Bridging LLDP Tools
Explanation
Storage QoS is managed by a Policy Manager that runs as a resource of the Scale-Out File Server failover cluster. Its cmdlets (for example Get-StorageQosFlow and New-StorageQosPolicy) are in the Failover Clustering PowerShell module, which is installed with RSAT: Failover Clustering Tools (Add-WindowsFeature RSAT-Clustering). RSAT: File Services Tools manage file services such as DFS and FSRM, not Storage QoS. The Storage Replica module manages replication. The Data Center Bridging LLDP tools manage DCB network settings.
You have a server named Server1 that runs Windows Server, has the File Server Resource Manager role service installed, and contains the volumes shown in the following table.
| Letter | File system |
|---|---|
| C | NTFS |
| D | ExFAT |
| E | ReFS |
| F | NTFS |
You plan to configure file screens on Server1.
On which volumes can you configure a file screen?
- A. C, D, E, and F
- B. F only
- C. C and F only Correct
- D. C, E and F only
- E. E and F only
Explanation
File Server Resource Manager, including file screening, supports only volumes formatted with NTFS. It does not support the Resilient File System (ReFS), and it does not work on exFAT volumes either. Volumes C and F are NTFS, so you can configure file screens on them. Volume D (exFAT) and volume E (ReFS) cannot have file screens.
You have three on-premises servers named SVR1, SVR2, and SVR3 that run Windows Server. SRV1 has a direct-attached storage (DAS) array.
You plan to deploy a failover cluster named Cluster1 by using SVR2 and SVR3.
You need to ensure that the DAS array on SRV1 can be used as shared storage for Cluster1. The solution must ensure that Cluster1 has block-level access to the storage.
What should you do first on SRV1?
- A. Run the start-service -name msiscsi cmdlet.
- B. Install the iSCSI Target Server role service. Correct
- C. Install the File Server role service.
- D. Run the Enable-ClusterStorageSpacesDirect cmdlet.
Explanation
To use the DAS array on SRV1 as shared storage for Cluster1 with block-level access, you must first install the iSCSI Target Server role service on SRV1. This allows SRV1 to act as an iSCSI target, making its local storage accessible to other servers in the cluster over the network.
You have an on-premises server that runs Windows Server and contains a file share named Share1.
You have an Azure subscription that contains an Azure Files share named azshare1 and an Azure File Sync instance named Sync1. Sync1 syncs Share1 with azshare1.
You need to delete Sync1.
Which four resources should you delete in sequence? To answer, move the appropriate resources from the list of resources to the answer area and arrange them in the correct order.
Explanation
An Azure File Sync Storage Sync Service cannot be deleted while it still contains sync groups, and a sync group cannot be deleted while it still contains endpoints. Work from the inside out: 1. Delete the server endpoint, which stops syncing Share1 on the on-premises server. 2. Delete the cloud endpoint, which disconnects azshare1 from the sync group (the Azure file share itself is kept). 3. Delete the now-empty sync group. 4. Delete Sync1, the Storage Sync Service (after the server is unregistered from it). The management group is unrelated to Azure File Sync, and deleting azshare1 is not required to remove Sync1.
You have an Azure subscription that contains an Azure Files share named share1.
You need to ensure that users can view and restore previous versions of the files stored in share1. The solution must minimize administrative effort.
What should you do?
- A. Create share snapshots. Correct
- B. Configure a point-in-time restore for the storage account that hosts share1.
- C. Enable soft delete for Azure Files.
- D. Configure a Recovery Services vault in Azure Backup.
Explanation
Azure Files share snapshots are read-only, point-in-time copies of the share. On a Windows client with the SMB share mounted, users can open a file or folder's Properties > Previous Versions tab to see the share snapshots and open or restore earlier versions themselves, just like Volume Shadow Copy snapshots on a Windows file server. Soft delete only protects an entire file share from accidental deletion and does not keep earlier versions of individual files. Point-in-time restore applies to block blobs, not Azure Files. Azure Backup for Azure Files also works by taking share snapshots, but configuring a Recovery Services vault and backup policy is more administrative effort than simply creating snapshots.
You need to meet the technical requirements for Server1.
Which users can currently perform the required tasks?
- A. Admin3 only
- B. Admin1 and Admin3 only Correct
- C. Admin1 only
- D. Admin1, Admin2, and Admin3
Explanation
Admin1 can perform the required tasks because being part of the Enterprise Admins group grants administrative privileges across all domains in the forest. Admin3, as a member of the Canada domain's administrators, also has the necessary permissions to perform the required tasks.
You need to meet the technical requirements for the site links.
Which users can perform the required tasks?
- A. Admin1, Admin2, and Admin3
- B. Admin1 and Admin3 only
- C. Admin1 only Correct
- D. Admin1 and Admin2 only
- E. Admin3 only
Explanation
According to Microsoft documentation, only an Enterprise Admin or a Domain Admin in the forest root domain can modify site links. This aligns with option C, indicating that Admin1, who presumably holds such a role, is the correct choice.
You need to meet the technical requirements for User1. The solution must use the principle of least privilege.
What should you do?
- A. Add Users1 to the Server Operators group in contoso.com.
- B. Create a delegation on contoso.com.
- C. Add Users1 to the Account Operators group in contoso.com.
- D. Create a delegation on OU3. Correct
Explanation
Creating a delegation on OU3 allows User1 to manage the membership of all groups within that specific organizational unit while adhering to the principle of least privilege, as it restricts administrative rights to only necessary tasks and scope.
Which groups can you add to Group3 and Group5? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Hot Area:
Explanation
Group3: Group1, Group2, Group4, and Group5 only — Group3 is a universal group, and Active Directory allows a universal group to contain user accounts, computer accounts, global groups, and other universal groups from any domain in the forest, so every global and universal group in the environment (Group1, Group2, Group4, and Group5) is a valid member. The one nesting a universal group can never accept is a domain local group, so the option that also includes Group6 (the domain local group) is wrong, and the narrower choices such as "Group1 and Group2 only" needlessly exclude the global groups that are perfectly legal members.
Group5: Group4 only — Group5 is a global group, and a global group's membership is restricted to accounts and other global groups from its own domain; Group4 is the only other global group in that same domain, so it is the sole group that can be nested inside Group5. "Group2 and Group4 only" and "Group1 only" fail because universal groups cannot be nested into a global group, and "Group4 and Group6 only" fails because a domain local group can never be a member of a global group.
You need to meet the technical requirements for Server3.
Which users can perform the required tasks?
- A. Admin3 only
- B. Admin1 and Admin3 only
- C. Admin1 only Correct
- D. Admin1, Admin2, and Admin3
- E. Admin1 and Admin2 only
Explanation
Based on Microsoft documentation, authorizing a DHCP server in an environment with multiple AD DS domains requires an Enterprise Administrator account. In the given options, Admin1 is likely part of the Enterprise Admins group, making C the correct answer.
You need to meet the technical requirements for Server4.
Which cmdlets should you run on Server1 and Server4? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Hot Area:
Explanation
Server1: Select the correct cmdlet — Set-Item. Server1 is the management machine, and to manage a server that is not in the same Active Directory domain (a workgroup or otherwise non-trusted host such as Server4), the WinRM client on the managing computer must explicitly trust that host, which is done with Set-Item WSMan:\localhost\Client\TrustedHosts -Value "Server4" (add -Concatenate to preserve existing entries). Enable-PSRemoting on Server1 would only configure Server1 to *receive* remote connections, which does nothing for outbound trust of an untrusted remote host.
Server4: Select the correct cmdlet — Enable-PSRemoting. Server4 is the target being managed, so it needs the WinRM listener created, the WinRM service set to automatic start and running, and the firewall rules for Windows Remote Management opened — all of which Enable-PSRemoting -Force performs in one step. Start-Service WinRM would start the service but leave the listener and firewall exceptions unconfigured, and Enable-ServerManagerStandardUserRemoting only grants non-administrator users the rights to view remote data, which is not what enables the remote management connection itself.
You need to meet the technical requirements for VM1.
Which cmdlet should you run first? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Hot Area:
Explanation
Cmdlet selection (left dropdown): Set-VMProcessor — the requirement for VM1 is nested virtualization (running Hyper-V, and therefore a hypervisor-based workload, inside the guest), and that setting lives on the virtual machine's virtual processor, which is configured with Set-VMProcessor. Set-VM changes general VM properties such as memory or automatic start/stop actions, Set-VMFirmware and Set-VMBios control boot order and secure boot for generation 2 and generation 1 VMs respectively, and Set-VMHost configures the Hyper-V host itself rather than VM1's CPU, so none of them can expose the hardware virtualization features to the guest.
Parameter selection (right dropdown): -ExposeVirtualizationExtensions — passing this parameter with a value of $true on a powered-off VM projects the host CPU's hardware virtualization extensions (Intel VT-x / AMD-V) into VM1's virtual processor, which is exactly what the guest operating system needs before the Hyper-V role or any hypervisor-backed feature can be installed inside it. -GuestControlledCacheTypes and -EnableHostResourceProtection are also Set-VMProcessor parameters, but they deal with guest cache-type control and with throttling excessive VM activity that would harm the host, and -NewVMName simply renames a virtual machine, so none of them enable nested virtualization.
You need to meet the technical requirements for VM2.
What should you do?
- A. Implement shielded virtual machines.
- B. Enable the Guest services integration service.
- C. Implement Credential Guard.
- D. Enable enhanced session mode. Correct
Explanation
Enabling enhanced session mode on the Hyper-V host prevents a VMConnect user from taking over another user's session, ensuring security and privacy. This feature is specifically designed to address the scenario described in the question.
You need to meet the technical requirements for VM3.
On which volumes can you enable Data Deduplication?
- A. C and D only
- B. D only
- C. C, D, E, and F
- D. D and E only Correct
- E. D, E, and F only
Explanation
Data Deduplication can be enabled only on volumes that meet its requirements. The volume cannot be the system or boot volume, so C is excluded. It must be formatted with NTFS, or with ReFS on Windows Server 2019 or later. In the VM3 scenario, volumes D and E meet these requirements and volume F does not, so deduplication can be enabled on D and E only. Any option that includes C or F is therefore wrong, and "D only" leaves out volume E, which qualifies.
For each of the following statements, select Yes if the statement is true. Otherwise. select No.
NOTE: Each correct selection is worth one point.
Hot Area:
Explanation
Statement 1 (No): For domain accounts, the minimum password length comes from the Account Policies in the GPO linked at the domain level (the Default Domain Policy by default), or from a fine-grained password policy (PSO) that applies to the user or one of its global groups. A GPO linked to the OU that holds Admin1 does not change the policy for domain accounts. In this scenario, the policy that applies to Admin1 does not require 14 characters.
Statement 2 (No): Only one password policy is in effect for a domain account: a PSO that applies to the user, otherwise the domain-level policy. Settings are never combined from several policies. In this scenario, the policy that applies to User1 does not set a 10-character minimum.
Statement 3 (No): A local account on Server1 is checked against the Account Policies that apply to the Server1 computer, from GPOs that reach the computer or from its local security policy. PSOs never apply to local accounts. In this scenario, the effective policy on Server1 does not require eight characters.