Question
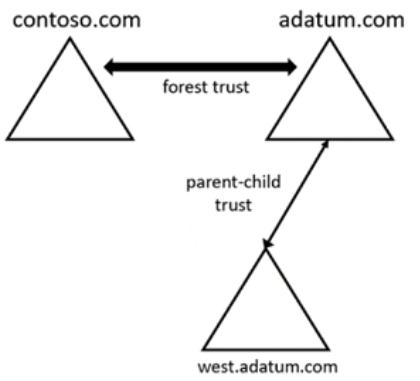
Your network contains two Active Directory Domain Services (AD DS) forests as shown in the following exhibit.
The forests contain the domain controllers shown in the following table.
You perform the following actions on DC1:
• Create a user named User1.
• Extend the schema with a new attribute named Attribute1.
To which domain controllers are User1 and Attribute1 replicated? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
| Name | Domain | Global catalog | Schema master |
| --- | --- | --- | --- |
| DC1 | adatum.com | Yes | Yes |
| DC2 | adatum.com | No | No |
| DC3 | west.adatum.com | Yes | No |
| DC4 | contoso.com | Yes | Yes |
Explanation
User1: DC2 and DC3 only — User1 is created in the adatum.com domain partition on DC1. A domain partition replicates to every domain controller in the same domain, so DC2 (adatum.com) receives a full copy. Global catalog servers in the same forest hold a partial, read-only copy of every object in the forest, so DC3 (a global catalog in west.adatum.com, a child domain of the adatum.com forest) also receives User1. DC4 is in the contoso.com forest; a forest trust allows authentication and resource access but never replicates directory objects between forests, so DC4 does not receive User1.
Attribute1: DC2 and DC3 only — The schema partition is shared by, and replicated to, every domain controller in the forest, whatever its domain or global catalog role. DC2 and DC3 are both in the adatum.com forest, so both receive Attribute1. DC4 belongs to the contoso.com forest, which has its own separate schema (DC4 is its schema master); a forest trust does not replicate schema changes, so DC4 does not receive Attribute1.
