Question
Your network contains an Active Directory Domain Services (AD DS) domain named adatum.com. The domain contains a file server named Server1 and three users named User1, User2, and User3.
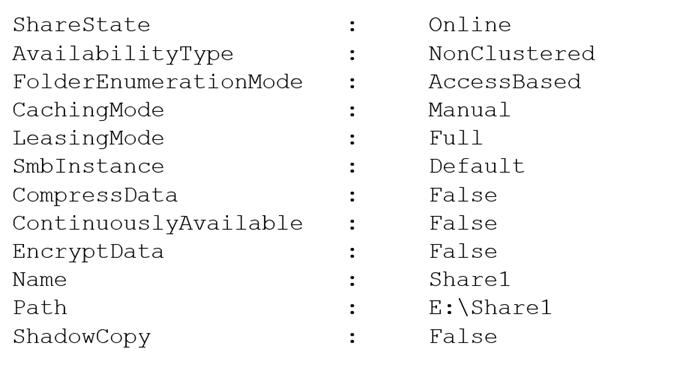
Server1 contains a shared folder named Share1 that has the configurations shown in the Share Configuration exhibit.
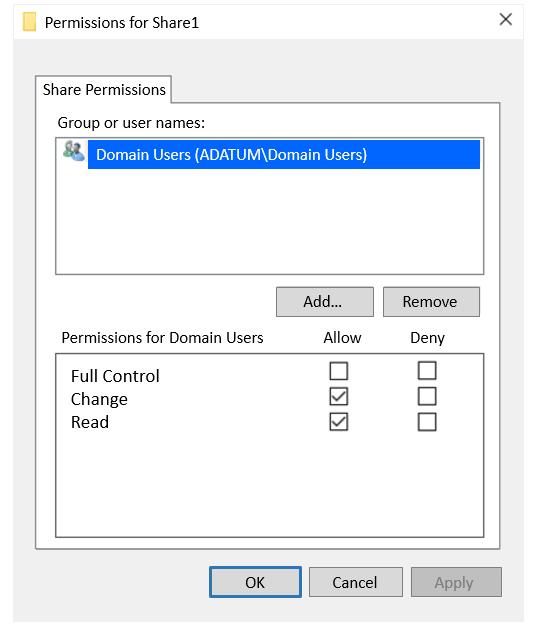
The share permissions for Share1 are configured as shown in the Share Permissions exhibit.
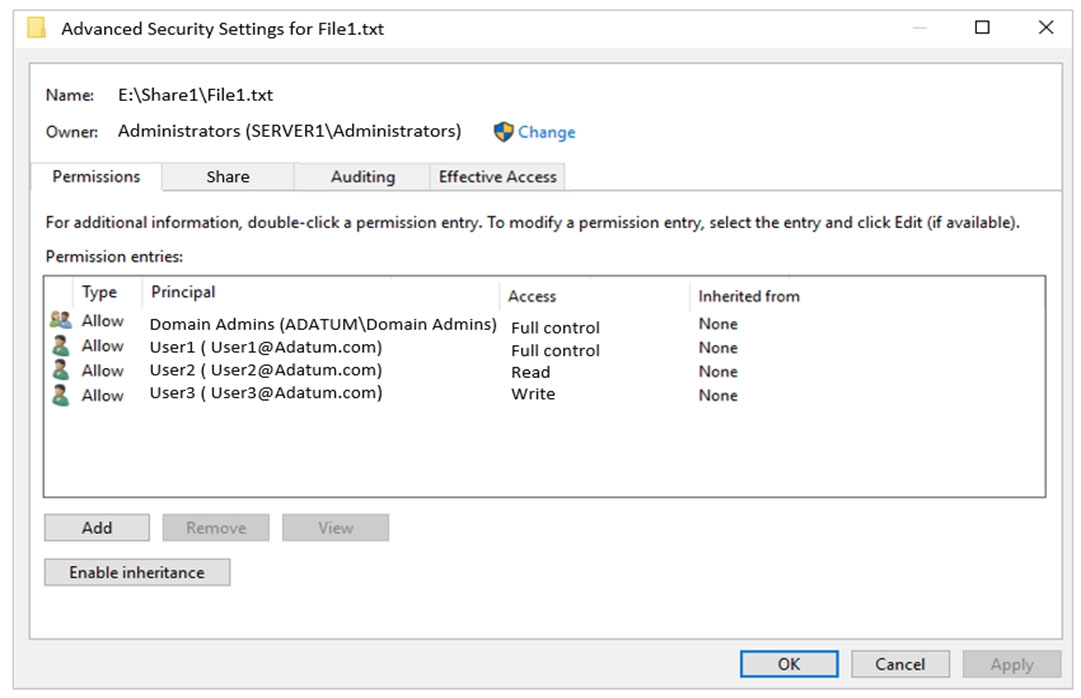
Share1 contains a file named File1.txt. The advanced security settings for File1.txt are configured as shown in the File Permissions exhibit.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Explanation
Statement 1 (No): When a file is reached through a share, the effective access is the more restrictive of the share permission and the NTFS permission. Domain Users have only Change (and Read) on Share1. Taking ownership requires the Take ownership right, which only the Full Control share permission passes through, so User1's NTFS Full Control is limited by the share and User1 cannot take ownership over the network. Statement 2 (Yes): Share1 uses access-based enumeration (FolderEnumerationMode is AccessBased), which hides only the files and folders a user has no permission to access. User2 has the NTFS Read permission on File1.txt and the share allows Read, so File1.txt is listed. Statement 3 (Yes): User3 has an explicit NTFS Write permission on File1.txt and the share allows Change, so User3 has permissions on the file and access-based enumeration does not hide it. User3 can see File1.txt, although Write alone does not let User3 open the file to read its contents.
