Question
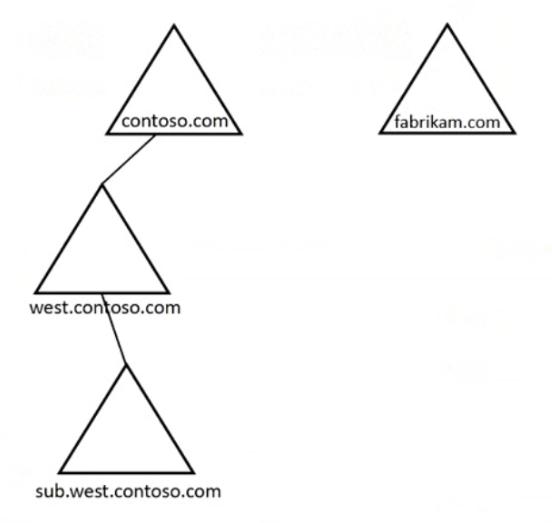
Your network contains the domains shown in the following exhibit.
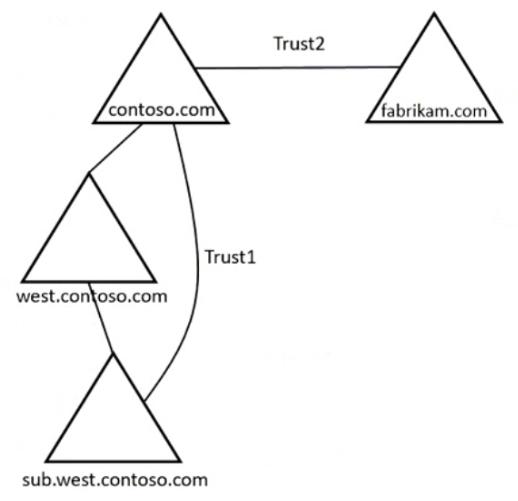
You need to establish trust relationships as shown in the following exhibit.
Which type of trust can you use for Trust1 and Trust2? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Explanation
Trust1: Shortcut trust only — Trust1 links two domains that already belong to the same Active Directory forest, and inside a single forest every domain is already connected by automatic two-way transitive parent-child and tree-root trusts, so the only trust an administrator can create there is a shortcut (cross-link) trust, which shortens the referral path between two domains in different branches of the same forest. Forest trust and external trust are not available options here because both are designed to join separate forests or separate domains outside the forest, and Active Directory will not let you create them between two domains that share a forest.
Trust2: Forest trust or external trust only — Trust2 crosses a forest boundary, connecting a domain in one forest to a domain in another forest, and that scenario supports either a forest trust (created between the two forest root domains, transitive across all domains in both forests, and requiring both forests to be at Windows Server 2003 or higher forest functional level) or an external trust (a non-transitive trust between two specific domains, which also works when the other side is an NT 4.0-style or otherwise non-forest-trust-capable domain). A shortcut trust cannot be used because shortcut trusts are only valid between domains within a single forest.
