Question
Your network contains an on-premises Active Directory domain that syncs to an Azure Active Directory (Azure AD) tenant. The tenant contains the users shown in the following table.
| Name | Type | Directory synced |
|---|---|---|
| User1 | User | No |
| User2 | User | Yes |
| User3 | Guest | No |
All the users work remotely.
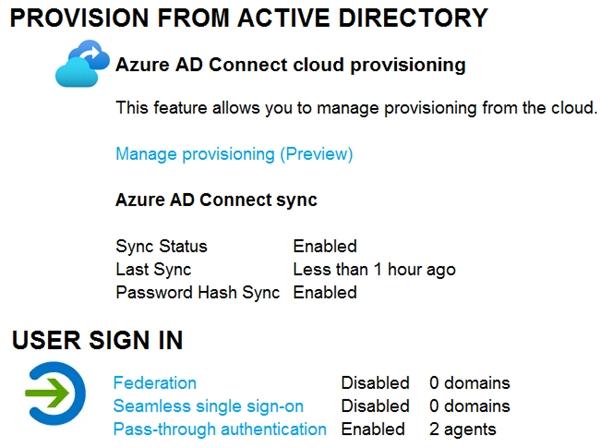
Azure AD Connect is configured in Azure AD as shown in the following exhibit.
Connectivity from the on-premises domain to the internet is lost.
Which users can sign in to Azure AD?
- A. User1 and User3 only Correct
- B. User1 only
- C. User1, User2, and User3
- D. User1 and User2 only
Explanation
User sign-in uses pass-through authentication, so synced users such as User2 are validated by the on-premises agents, which cannot be reached once the domain loses internet connectivity. Password hash sync is enabled, but it is not an automatic fallback for pass-through authentication; an administrator would have to switch the sign-in method manually. User1 is a cloud-only account and User3 is a guest authenticated by their own home identity provider, so neither depends on the on-premises domain and both can still sign in.
