Question
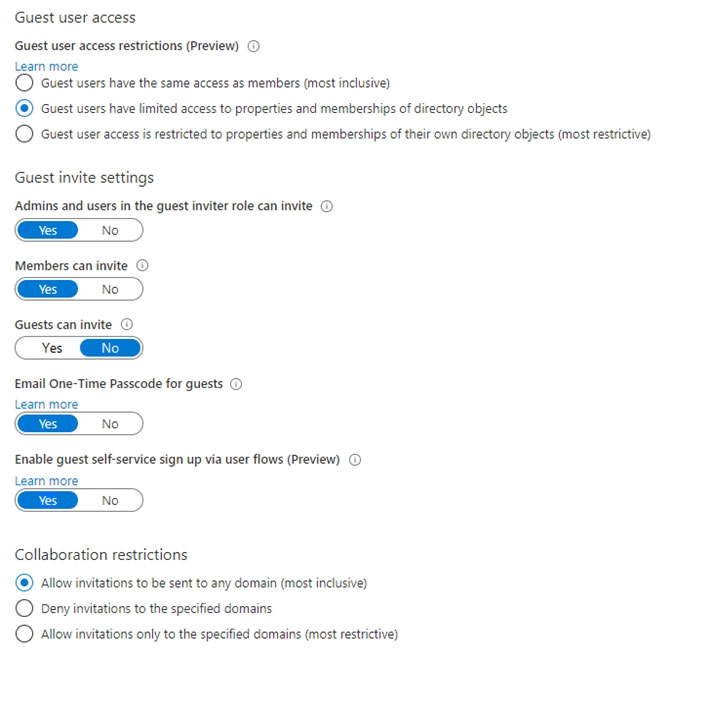
You have a Microsoft 365 tenant that uses the domain named fabrikam.com. The Guest invite settings for Azure Active Directory (Azure AD) are configured as shown in the exhibit.
A user named Admin1@fabrikam.com shares a Microsoft SharePoint Online document library to the users shown in the following table.
| Name | Email | Description |
|---|---|---|
| User1 | User1@contoso.com | A guest user in fabrikam.com |
| User2 | User2@outlook.com | A user who has never accessed resources in fabrikam.com |
| User3 | User3@fabrkam.com | A user in fabrikam.com |
Which users will be emailed a passcode?
- A. User2 only Correct
- B. User1 only
- C. User1 and User2 only
- D. User1, User2, and User3
Explanation
With Email One-Time Passcode for guests set to Yes and invitations allowed to any domain, a passcode is the fallback sign-in method for a new external recipient who redeems a share and has no other way to authenticate. User2 has never accessed resources in fabrikam.com, so User2 is the only recipient who goes through first-time redemption, and the one emailed a passcode. User1 is already a guest in fabrikam.com. Existing guests are past redemption and keep the sign-in method they used when they first redeemed, so User1 is not sent a passcode. User3 is an internal fabrikam.com user who signs in with an organizational account, so User3 doesn't need one either. In practice a passcode is sent only when the recipient has no Microsoft Entra account, Microsoft account or federated account, so an address that already has a Microsoft account signs in with that account instead.
