Question
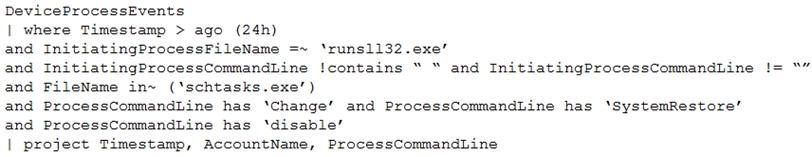
You have the following advanced hunting query in Microsoft 365 Defender.
You need to receive an alert when any process disables System Restore on a device managed by Microsoft Defender during the last 24 hours.
Which two actions should you perform? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
- A. Create a detection rule. Correct
- B. Create a suppression rule.
- C. Add | order by Timestamp to the query.
- D. Replace DeviceProcessEvents with DeviceNetworkEvents.
- E. Add DeviceId and ReportId to the output of the query. Correct
Explanation
To get alerts from an advanced hunting query you create a custom detection rule from it. For Defender for Endpoint tables, the rule's query must return Timestamp, DeviceId and ReportId so alerts can be tied to the device and the original event, and the current project line returns only Timestamp, AccountName and ProcessCommandLine. A suppression rule hides alerts instead of creating them, sorting the output does not matter, and process creation is recorded in DeviceProcessEvents, not DeviceNetworkEvents.
