Question
Your company uses Microsoft Defender for Cloud and Microsoft Sentinel.
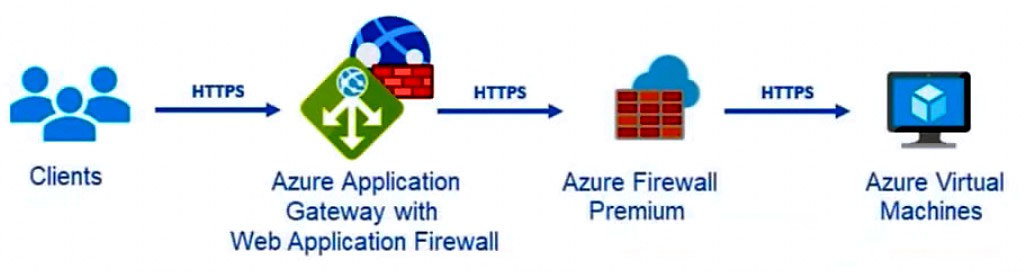
The company is designing an application that will have the architecture shown in the following exhibit.
You are designing a logging and auditing solution for the proposed architecture. The solution must meet the following requirements:
✑ Integrate Azure Web Application Firewall (WAF) logs with Microsoft Sentinel.
✑ Use Defender for Cloud to review alerts from the virtual machines.
What should you include in the solution? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Hot Area:
Explanation
For WAF: Data connectors. Microsoft Sentinel ingests Azure Web Application Firewall logs from Application Gateway through the Azure Web Application Firewall (WAF) data connector, which streams the WAF diagnostic logs to the Sentinel workspace. The Azure Diagnostics extension and Network Watcher do not bring WAF logs into Sentinel, and workflow automation responds to alerts rather than collecting logs.
For the virtual machines: The Log Analytics agent. Defender for Cloud collects security data from virtual machines through the Log Analytics agent (now replaced by the Azure Monitor Agent), which sends the events it needs to generate and display alerts for the VMs. The Azure Diagnostics extension sends guest metrics to storage or Azure Monitor metrics rather than providing Defender for Cloud alerting, Storage Analytics applies to storage accounts, and data connectors are a Sentinel feature.
