Your company has a Microsoft 365 E5 subscription.
The Chief Compliance Officer plans to enhance privacy management in the working environment.
You need to recommend a solution to enhance the privacy management. The solution must meet the following requirements:
✑ Identify unused personal data and empower users to make smart data handling decisions.
✑ Provide users with notifications and guidance when a user sends personal data in Microsoft Teams.
✑ Provide users with recommendations to mitigate privacy risks.
What should you include in the recommendation?
A.communication compliance in insider risk management
B.Microsoft Viva Insights
C.Privacy Risk Management in Microsoft PrivaCorrect
D.Advanced eDiscovery
Explanation
Privacy Risk Management in Microsoft Priva allows for the identification of unused personal data and provides users with notifications and guidance on handling personal data securely, including mitigating privacy risks when sending data via Microsoft Teams.
You have an Azure subscription that has Microsoft Defender for Cloud enabled.
Suspicious authentication activity alerts have been appearing in the Workload protections dashboard.
You need to recommend a solution to evaluate and remediate the alerts by using workflow automation. The solution must minimize development effort.
What should you include in the recommendation?
A.Azure Monitor webhooks
B.Azure Event Hubs
C.Azure Functions apps
D.Azure Logics AppsCorrect
Explanation
Azure Logic Apps is the appropriate choice for automating workflows in response to suspicious activity alerts from Microsoft Defender for Cloud, as it supports integration with security services and enables automated remediation steps without requiring extensive development effort.
Your company is moving a big data solution to Azure.
The company plans to use the following storage workloads:
- Azure Storage blob containers
- Azure Data Lake Storage Gen2
- Azure Storage file shares
- Azure Disk Storage
Which two storage workloads support authentication by using Azure Active Directory (Azure AD)? Each correct answer presents a complete solution.
NOTE: Each correct selection is worth one point.
A.Azure Storage file shares
B.Azure Disk Storage
C.Azure Storage blob containersCorrect
D.Azure Data Lake Storage Gen2Correct
Explanation
Azure Storage blob containers support Azure AD (Microsoft Entra ID) authorization natively: security principals and managed identities get OAuth tokens and are authorized with Azure RBAC roles such as Storage Blob Data Reader. Azure Data Lake Storage Gen2 is built on Blob Storage and supports the same Azure AD authorization, with POSIX-style ACLs on top. Azure Storage file shares are accessed mainly over SMB, where identity-based access depends on AD DS, Microsoft Entra Domain Services or Microsoft Entra Kerberos rather than direct Azure AD authorization. Azure Disk Storage is attached to virtual machines and is not accessed through Azure AD-authorized data requests.
Your company is migrating data to Azure. The data contains Personally Identifiable Information (PII).
The company plans to use Microsoft Information Protection for the PII data store in Azure.
You need to recommend a solution to discover PII data at risk in the Azure resources.
What should you include in the recommendation? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Hot Area:
Explanation
To connect the Azure data sources to Microsoft Information Protection: Azure Purview (now Microsoft Purview). The Microsoft Purview Data Map scans Azure data sources such as Azure Storage and Azure SQL Database, classifies the data it finds, and applies the Microsoft Information Protection sensitivity labels and sensitive information types, so PII stored in Azure is discovered and labeled. Endpoint data loss prevention covers devices, not Azure data stores, and Defender for Cloud Apps governs SaaS apps.
To triage security alerts related to resources that contain PII data: Microsoft Defender for Cloud. Its data-aware security posture uses the sensitivity information discovered in your Azure resources, so alerts on storage and databases show whether the resource holds sensitive data and can be prioritized accordingly. Azure Monitor collects telemetry but does not provide security alert triage, and Defender for Cloud Apps focuses on cloud app usage rather than Azure resources.
You have a Microsoft 365 E5 subscription and an Azure subscription.
You are designing a Microsoft deployment.
You need to recommend a solution for the security operations team. The solution must include custom views and a dashboard for analyzing security events.
What should you recommend using in Microsoft Sentinel?
A.notebooks
B.playbooks
C.workbooksCorrect
D.threat intelligence
Explanation
Workbooks in Microsoft Sentinel provide a flexible canvas for creating custom views and dashboards to analyze security events, which is what the security operations team needs. Notebooks are for hunting and investigation with Jupyter, playbooks automate responses with Logic Apps, and threat intelligence manages indicators of compromise.
Your company has a Microsoft 365 subscription and uses Microsoft Defender for Identity.
You are informed about incidents that relate to compromised identities.
You need to recommend a solution to expose several accounts for attackers to exploit. When the attackers attempt to exploit the accounts, an alert must be triggered.
Which Defender for Identity feature should you include in the recommendation?
A.sensitivity labels
B.custom user tags
C.standalone sensors
D.honeytoken entity tagsCorrect
Explanation
Honeytoken entity tags are designed to act as traps for malicious actors. When an attacker attempts to exploit a honeytoken-tagged account, Defender for Identity triggers an alert.
Your company is moving all on-premises workloads to Azure and Microsoft 365.
You need to design a security orchestration, automation, and response (SOAR) strategy in Microsoft Sentinel that meets the following requirements:
✑ Minimizes manual intervention by security operation analysts
✑ Supports triaging alerts within Microsoft Teams channels
What should you include in the strategy?
A.KQL
B.playbooksCorrect
C.data connectors
D.workbooks
Explanation
Playbooks in Microsoft Sentinel are Azure Logic Apps workflows that run automatically from automation rules in response to alerts and incidents, which minimizes manual intervention by security operations analysts. Through the Microsoft Teams connector, a playbook can post an alert or incident to a Teams channel and let analysts triage it there. KQL, data connectors and workbooks query, ingest and visualize data but do not automate responses.
You have an Azure subscription that contains virtual machines, storage accounts, and Azure SQL databases.
All resources are backed up multiple times a day by using Azure Backup.
You are developing a strategy to protect against ransomware attacks.
You need to recommend which controls must be enabled to ensure that Azure Backup can be used to restore the resources in the event of a successful ransomware attack.
Which two controls should you include in the recommendation? Each correct answer presents a complete solution.
NOTE: Each correct selection is worth one point.
A.Enable soft delete for backups.Correct
B.Require PINs for critical operations.Correct
C.Encrypt backups by using customer-managed keys (CMKs).
D.Perform offline backups to Azure Data Box.
E.Use Azure Monitor notifications when backup configurations change.
Explanation
Enable soft delete for backups: if an attacker deletes backup data, Azure Backup keeps it for 14 more days, so the backup items can still be recovered with no data loss.
Require PINs for critical operations: Azure Backup's security features require a security PIN, generated in the Azure portal, before critical operations such as stopping protection with data deletion or changing a passphrase. An attacker with stolen credentials therefore cannot easily destroy or tamper with online backups.
Customer-managed keys control who manages the encryption keys, but they do not stop backups from being deleted. Offline backup to Azure Data Box is only an initial seeding method, and Azure Monitor notifications only alert you to changes; neither guarantees that the backups can be restored.
You are creating the security recommendations for an Azure App Service web app named App1. App1 has the following specifications:
✑ Users will request access to App1 through the My Apps portal. A human resources manager will approve the requests.
✑ Users will authenticate by using Azure Active Directory (Azure AD) user accounts.
You need to recommend an access security architecture for App1.
What should you include in the recommendation? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Hot Area:
Explanation
To enable Azure AD authentication for App1, use: Azure AD application. Registering App1 as an application in Azure AD (Microsoft Entra ID), for example through App Service authentication, lets users sign in with their Azure AD accounts and makes the app available as a tile in the My Apps portal. Application Proxy is for publishing on-premises apps, Application Gateway is a load balancer, and a managed identity lets the app itself authenticate to other resources, not users to the app.
To implement access requests for App1, use: An access package in Identity Governance. Entitlement management access packages let users request access in the My Apps portal and route each request through an approval policy, so a human resources manager can approve it. An access review recertifies existing access rather than handling new requests, and the Defender for Cloud Apps and Conditional Access App Control options control sessions, not access requests.
Your company uses Microsoft Defender for Cloud and Microsoft Sentinel.
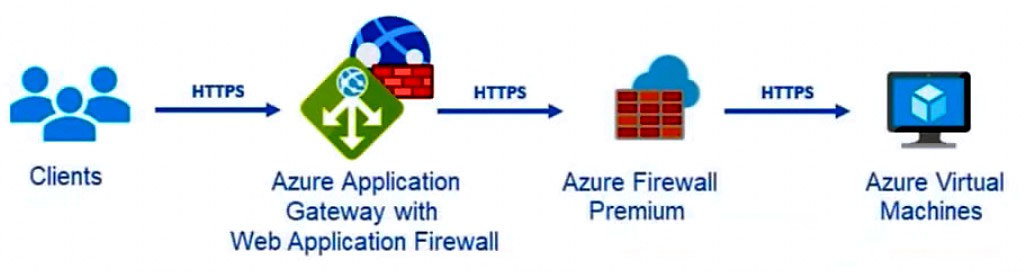
The company is designing an application that will have the architecture shown in the following exhibit.
You are designing a logging and auditing solution for the proposed architecture. The solution must meet the following requirements:
✑ Integrate Azure Web Application Firewall (WAF) logs with Microsoft Sentinel.
✑ Use Defender for Cloud to review alerts from the virtual machines.
What should you include in the solution? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Hot Area:
Explanation
For WAF: Data connectors. Microsoft Sentinel ingests Azure Web Application Firewall logs from Application Gateway through the Azure Web Application Firewall (WAF) data connector, which streams the WAF diagnostic logs to the Sentinel workspace. The Azure Diagnostics extension and Network Watcher do not bring WAF logs into Sentinel, and workflow automation responds to alerts rather than collecting logs.
For the virtual machines: The Log Analytics agent. Defender for Cloud collects security data from virtual machines through the Log Analytics agent (now replaced by the Azure Monitor Agent), which sends the events it needs to generate and display alerts for the VMs. The Azure Diagnostics extension sends guest metrics to storage or Azure Monitor metrics rather than providing Defender for Cloud alerting, Storage Analytics applies to storage accounts, and data connectors are a Sentinel feature.
Your company has a third-party security information and event management (SIEM) solution that uses Splunk and Microsoft Sentinel.
You plan to integrate Microsoft Sentinel with Splunk.
You need to recommend a solution to send security events from Microsoft Sentinel to Splunk.
What should you include in the recommendation?
A.a Microsoft Sentinel data connector
B.Azure Event HubsCorrect
C.a Microsoft Sentinel workbook
D.Azure Data Factory
Explanation
Use Azure Event Hubs. A Log Analytics data export rule on the Microsoft Sentinel workspace streams new data from selected tables (for example SecurityIncident, SecurityAlert or SecurityEvent) to an event hub as it arrives, and Splunk reads the event hub by using the Splunk Add-on for Microsoft Cloud Services.
Microsoft Sentinel data connectors bring data into Sentinel; they do not send data out. Workbooks only visualize data, and Azure Data Factory is a batch data integration service, not a way to stream security events to a SIEM.
A customer follows the Zero Trust model and explicitly verifies each attempt to access its corporate applications.
The customer discovers that several endpoints are infected with malware.
The customer suspends access attempts from the infected endpoints.
The malware is removed from the endpoints.
Which two conditions must be met before endpoint users can access the corporate applications again? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
A.The client access tokens are refreshed.Correct
B.Microsoft Intune reports the endpoints as compliant.Correct
C.A new Azure Active Directory (Azure AD) Conditional Access policy is enforced.
D.Microsoft Defender for Endpoint reports the endpoints as compliant.
Explanation
Defender for Endpoint gives each device a risk level and sends it to Intune. Intune compares that risk level with the device compliance policy and marks the device compliant or noncompliant. Conditional Access then uses this Intune compliance state to allow or block access. When the malware has been removed, Defender for Endpoint lowers the device's risk level, so Intune reports the device as compliant again (B). Conditional Access is checked when a token is issued, so the client must refresh its access tokens (A). The new tokens are issued against the device's compliant state, and only then can users reach the apps again. Defender for Endpoint does not report compliance itself (it reports risk), so D is wrong. No new Conditional Access policy is needed because the existing policy already allows compliant devices, so C is wrong.
You have a Microsoft 365 subscription and an Azure subscription. Microsoft 365 Defender and Microsoft Defender for Cloud are enabled.
The Azure subscription contains a Microsoft Sentinel workspace. Microsoft Sentinel data connectors are configured for Microsoft 365, Microsoft 365 Defender,
Defender for Cloud, and Azure.
You plan to deploy Azure virtual machines that will run Windows Server.
You need to enable extended detection and response (EDR) and security orchestration, automation, and response (SOAR) capabilities for Microsoft Sentinel.
How should you recommend enabling each capability? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Hot Area:
Explanation
EDR: Onboard the servers to Defender for Cloud. Enabling Microsoft Defender for Servers on the Azure virtual machines deploys the integrated Microsoft Defender for Endpoint sensor, which provides endpoint detection and response; the resulting alerts already reach Microsoft Sentinel through the existing Defender for Cloud and Microsoft 365 Defender connectors. Azure Arc is only needed for servers outside Azure, and the Azure AD and Defender for Cloud Apps connectors bring identity and SaaS data, not endpoint detection.
SOAR: Configure Microsoft Sentinel playbooks. Playbooks are Azure Logic Apps workflows that Microsoft Sentinel runs from automation rules to respond to incidents and alerts, which is its security orchestration, automation, and response capability. Analytics rules detect threats rather than automate responses, and regulatory compliance standards and workflow automation in Defender for Cloud are not SOAR capabilities of Microsoft Sentinel.
You have a customer that has a Microsoft 365 subscription and uses the Free edition of Azure Active Directory (Azure AD).
The customer plans to obtain an Azure subscription and provision several Azure resources.
You need to evaluate the customer's security environment.
What will necessitate an upgrade from the Azure AD Free edition to the Premium edition?
A.Azure AD Privileged Identity Management (PIM)Correct
B.role-based authorization
C.resource-based authorization
D.Azure AD Multi-Factor Authentication
Explanation
Privileged Identity Management (PIM) requires Microsoft Entra ID P2 (formerly Azure AD Premium P2). Role-based and resource-based authorization are available in the Free edition, and multi-factor authentication can be enabled for free through security defaults, so only PIM forces an upgrade to a Premium edition.
You are designing the security standards for a new Azure environment.
You need to design a privileged identity strategy based on the Zero Trust model.
Which framework should you follow to create the design?
A.Microsoft Security Development Lifecycle (SDL)
B.Enhanced Security Admin Environment (ESAE)
C.Rapid Modernization Plan (RaMP)Correct
D.Microsoft Operational Security Assurance (OSA)
Explanation
The Rapid Modernization Plan (RaMP) is Microsoft's recommended approach for quickly adopting the privileged access strategy aligned with the Zero Trust model. The Security Development Lifecycle (SDL) covers secure software development and Operational Security Assurance (OSA) covers secure operation of online services, so neither is a privileged access framework. The Enhanced Security Admin Environment (ESAE) is a legacy approach that Microsoft has retired in favour of the modern privileged access strategy and RaMP.
A customer has a hybrid cloud infrastructure that contains a Microsoft 365 E5 subscription and an Azure subscription.
All on-premises servers in the perimeter network are prevented from connecting directly to the internet.
The customer recently recovered from a ransomware attack.
The customer plans to deploy Microsoft Sentinel.
You need to recommend solutions to meet the following requirements:
✑ Ensure that the security operations team can access the security logs and the operation logs.
✑ Ensure that the IT operations team can access only the operations logs, including the event logs of the servers in the perimeter network.
Which two solutions should you include in the recommendation? Each correct answer presents a complete solution.
NOTE: Each correct selection is worth one point.
A.a custom collector that uses the Log Analytics agent
B.the Azure Monitor agentCorrect
C.resource-based role-based access control (RBAC)Correct
D.Azure Active Directory (Azure AD) Conditional Access policies
Explanation
The Azure Monitor agent (B) collects the event logs from the on-premises servers, including those in the perimeter network, which can send their data through the Log Analytics gateway or a proxy because they cannot reach the internet directly. Data collection rules control which data goes to which workspace. Resource-context role-based access control (RBAC) (C) lets the security operations team read all security and operations logs in the workspace, while the IT operations team gets access only to the operations data for the resources they manage. The Log Analytics agent is retired, and Conditional Access controls sign-in, not access to log data.
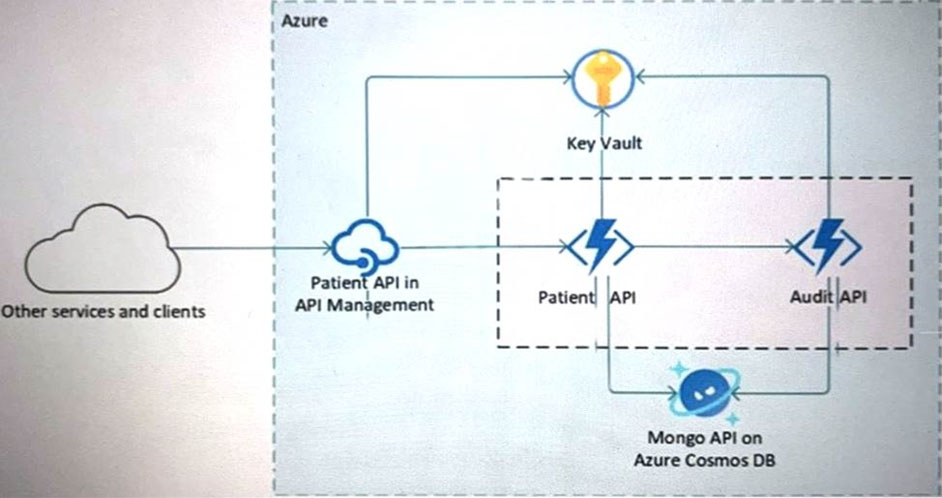
Your company is developing a serverless application in Azure that will have the architecture shown in the following exhibit.
[Diagram: External services connect to API Management, which routes to Key Vault, Patient API, and Audit API. Patient API and Audit API interact with Key Vault and Azure Cosmos DB.]
You need to recommend a solution to isolate the compute components on an Azure virtual network.
What should you include in the recommendation?
A.Azure Active Directory (Azure AD) enterprise applications
B.an Azure App Service Environment (ASE)Correct
C.Azure service endpoints
D.an Azure Active Directory (Azure AD) application proxy
Explanation
An Azure App Service Environment (ASE) allows for hosting web apps, mobile apps, and functions within an isolated subnet of a virtual network in Azure, providing secure network access and isolation r required by the architecture.
You are planning the security levels for a security access strategy.
You need to identify which job roles to configure at which security levels. The solution must meet security best practices of the Microsoft Cybersecurity Reference Architectures (MCRA).
Which security level should you configure for each job role? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Explanation
Developer: Specialized security. In Microsoft's privileged access strategy (part of MCRA), specialized security provides increased controls for roles with elevated business impact, such as developers and those who handle sensitive data or systems.
Standard user: Enterprise security. Enterprise security is the baseline level for all users and productivity scenarios, using standard controls such as MFA and compliant devices.
IT administrator: Privileged security. Privileged security is the highest level, for IT administrators and other roles that can cause a significant incident through control of systems, typically with privileged access workstations and just-in-time access.
Your company plans to apply the Zero Trust Rapid Modernization Plan (RaMP) to its IT environment.
You need to recommend the top three modernization areas to prioritize as part of the plan.
Which three areas should you recommend based on RaMP? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
A.data, compliance, and governanceCorrect
B.infrastructure and development
C.user access and productivityCorrect
D.operational technology (OT) and IoT
E.modern security operationsCorrect
Explanation
The Zero Trust Rapid Modernization Plan (RaMP) puts three initiatives first: user access and productivity (C), data, compliance, and governance (A), and modern security operations (E). These give the quickest Zero Trust and ransomware-resilience gains: verifying identities and devices explicitly, protecting and governing sensitive data, and unifying detection and response. Operational technology (OT) and IoT, and datacenter/infrastructure and development, are later, optional RaMP initiatives that depend on the needs of the organization.
For a Microsoft cloud environment, you are designing a security architecture based on the Microsoft Cybersecurity Reference Architectures (MCRA).
You need to protect against the following external threats of an attack chain:
• An attacker attempts to exfiltrate data to external websites.
• An attacker attempts lateral movement across domain-joined computers.
What should you include in the recommendation for each threat? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Explanation
An attacker attempts to exfiltrate data to external websites: Microsoft Defender for Cloud Apps. As a cloud access security broker it discovers and controls the use of cloud apps and websites, and its session and file policies detect and block uploads of sensitive data to unsanctioned external destinations.
An attacker attempts lateral movement across domain-joined computers: Microsoft Defender for Identity. It monitors on-premises Active Directory domain controller signals and detects lateral movement techniques such as pass-the-hash, pass-the-ticket and lateral movement paths between domain-joined computers. Defender for Office 365 protects email and collaboration, not these attack stages.
Verifying access...
Access Required
You need to purchase this exam to access practice mode
Unlock a few more questions every day for 300 points you earn free on
Godlike Academy. Everything you unlock with the Daily Climb stays open for 7 days after your last unlock.