Question
You have an Azure virtual network named Vnet1 and an on-premises network. The on-premises network has policy-based VPN devices.
In Vnet1, you deploy a virtual network gateway named GW1 that uses a SKU of VpnGw1 and is route-based.
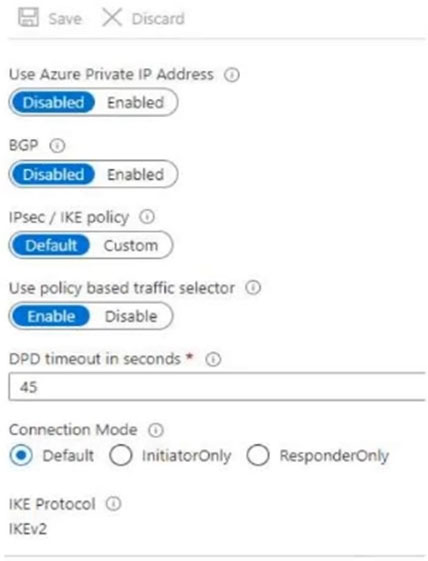
You have a Site-to-Site VPN connection for GW1 as shown in the following exhibit.
You need to ensure that the on-premises network can connect to the route-based GW1.
What should you do before you create the connection?
- A. Set Connection Mode to ResponderOnly.
- B. Set BGP to Enabled.
- C. Set Use Azure Private IP Address to Enabled.
- D. Set IPsec / IKE policy to Custom. Correct
Explanation
A route-based gateway connects to policy-based on-premises devices by enabling policy-based traffic selectors on the connection, and that option is part of a custom IPsec/IKE policy: you must specify the complete policy (algorithms, key strengths and SA lifetimes). The exhibit already enables Use policy based traffic selector but leaves IPsec / IKE policy at Default, so it must be set to Custom. Enabling BGP, changing the connection mode or using the Azure private IP address does nothing to match the policy-based device's traffic selectors.
