Question
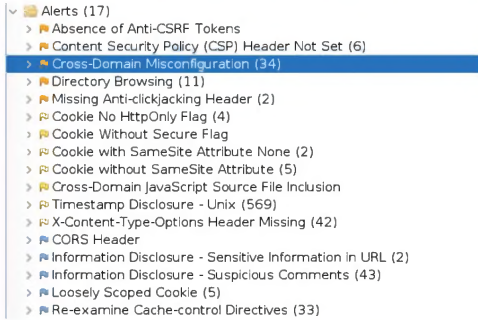
An organization conducted a web application vulnerability assessment against the corporate website, and the following output was observed:
Which of the following tuning recommendations should the security analyst share?
- A. Set an HttpOnly flag to force communication by HTTPS
- B. Block requests without an X-Frame-Options header
- C. Configure an Access-Control-Allow-Origin header to authorized domains Correct
- D. Disable the cross-origin resource sharing header
Explanation
The most frequent finding in the scan is Cross-Domain Misconfiguration (34 instances), which means the site's CORS policy, usually an Access-Control-Allow-Origin header set to *, lets any origin read its responses. Restricting Access-Control-Allow-Origin to an allowlist of authorized domains fixes this while keeping legitimate cross-origin use working. HttpOnly stops scripts from reading cookies and does not force HTTPS (that is the Secure flag), X-Frame-Options is a response header the server sends rather than something to require on requests, and disabling CORS entirely would break legitimate cross-origin access.
